Vulnerabilities in pkg:maven/io.github.skylot/jadx-core
PACKAGEGHSA-hvp5-5x4f-33fq is a LOW (CVSS 3.3) jadx file override vulnerability vulnerability (CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')) affecting Jadx core libraries in the Maven ecosystem. The issue involves jadx file override vulnerability. Remediation is available by upgrading affected packages to version 1.5.0.
pkg:maven/io.github.skylot/jadx-core
Vulnerability advisories affecting package pkg:maven/io.github.skylot/jadx-core. Select an advisory below to view technical details or fixes.
| Advisory ID | CVE / NVD | Severity | Summary |
|---|---|---|---|
| GHSA-hvp5-5x4f-33fq | - | LOW | JADX file override vulnerability |
| GHSA-fjh6-p566-wr6q | - | MODERATE | skylot jadx affected by Incorrect Behavior Order in vulnerable dependency |
| GHSA-r8j4-96mx-rjcc | CVE-2022-0219 | MODERATE | Improper Restriction of XML External Entity Reference in skylot/jadx |
GHSA-hvp5-5x4f-33fq at a Glance
Security Impact
CVSS: 3.3
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N).
How to Fix GHSA-hvp5-5x4f-33fq
To remediate this vulnerability, upgrade all affected Jadx core dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
<dependency>
    <groupId>io.github.skylot</groupId>
    <artifactId>jadx-core</artifactId>
    <version>1.5.0</version>
</dependency>Run the following command in your project directory to verify that all resolved dependencies use the patched release:
mvn dependency:tree -Dincludes=io.github.skylotHow to Check if You Are Affected
To determine whether your Java application is affected by GHSA-hvp5-5x4f-33fq, inspect your build dependencies using the Maven Dependency Plugin:
mvn dependency:tree -Dincludes=io.github.skylotAnalyze the terminal output to locate any version of Jadx core in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 1.5.0), your application is affected.
Note: The mvn dependency:tree -Dincludes=io.github.skylot command inspects the resolved dependency graph declared in your project's POM files; it does not perform automated security scanning or inspect runtime dynamic classpaths. Always verify runtime container classpaths and shaded JARs.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal'), where the product uses external input to construct a pathname that is intended to identify a file or directory that is located underneath a restricted parent directory, but the product does not properly neutralize special elements within the pathname that can cause the pathname to resolve to a location that is outside of the restricted directory. In Jadx core, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
GHSA-hvp5-5x4f-33fq Affected Jadx core Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
io.github.skylot:jadx-core
|
Maven |
< 1.5.0
|
1.5.0
|
References
Frequently Asked Questions
What is GHSA-hvp5-5x4f-33fq?
Which Jadx core versions are affected?
What version fixes GHSA-hvp5-5x4f-33fq?
Is jadx-core affected?
What is the CVSS score of GHSA-hvp5-5x4f-33fq?
What CWE is associated with GHSA-hvp5-5x4f-33fq?
How can I check Maven dependencies for GHSA-hvp5-5x4f-33fq?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-hvp5-5x4f-33fq",
"modified" : "2024-04-22T15:56:04Z",
"published" : "2024-04-22T15:56:04Z",
"aliases" : [ ],
"summary" : "JADX file override vulnerability",
"details" : "### Summary\nwhen jadx parses a resource file, there is an escape problem with the style file, which can overwrite other files in the directory when saving the decompile result.\n\nAlthough I don't think this vulnerability realizes path traversal in the true sense of the word , I reported it anyway\n\n### Details\n\nI see that getResAlias does something with the filename.\n\n```java\nprivate String getResAlias(int resRef, String origKeyName, @Nullable FieldNode constField) {\n```\n\nbut type style will return the original filename directly.\n\n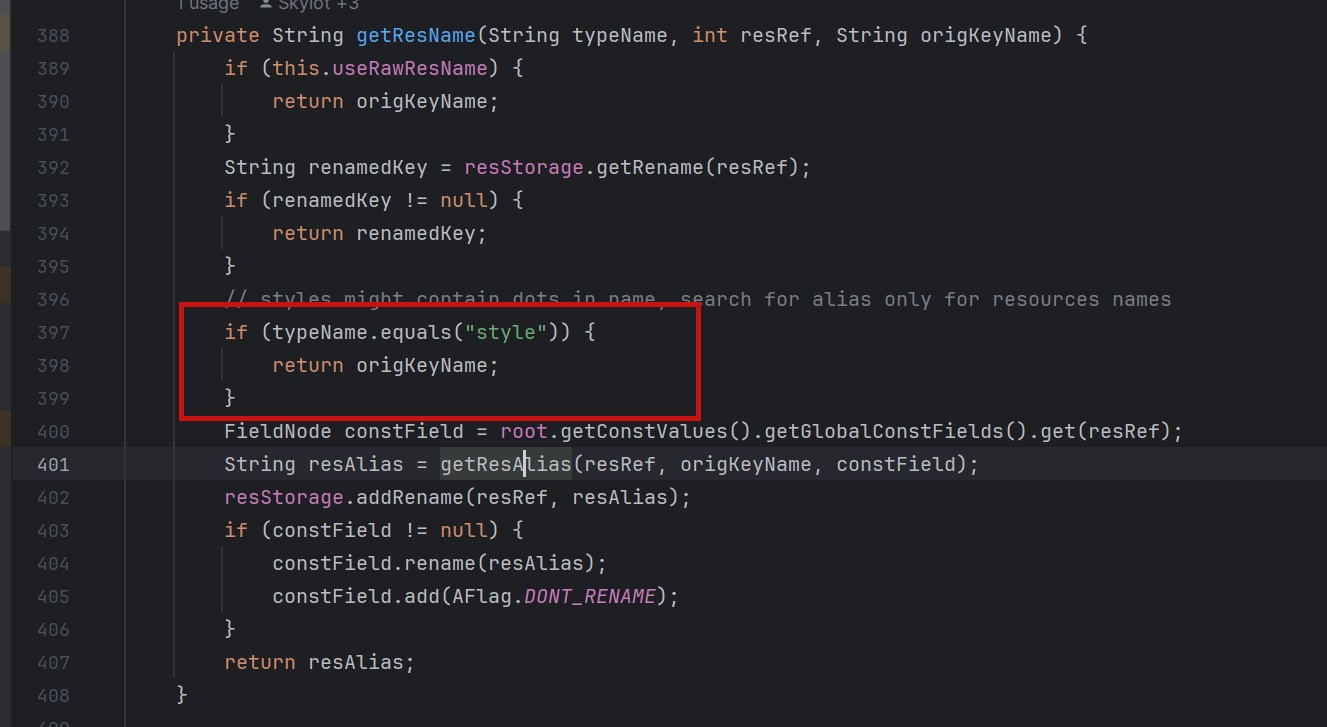\nso our goal is to take a malicious file that was originally of type raw, modify its type to style, trick jadx into\n\n#### step1\n\ncreate an android project using androidstudio and create a raw folder with the name attack_file_sayhiiiiiiiiiiiii, it doesn't matter what the content is!\n\n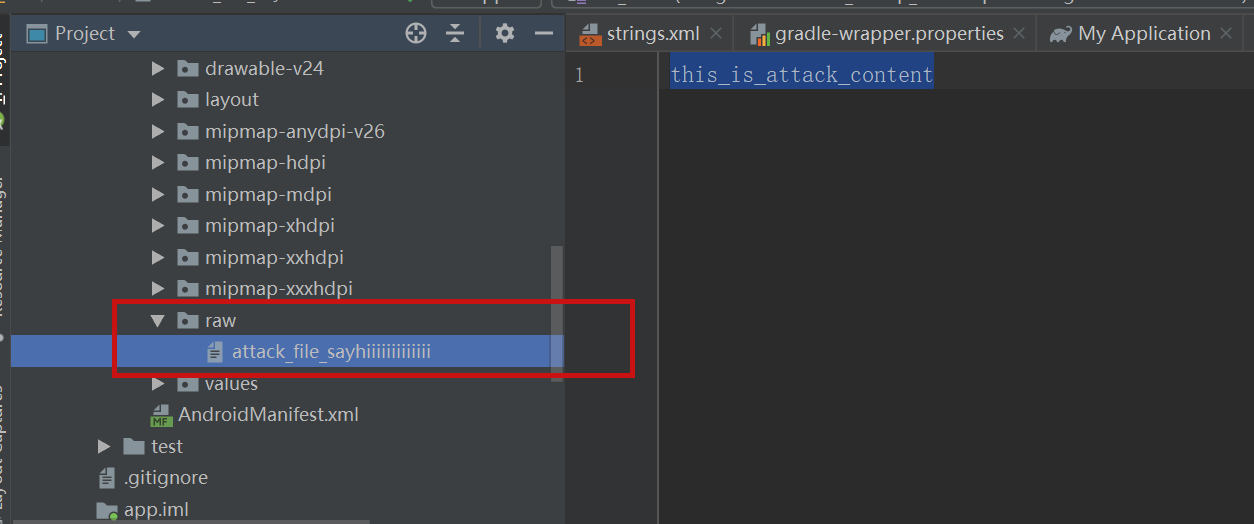\ngenerate an initial APK\n\n#### step2 \n\nextract this initial APK using ZIP software to get resources.arsc\n\n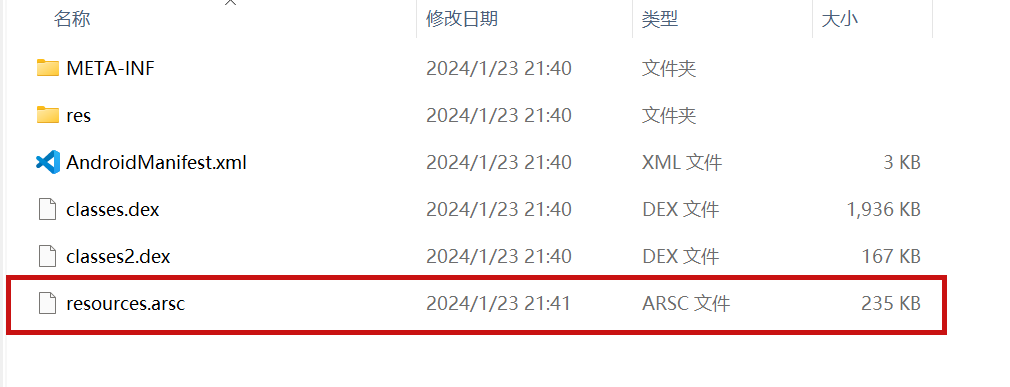\ndrop resources.arsc into 010editor\n\n#### step3\n\nsearch for the previous filename attack_file_sayhiiiiiiiiiiiii , two will appear here, we choose the second one\n\n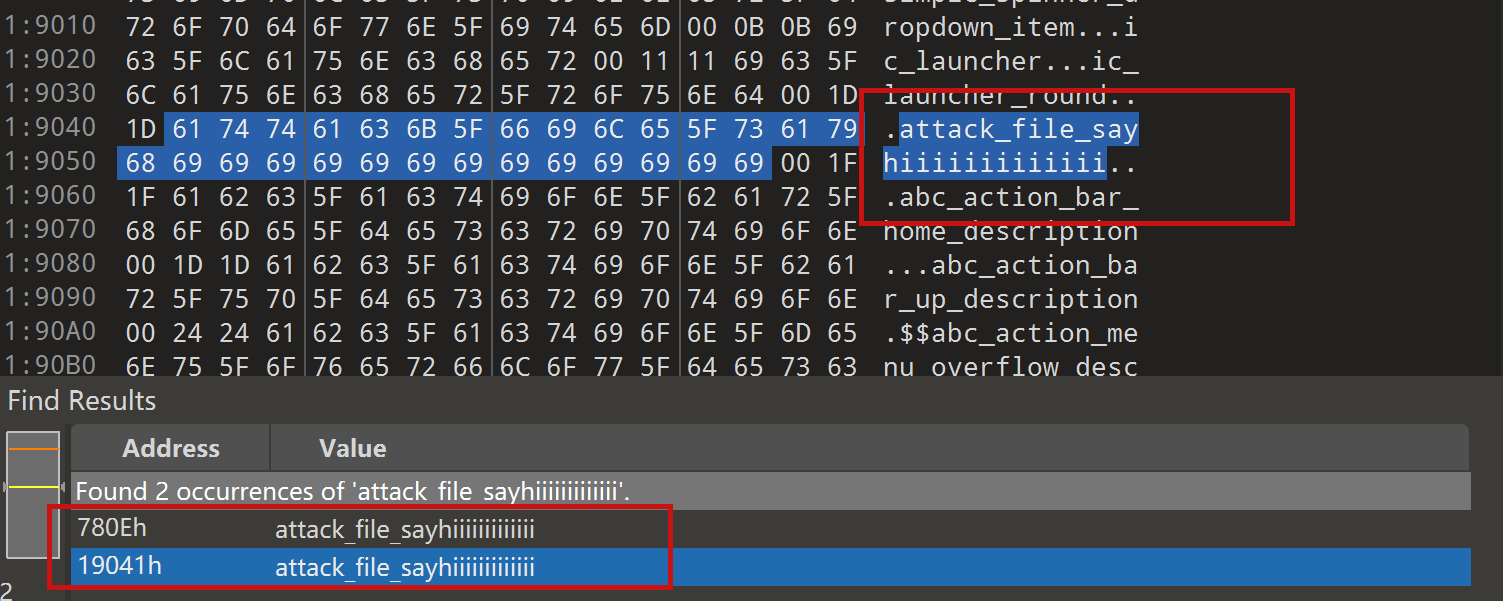\nlet's change the name of the file here. I'll change it to ../../_file_sayhiiiiiiiiiiiii\n\nnote that you can only overwrite files in the folder where the decompile was saved.\n\n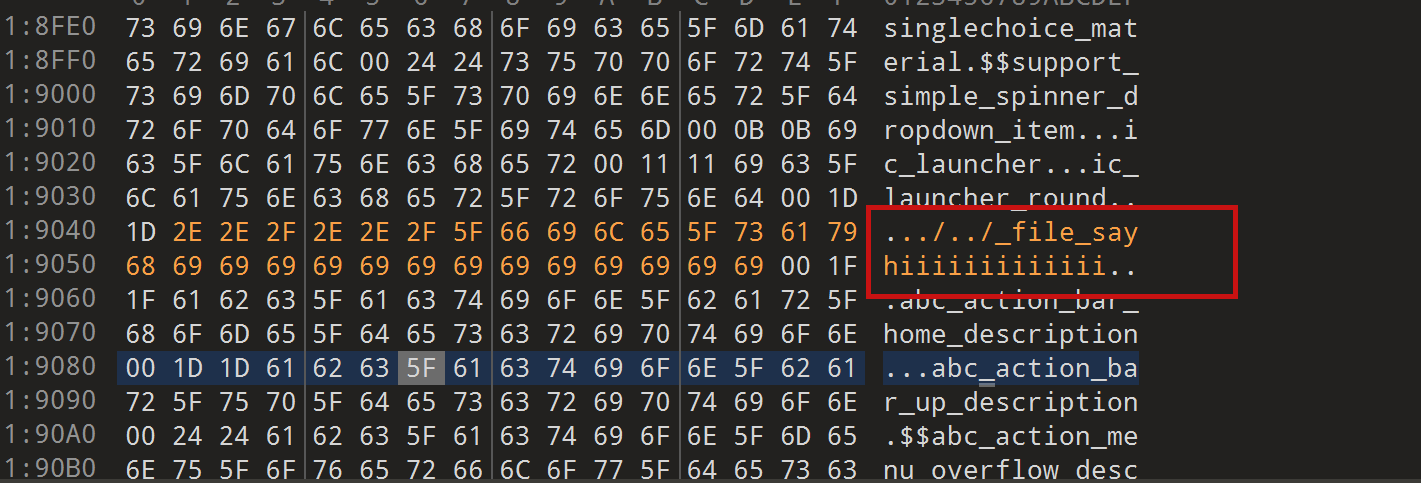\n#### step4 \nchange the type of this file to style\n\n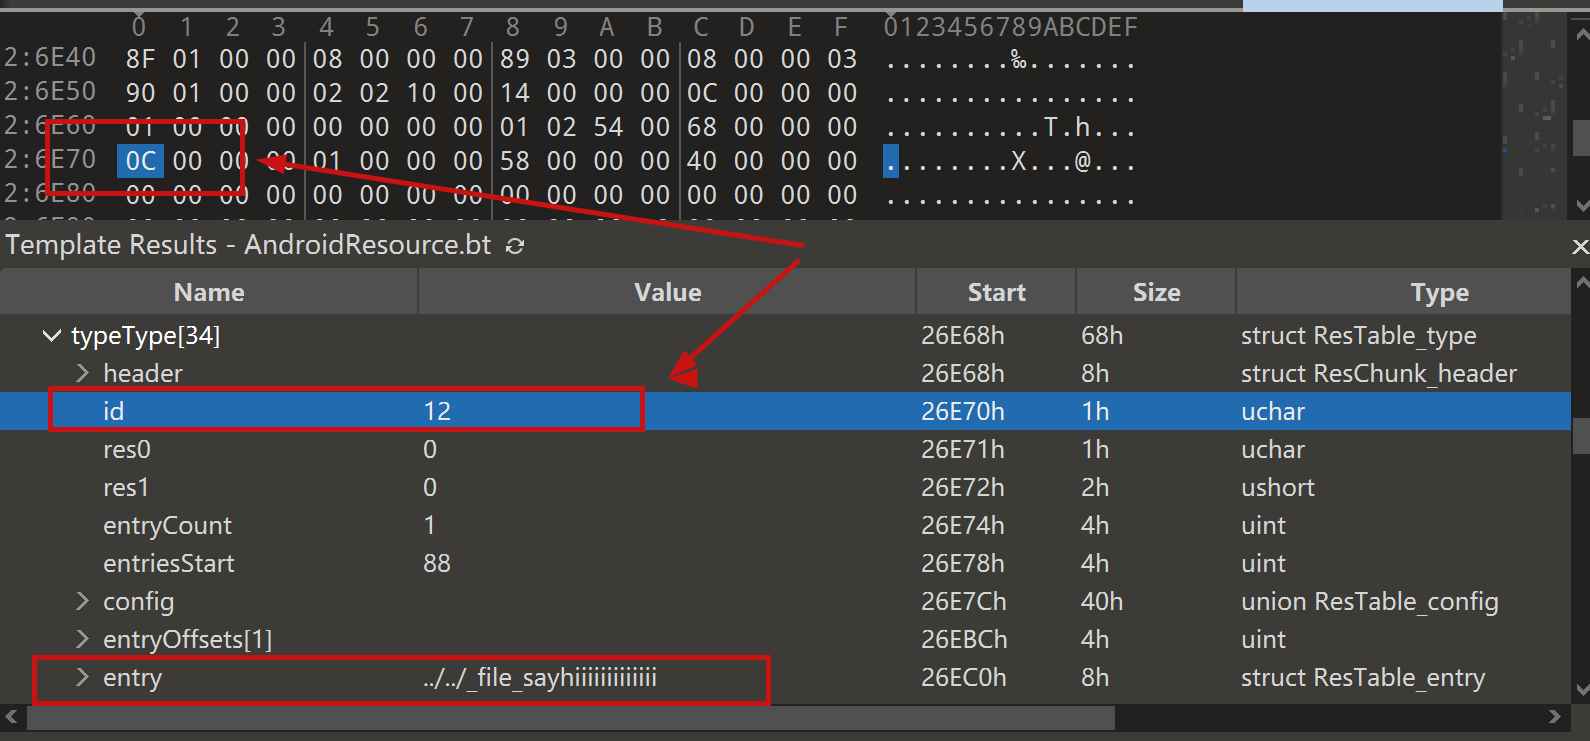\nmodified to 0E\n\n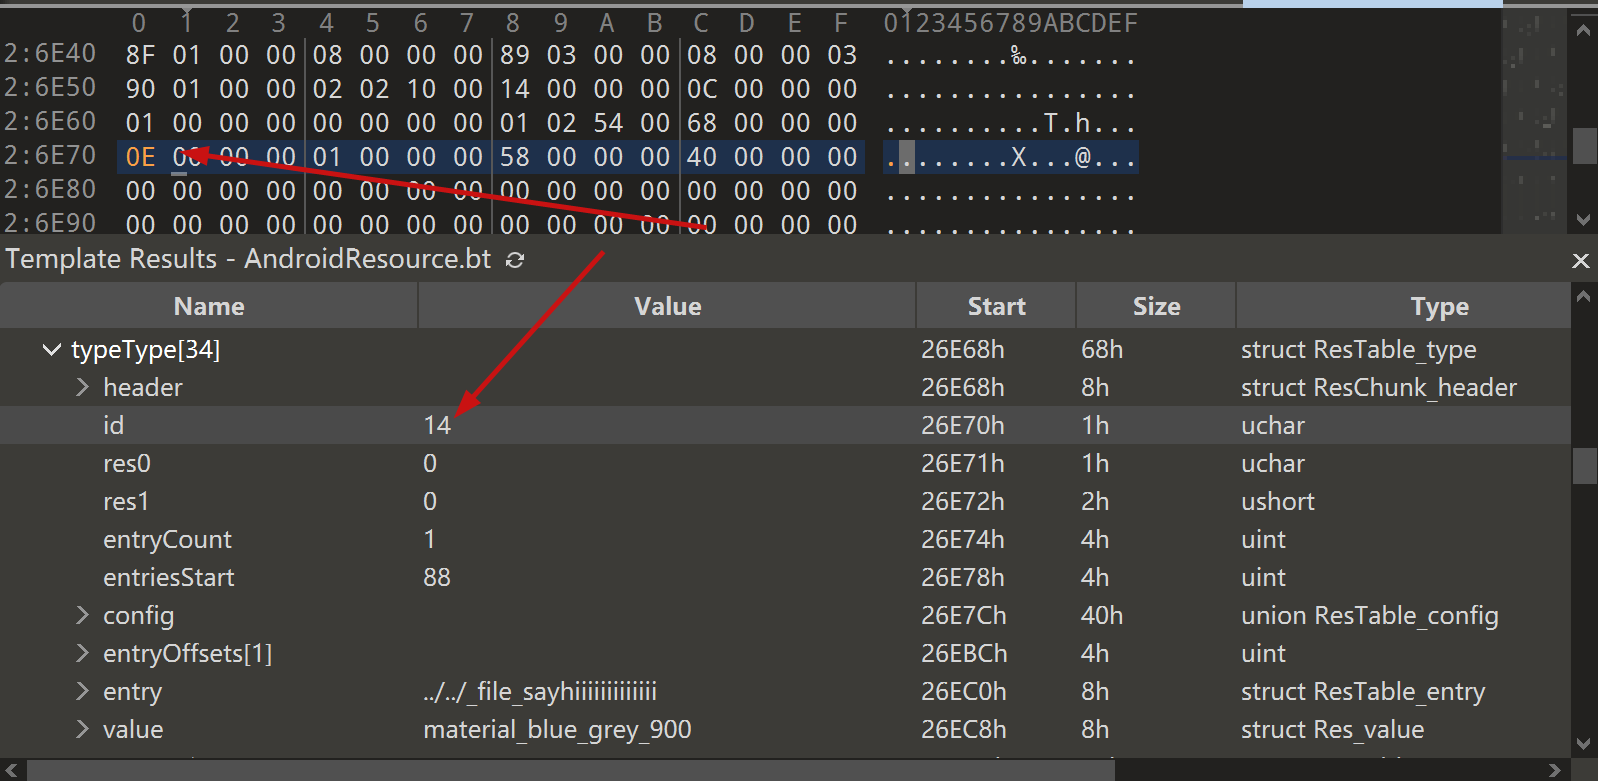\n#### step5 \n\nAfter saving, re-compress the whole folder into a zip, then change the extension to APK.\n\nopen it with JADX and you can see that it has been changed to a style type.\n\n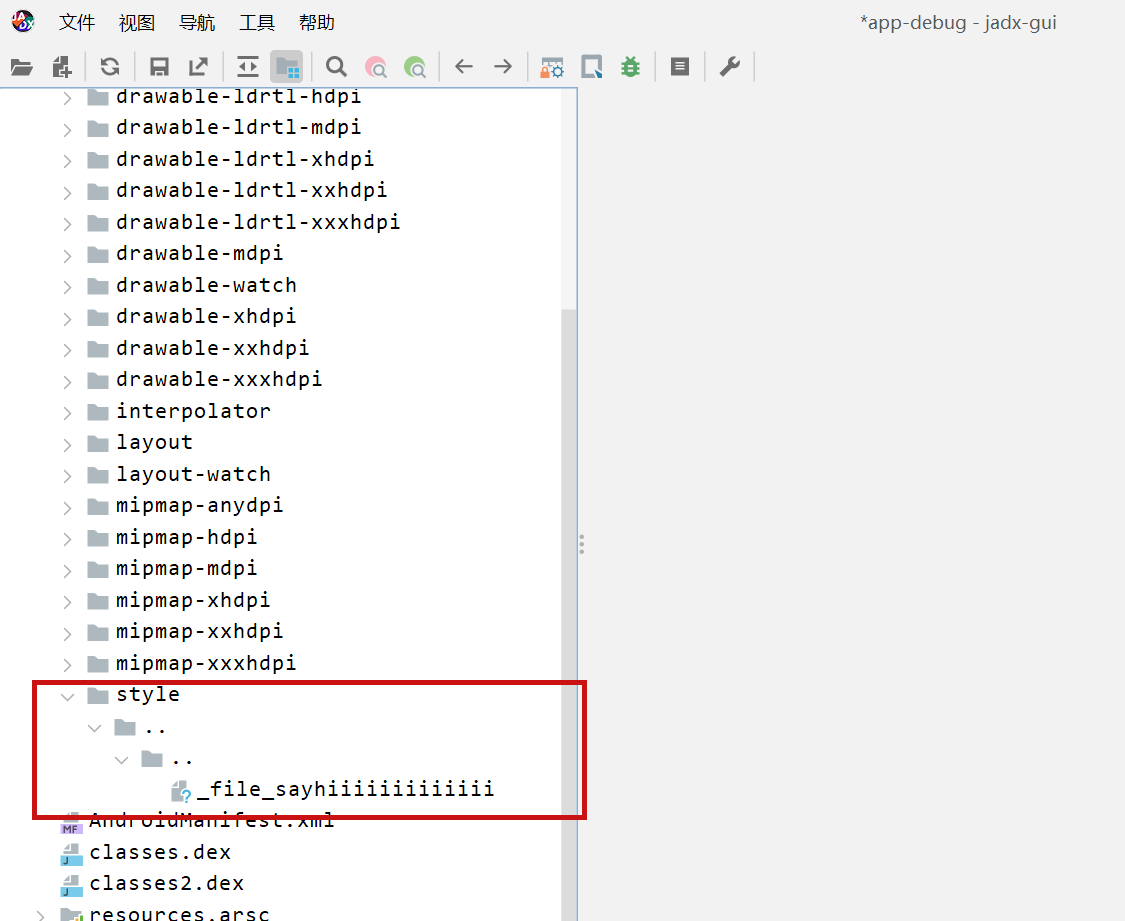\nclick save all\n\n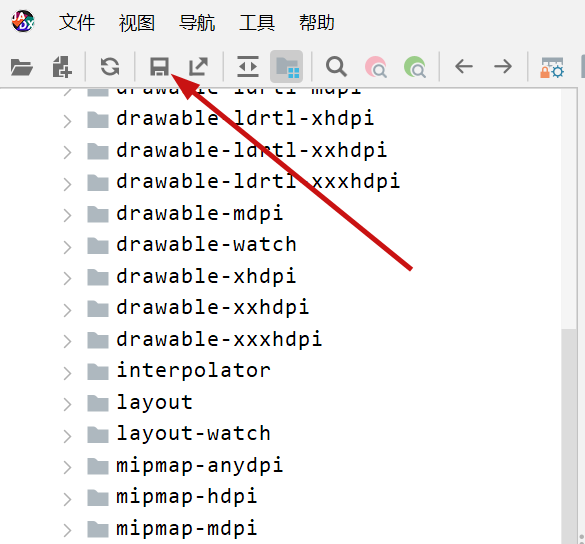\nyou can see the file escaping.\n\n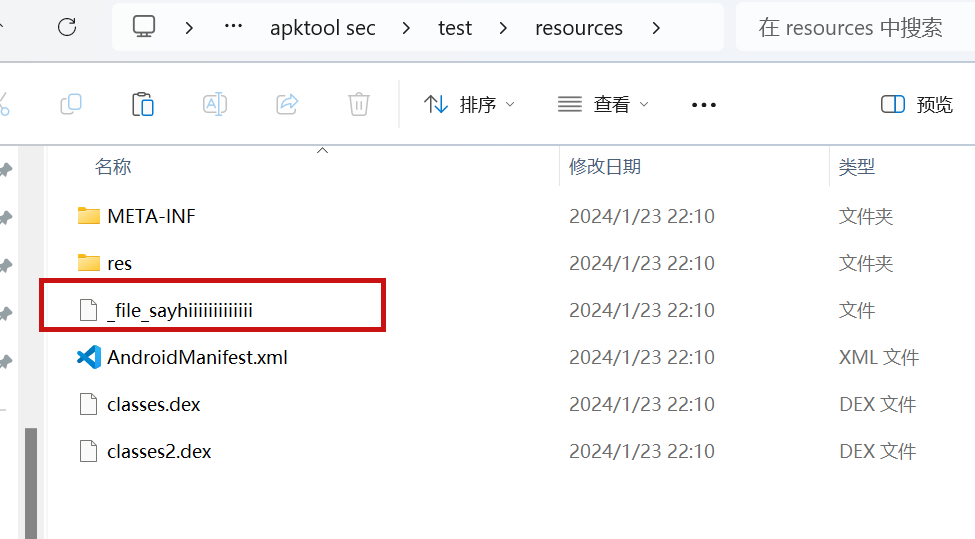\nso we can also construct a \n\n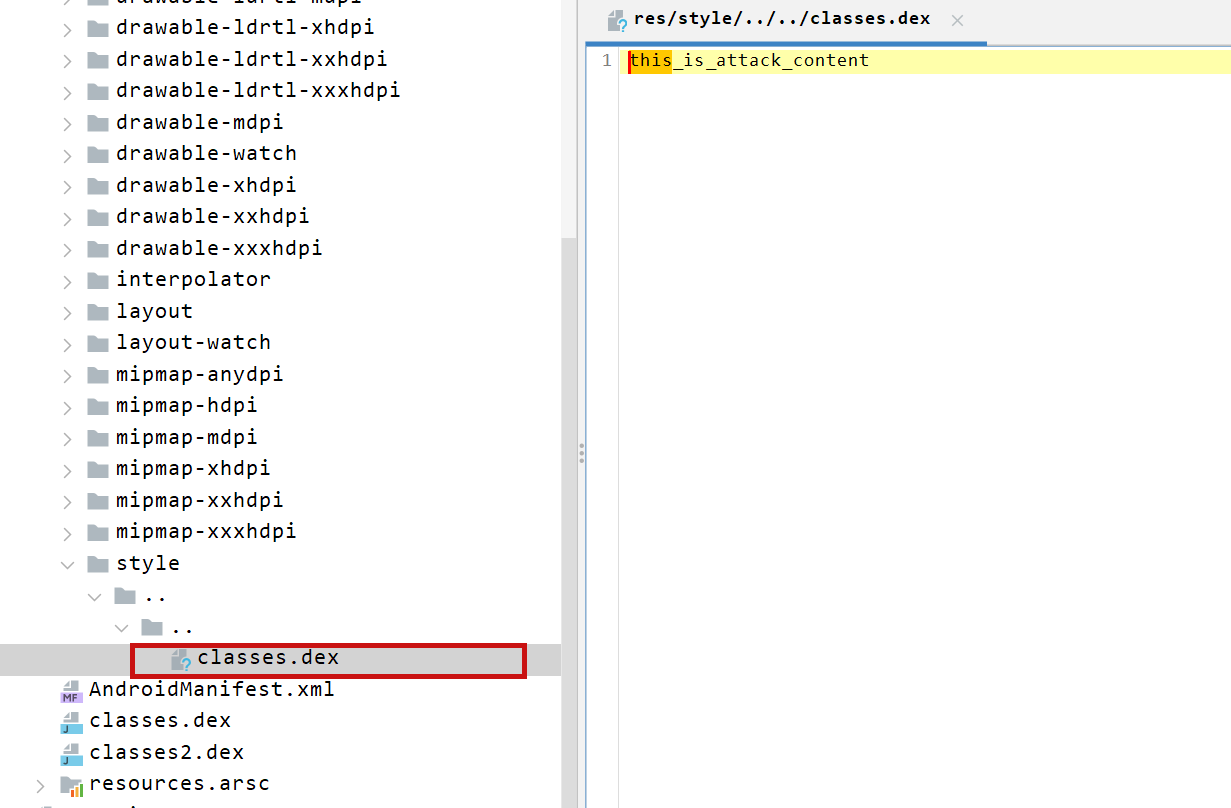\nso the classes.dex file is also replaced here\n\n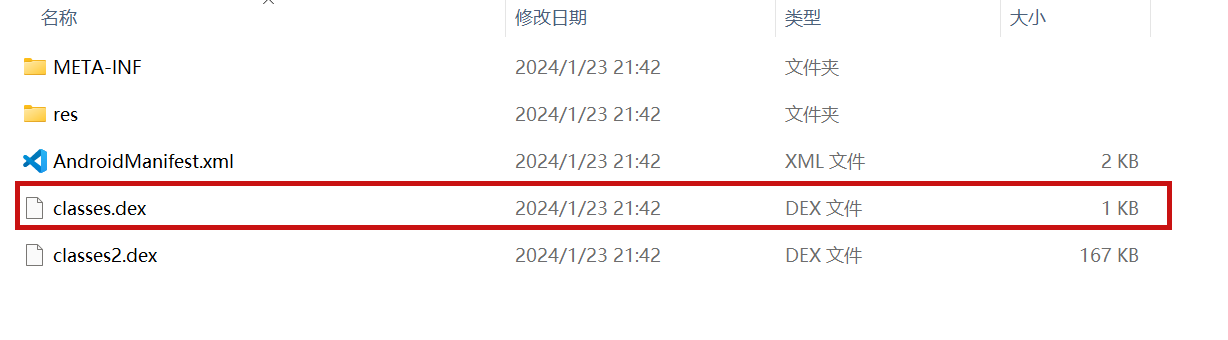\n\n### PoC\nthe details above have been written\n\n### Impact\nlatest version \n",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Maven",
"name" : "io.github.skylot:jadx-core"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "0"
}, {
"fixed" : "1.5.0"
} ]
} ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/skylot/jadx/security/advisories/GHSA-hvp5-5x4f-33fq"
}, {
"type" : "WEB",
"url" : "https://github.com/skylot/jadx/commit/d86449a8ea26381d0ce6fafaed7deb7542dfd70b"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/skylot/jadx"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-22" ],
"severity" : "LOW",
"github_reviewed" : true,
"github_reviewed_at" : "2024-04-22T15:56:04Z",
"nvd_published_at" : null
}
}