CVE-2024-32461: Librenms/librenms SQL Injection Vulnerability
HIGHCVE-2024-32461 is a HIGH (CVSS 8.8) sql injection vulnerability (CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')) affecting Librenms/librenms libraries in the Packagist ecosystem. The issue involves librenms vulnerable to sql injection time-based leads to database extraction. Remediation is available by upgrading affected packages to version 24.4.0.
CVE-2024-32461 at a Glance
Security Impact
CVSS: 8.8
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H).
How to Fix CVE-2024-32461
To remediate this vulnerability, upgrade all affected Librenms/librenms dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade librenms/librenms to 24.4.0Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for librenms/librenmsHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-32461, inspect your project dependencies for Librenms/librenms:
inspect dependencies for librenms/librenmsAnalyze the terminal output to locate any version of Librenms/librenms in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 24.4.0), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection'), where the product constructs all or part of an sql command using externally-influenced input from an upstream component, but it does not neutralize or incorrectly neutralizes special elements that could modify the intended sql command when it is sent to a downstream component. without sufficient removal or quoting of sql syntax in user-controllable inputs, the generated sql query can cause those inputs to be interpreted as sql instead of ordinary user data. In Librenms/librenms, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-32461 Affected Librenms/librenms Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
librenms/librenms
|
Packagist |
< 24.4.0
|
24.4.0
|
References
Frequently Asked Questions
What is CVE-2024-32461?
Which Librenms/librenms versions are affected?
What version fixes CVE-2024-32461?
Is librenms/librenms affected?
What is the CVSS score of CVE-2024-32461?
What CWE is associated with CVE-2024-32461?
How can I check Packagist dependencies for CVE-2024-32461?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-cwx6-cx7x-4q34",
"modified" : "2024-04-23T14:15:04Z",
"published" : "2024-04-22T18:37:21Z",
"aliases" : [ "CVE-2024-32461" ],
"summary" : "LibreNMS vulnerable to SQL injection time-based leads to database extraction",
"details" : "### Summary\nSQL injection vulnerability in POST /search/search=packages in LibreNMS 24.3.0 allows a user with global read privileges to execute SQL commands via the package parameter. \n\n### Details\nThere is a lack of hygiene of data coming from the user in line 83 of the file librenms/includes/html/pages/search/packages.inc.php\n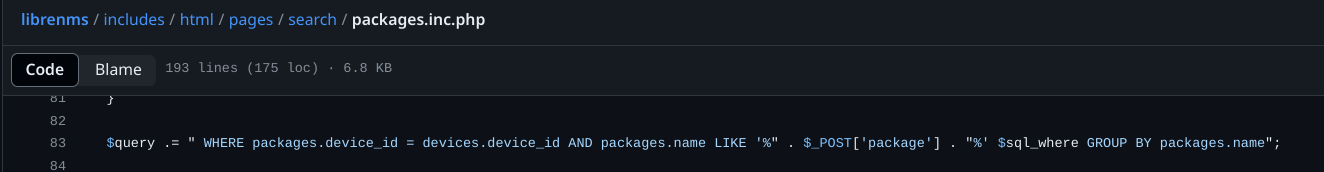\n\n### PoC\nhttps://doc.clickup.com/9013166444/p/h/8ckm0bc-53/16811991bb5fff6\n\n### Impact\nWith this vulnerability, we can exploit a SQL injection time based vulnerability to extract all data from the database, such as administrator credentials\n",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Packagist",
"name" : "librenms/librenms"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "0"
}, {
"fixed" : "24.4.0"
} ]
} ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/librenms/librenms/security/advisories/GHSA-cwx6-cx7x-4q34"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2024-32461"
}, {
"type" : "WEB",
"url" : "https://github.com/librenms/librenms/commit/d29201fce134347f891102699fbde7070debee33"
}, {
"type" : "WEB",
"url" : "https://doc.clickup.com/9013166444/p/h/8ckm0bc-53/16811991bb5fff6"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/librenms/librenms"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-89" ],
"severity" : "HIGH",
"github_reviewed" : true,
"github_reviewed_at" : "2024-04-22T18:37:21Z",
"nvd_published_at" : "2024-04-22T22:15:07Z"
}
}