CVE-2024-28106: Phpmyfaq/phpmyfaq Cross-Site Scripting Vulnerability
MODERATECVE-2024-28106 is a MODERATE (CVSS 4.3) cross-site scripting vulnerability (CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')) affecting Phpmyfaq/phpmyfaq libraries in the Packagist ecosystem. The issue involves phpmyfaq stored cross-site scripting at faq news content. Remediation is available by upgrading affected packages to version 3.2.6.
CVE-2024-28106 at a Glance
Security Impact
CVSS: 4.3
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L).
How to Fix CVE-2024-28106
To remediate this vulnerability, upgrade all affected Phpmyfaq/phpmyfaq dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade phpmyfaq/phpmyfaq to 3.2.6Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for phpmyfaq/phpmyfaqHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-28106, inspect your project dependencies for Phpmyfaq/phpmyfaq:
inspect dependencies for phpmyfaq/phpmyfaqAnalyze the terminal output to locate any version of Phpmyfaq/phpmyfaq in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 3.2.6), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting'), where the product does not neutralize or incorrectly neutralizes user-controllable input before it is placed in output that is used as a web page that is served to other users. In Phpmyfaq/phpmyfaq, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-28106 Affected Phpmyfaq/phpmyfaq Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
phpmyfaq/phpmyfaq
|
Packagist |
≥ 3.2.5
< 3.2.6
All 1 versions
3.2.5
|
3.2.6
|
References
Frequently Asked Questions
What is CVE-2024-28106?
Which Phpmyfaq/phpmyfaq versions are affected?
What version fixes CVE-2024-28106?
Is phpmyfaq/phpmyfaq affected?
What is the CVSS score of CVE-2024-28106?
What CWE is associated with CVE-2024-28106?
How can I check Packagist dependencies for CVE-2024-28106?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-6p68-36m6-392r",
"modified" : "2024-03-25T22:28:12Z",
"published" : "2024-03-25T19:45:52Z",
"aliases" : [ "CVE-2024-28106" ],
"summary" : "phpMyFAQ Stored Cross-site Scripting at FAQ News Content",
"details" : "### Summary\nBy manipulating the news parameter in a POST request, an attacker can inject malicious JavaScript code. Upon browsing to the compromised news page, the XSS payload triggers.\n\n### PoC\n1. Edit a FAQ news, intercept the request and modify the `news` parameter in the POST body with the following payload: `%3cscript%3ealert('xssContent')%3c%2fscript%3e`\n2. Browse to the particular news page and the XSS should pop up.\n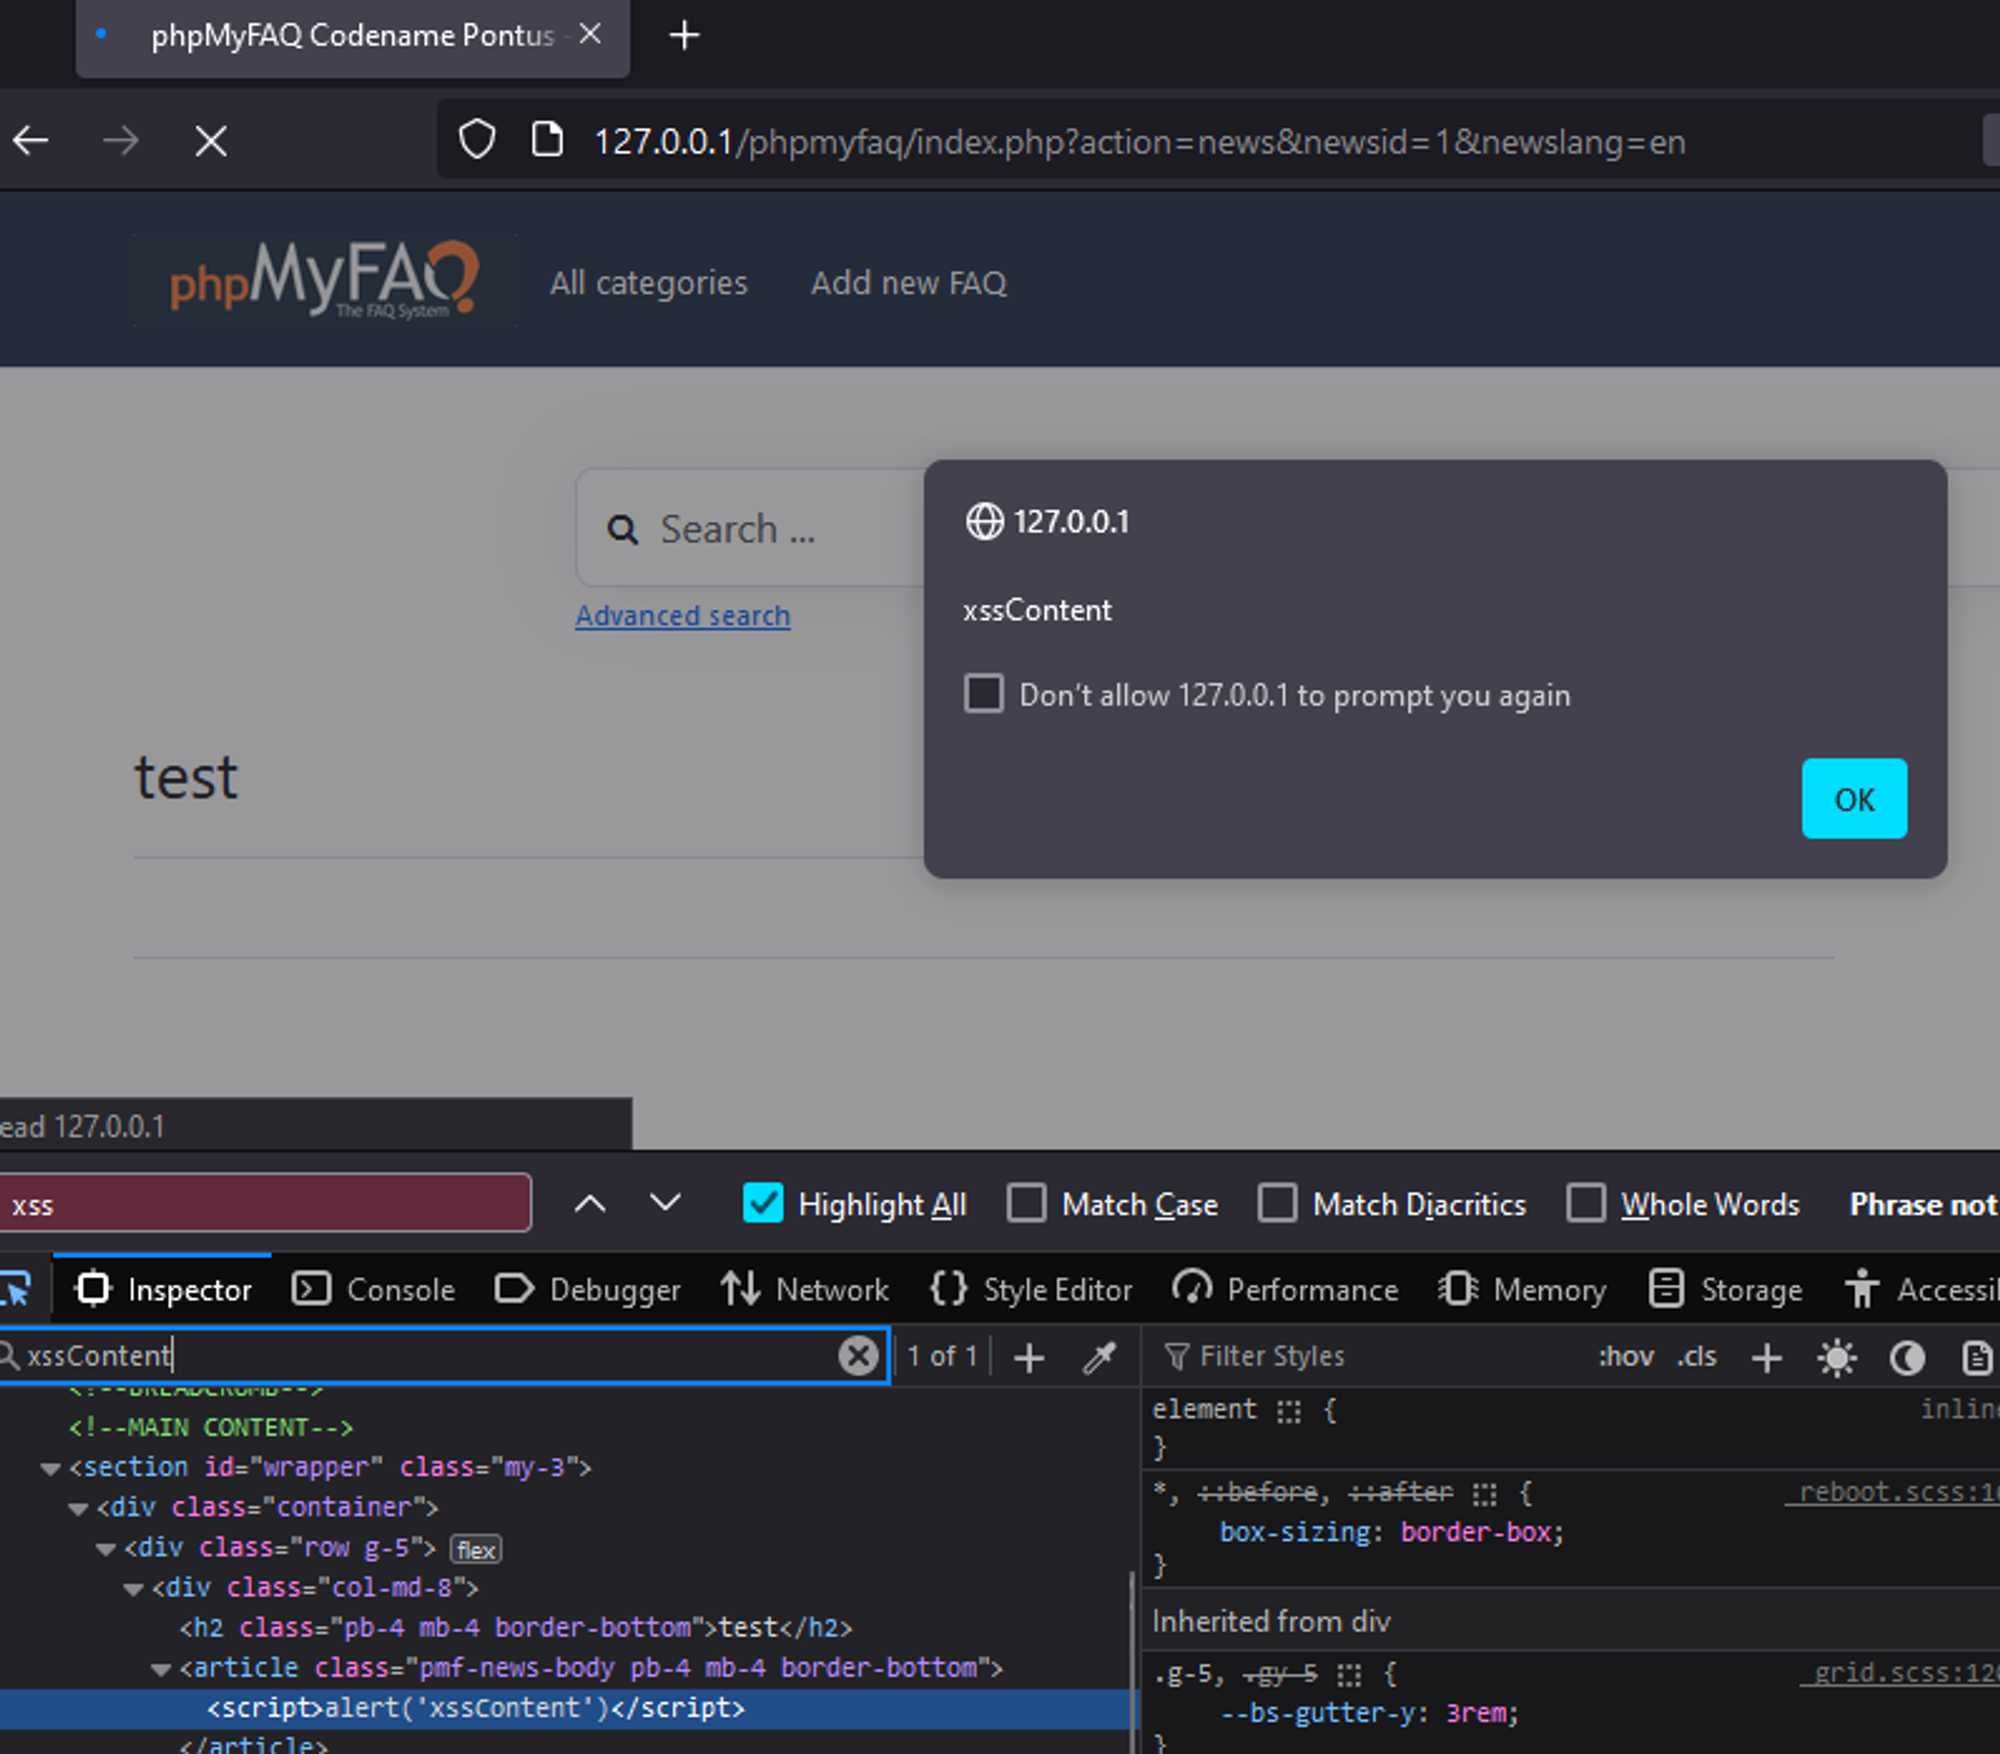\n\n### Impact\nThis allows an attacker to execute arbitrary client side JavaScript within the context of another user's phpMyFAQ session",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Packagist",
"name" : "phpmyfaq/phpmyfaq"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "3.2.5"
}, {
"fixed" : "3.2.6"
} ]
} ],
"versions" : [ "3.2.5" ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-6p68-36m6-392r"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2024-28106"
}, {
"type" : "WEB",
"url" : "https://github.com/thorsten/phpMyFAQ/commit/c94b3deadd87789389e1fad162bc3dd595c0e15a"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/thorsten/phpMyFAQ"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-79" ],
"severity" : "MODERATE",
"github_reviewed" : true,
"github_reviewed_at" : "2024-03-25T19:45:52Z",
"nvd_published_at" : "2024-03-25T19:15:58Z"
}
}