CVE-2024-52291: Craftcms/cms Local File System Validation Bypass Vulnerability
HIGHCVE-2024-52291 is a HIGH (CVSS 8.4) local file system validation bypass vulnerability (CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')) affecting Craftcms/cms libraries in the Packagist ecosystem. The issue involves local file system validation bypass leading to file overwrite, sensitive file access, and potential code execution. Remediation is available by upgrading affected packages to version 5.4.6, 4.12.5.
CVE-2024-52291 at a Glance
Security Impact
CVSS: 8.4
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:H).
How to Fix CVE-2024-52291
To remediate this vulnerability, upgrade all affected Craftcms/cms dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade craftcms/cms to 5.4.6Upgrade craftcms/cms to 4.12.5Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for craftcms/cmsHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-52291, inspect your project dependencies for Craftcms/cms:
inspect dependencies for craftcms/cmsAnalyze the terminal output to locate any version of Craftcms/cms in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 5.4.6), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-22: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal'), where the product uses external input to construct a pathname that is intended to identify a file or directory that is located underneath a restricted parent directory, but the product does not properly neutralize special elements within the pathname that can cause the pathname to resolve to a location that is outside of the restricted directory. In Craftcms/cms, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-52291 Affected Craftcms/cms Versions
2 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
craftcms/cms
|
Packagist |
≥ 5.0.0-RC1
< 5.4.6
|
5.4.6
|
|
craftcms/cms
|
Packagist |
≥ 4.0.0-RC1
< 4.12.5
|
4.12.5
|
References
Frequently Asked Questions
What is CVE-2024-52291?
Which Craftcms/cms versions are affected?
What version fixes CVE-2024-52291?
Is craftcms/cms affected?
What is the CVSS score of CVE-2024-52291?
What CWE is associated with CVE-2024-52291?
How can I check Packagist dependencies for CVE-2024-52291?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-jrh5-vhr9-qh7q",
"modified" : "2024-11-13T18:58:32Z",
"published" : "2024-11-13T14:12:36Z",
"aliases" : [ "CVE-2024-52291" ],
"summary" : "Local File System Validation Bypass Leading to File Overwrite, Sensitive File Access, and Potential Code Execution",
"details" : "### Summary\nA vulnerability in CraftCMS allows an attacker to bypass local file system validation by utilizing a double `file://` scheme (e.g., `file://file:////`). This enables the attacker to specify sensitive folders as the file system, leading to potential file overwriting through malicious uploads, unauthorized access to sensitive files, and, under certain conditions, remote code execution (RCE) via Server-Side Template Injection (SSTI) payloads.\n\nNote that this will only work if you have an authenticated administrator account with [allowAdminChanges enabled](https://craftcms.com/docs/5.x/reference/config/general.html#allowadminchanges).\n\nhttps://craftcms.com/knowledge-base/securing-craft#set-allowAdminChanges-to-false-in-production\n\n### Details\nThe issue lies in line 57 of `cms/src/helpers/FileHelper.php`, it only removes `file://` on the most left. It is trivial to bypass this sanitization by adding 2 `file://`, e.g. `file://file:////`.\n```php\n public static function normalizePath($path, $ds = DIRECTORY_SEPARATOR): string\n {\n // Remove any file protocol wrappers\n $path = StringHelper::removeLeft($path, 'file://');\n\n // Is this a UNC network share path?\n $isUnc = (str_starts_with($path, '//') || str_starts_with($path, '\\\\\\\\'));\n\n // Normalize the path\n $path = parent::normalizePath($path, $ds);\n\n // If it is UNC, add those slashes back in front\n if ($isUnc) {\n $path = $ds . $ds . ltrim($path, $ds);\n }\n\n return $path;\n }\n```\n\n### PoC\n1. Sign in with an admin account and navigate to `Settings → Assets`, then create a new volume.\n2. n the Asset Filesystem section, create a new file system and set the Base Path to `file://file:////vendor`.\nWithout the prefix, the selection fails.\n 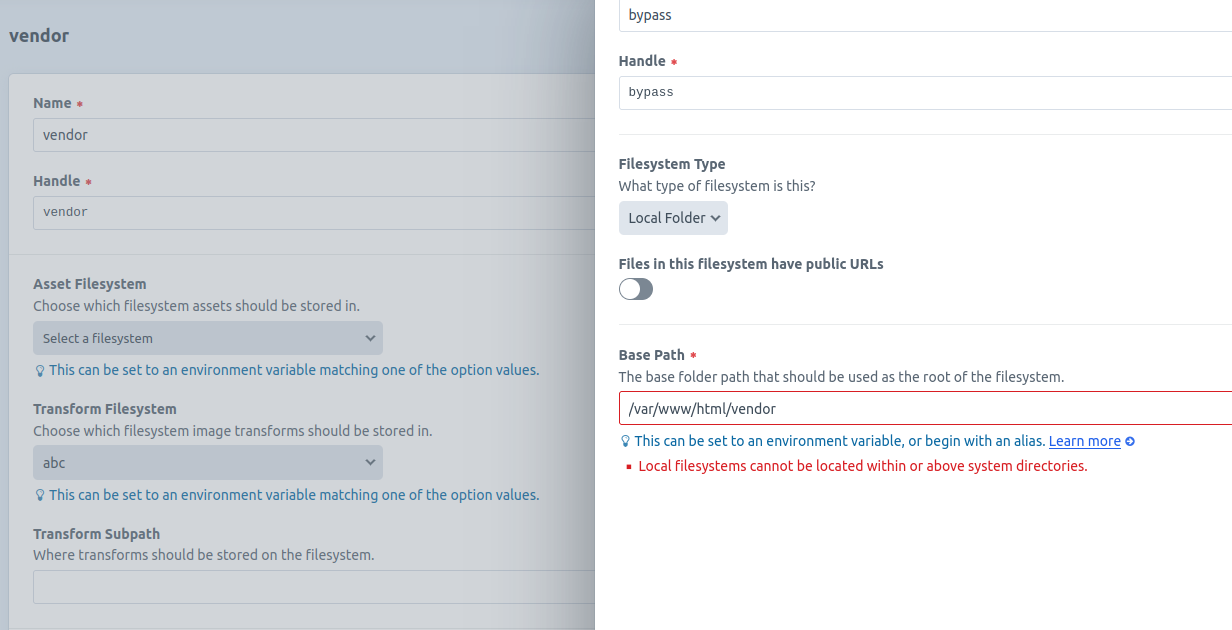\nWith the double `file://` prefix, the selection succeeds.\n 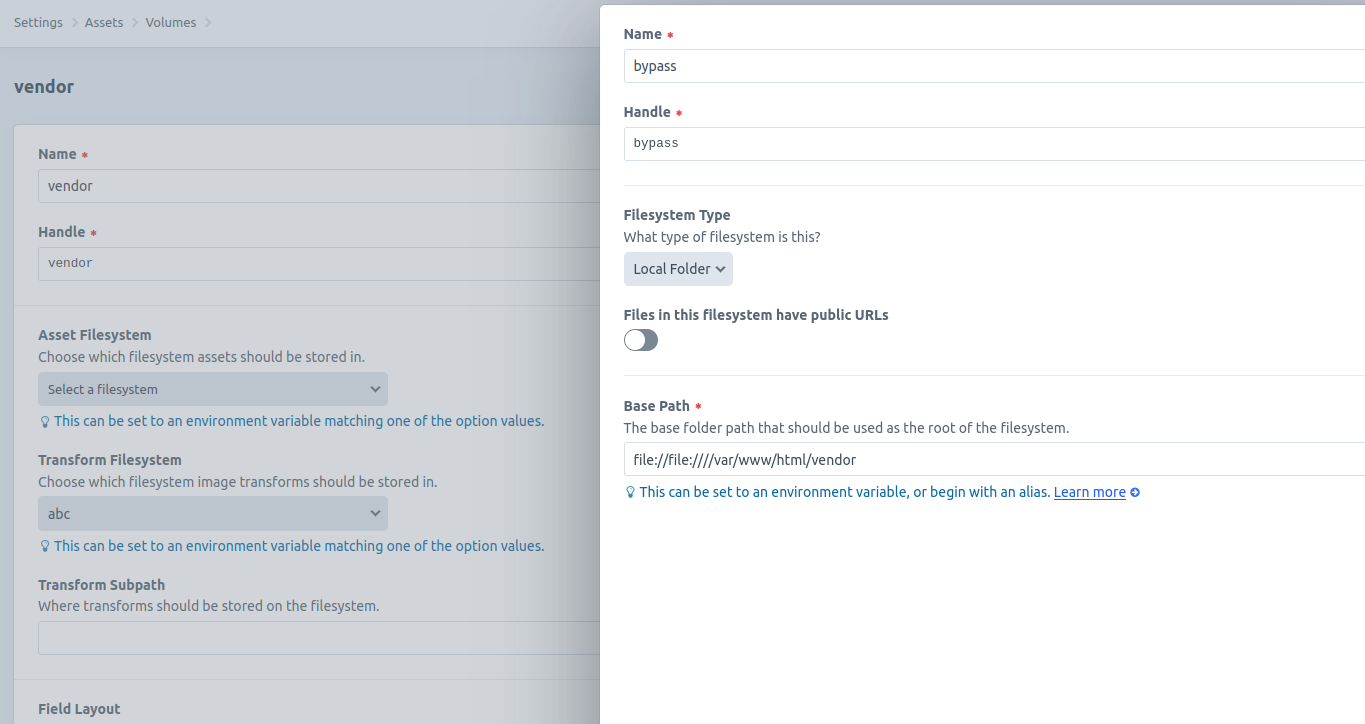\n3. Access Assets from the left navigation bar, then upload a file into this volume.\n 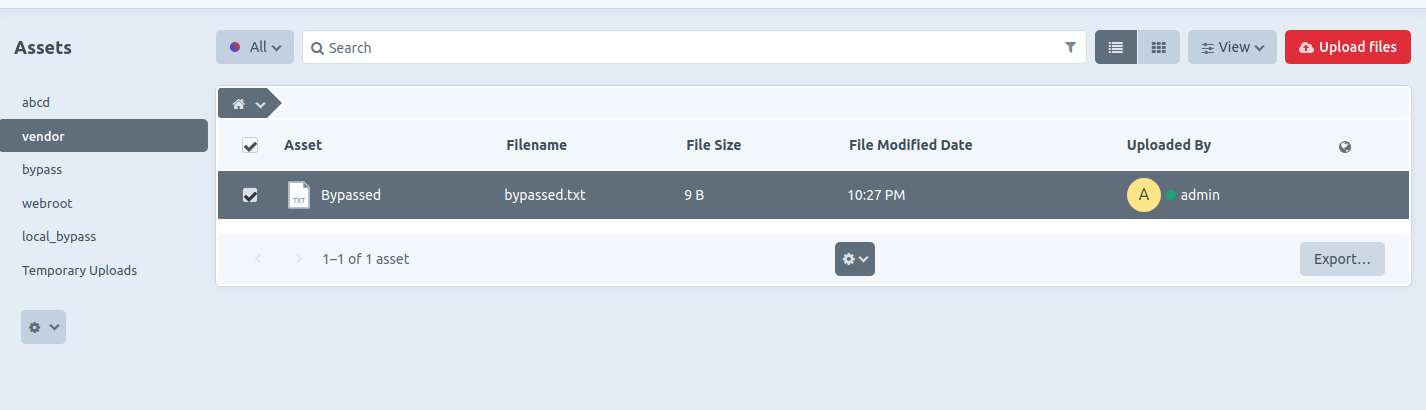\n4. The file is successfully uploaded and stored in the sensitive folder specified (e.g., `/vendor`).\n 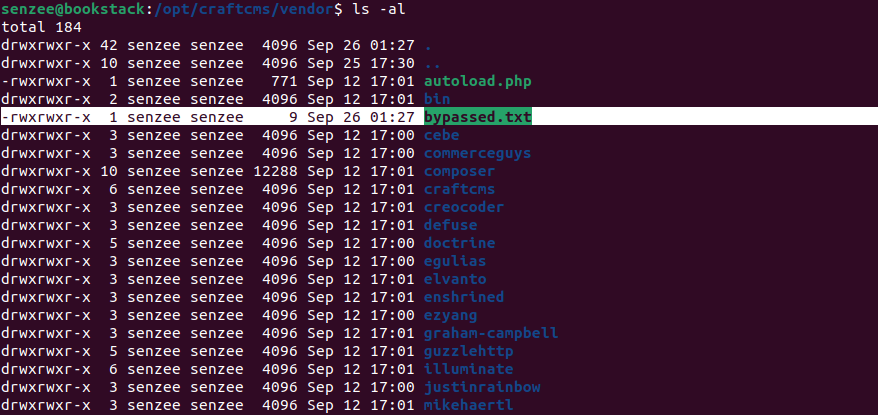\n5. SSTI payloads can be uploaded to `/templates` folder, though full code execution was not achieved during testing, some payloads were still successful, leading to sensitive information disclosure, among other potential impacts.\n 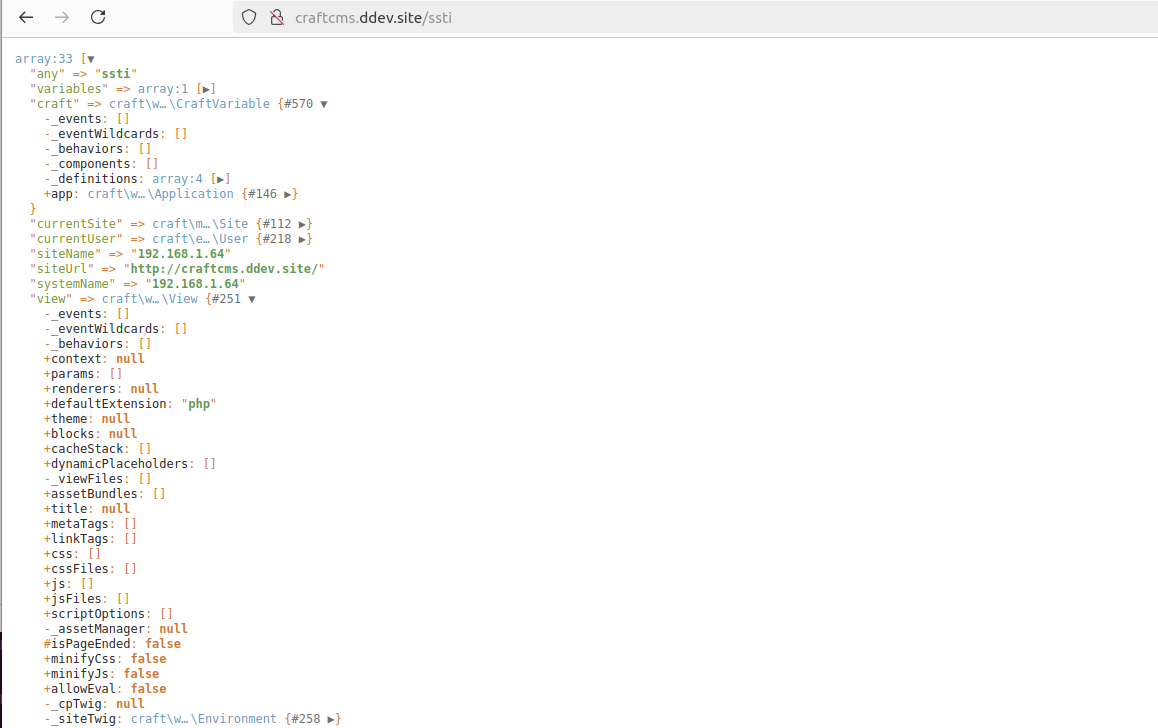\n\n### Impact\nAttackers who compromise an admin account(The admin user is not equal to the server owner) can exploit this flaw to assign sensitive folders as the base path of the filesystem. For instance, if the path `/templates` is specified (e.g., `file://file:////var/www/html/templates`), the attacker could upload SSTI payloads. While CraftCMS includes strict SSTI input sanitization, RCE may still be possible if the attacker can craft a valid payload, as seen in similar vulnerabilities (e.g., [GHSA-44wr-rmwq-3phw](https://github.com/advisories/GHSA-44wr-rmwq-3phw)).\n\nAdditionally, attackers can upload tampered files to overwrite critical web application files. By enabling public URLs for files in the specified filesystem, they can also retrieve sensitive files (e.g., configuration files from the local file system).\n\nAlthough the vulnerability is exploitable only in the authenticated users, configuration with `ALLOW_ADMIN_CHANGES=true`, there is still a potential security threat.\n\n",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:C/C:H/I:H/A:H"
}, {
"type" : "CVSS_V4",
"score" : "CVSS:4.0/AV:N/AC:L/AT:P/PR:H/UI:A/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H/E:P"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Packagist",
"name" : "craftcms/cms"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "5.0.0-RC1"
}, {
"fixed" : "5.4.6"
} ]
} ],
"database_specific" : {
"last_known_affected_version_range" : "<= 5.4.5.1"
}
}, {
"package" : {
"ecosystem" : "Packagist",
"name" : "craftcms/cms"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "4.0.0-RC1"
}, {
"fixed" : "4.12.5"
} ]
} ],
"database_specific" : {
"last_known_affected_version_range" : "<= 4.12.4.1"
}
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/craftcms/cms/security/advisories/GHSA-jrh5-vhr9-qh7q"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2024-52291"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/craftcms/cms"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-22" ],
"severity" : "HIGH",
"github_reviewed" : true,
"github_reviewed_at" : "2024-11-13T14:12:36Z",
"nvd_published_at" : "2024-11-13T17:15:12Z"
}
}