CVE-2024-29179: Phpmyfaq/phpmyfaq Cross-Site Scripting Vulnerability
MODERATECVE-2024-29179 is a MODERATE (CVSS 4.3) cross-site scripting vulnerability (CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')) affecting Phpmyfaq/phpmyfaq libraries in the Packagist ecosystem. The issue involves phpmyfaq stored cross-site scripting at file attachments. Remediation is available by upgrading affected packages to version 3.2.6.
CVE-2024-29179 at a Glance
Security Impact
CVSS: 4.3
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L).
How to Fix CVE-2024-29179
To remediate this vulnerability, upgrade all affected Phpmyfaq/phpmyfaq dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade phpmyfaq/phpmyfaq to 3.2.6Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for phpmyfaq/phpmyfaqHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-29179, inspect your project dependencies for Phpmyfaq/phpmyfaq:
inspect dependencies for phpmyfaq/phpmyfaqAnalyze the terminal output to locate any version of Phpmyfaq/phpmyfaq in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 3.2.6), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting'), where the product does not neutralize or incorrectly neutralizes user-controllable input before it is placed in output that is used as a web page that is served to other users. In Phpmyfaq/phpmyfaq, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-29179 Affected Phpmyfaq/phpmyfaq Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
phpmyfaq/phpmyfaq
|
Packagist |
≥ 3.2.5
< 3.2.6
All 1 versions
3.2.5
|
3.2.6
|
References
Frequently Asked Questions
What is CVE-2024-29179?
Which Phpmyfaq/phpmyfaq versions are affected?
What version fixes CVE-2024-29179?
Is phpmyfaq/phpmyfaq affected?
What is the CVSS score of CVE-2024-29179?
What CWE is associated with CVE-2024-29179?
How can I check Packagist dependencies for CVE-2024-29179?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-hm8r-95g3-5hj9",
"modified" : "2024-03-25T22:31:44Z",
"published" : "2024-03-25T19:45:12Z",
"aliases" : [ "CVE-2024-29179" ],
"summary" : "phpMyFAQ Stored Cross-site Scripting at File Attachments",
"details" : "### Summary\nAn attacker with admin privileges can upload an attachment containing JS code without extension and the application will render it as HTML which allows for XSS attacks.\n\n### Details\nWhen attachments are uploaded without an extension, the application renders it as HTML by default. Therefore allowing attackers to upload .html files containing javascript code to perform XSS attacks. The direct file path to the uploaded attachment is also easily obtainable as it is made up of substrings of the file's MD5 hashes.\n\n### PoC\n1. Admin users can upload attachments containing XSS payloads in files without extensions to bypass the .html extension check.\n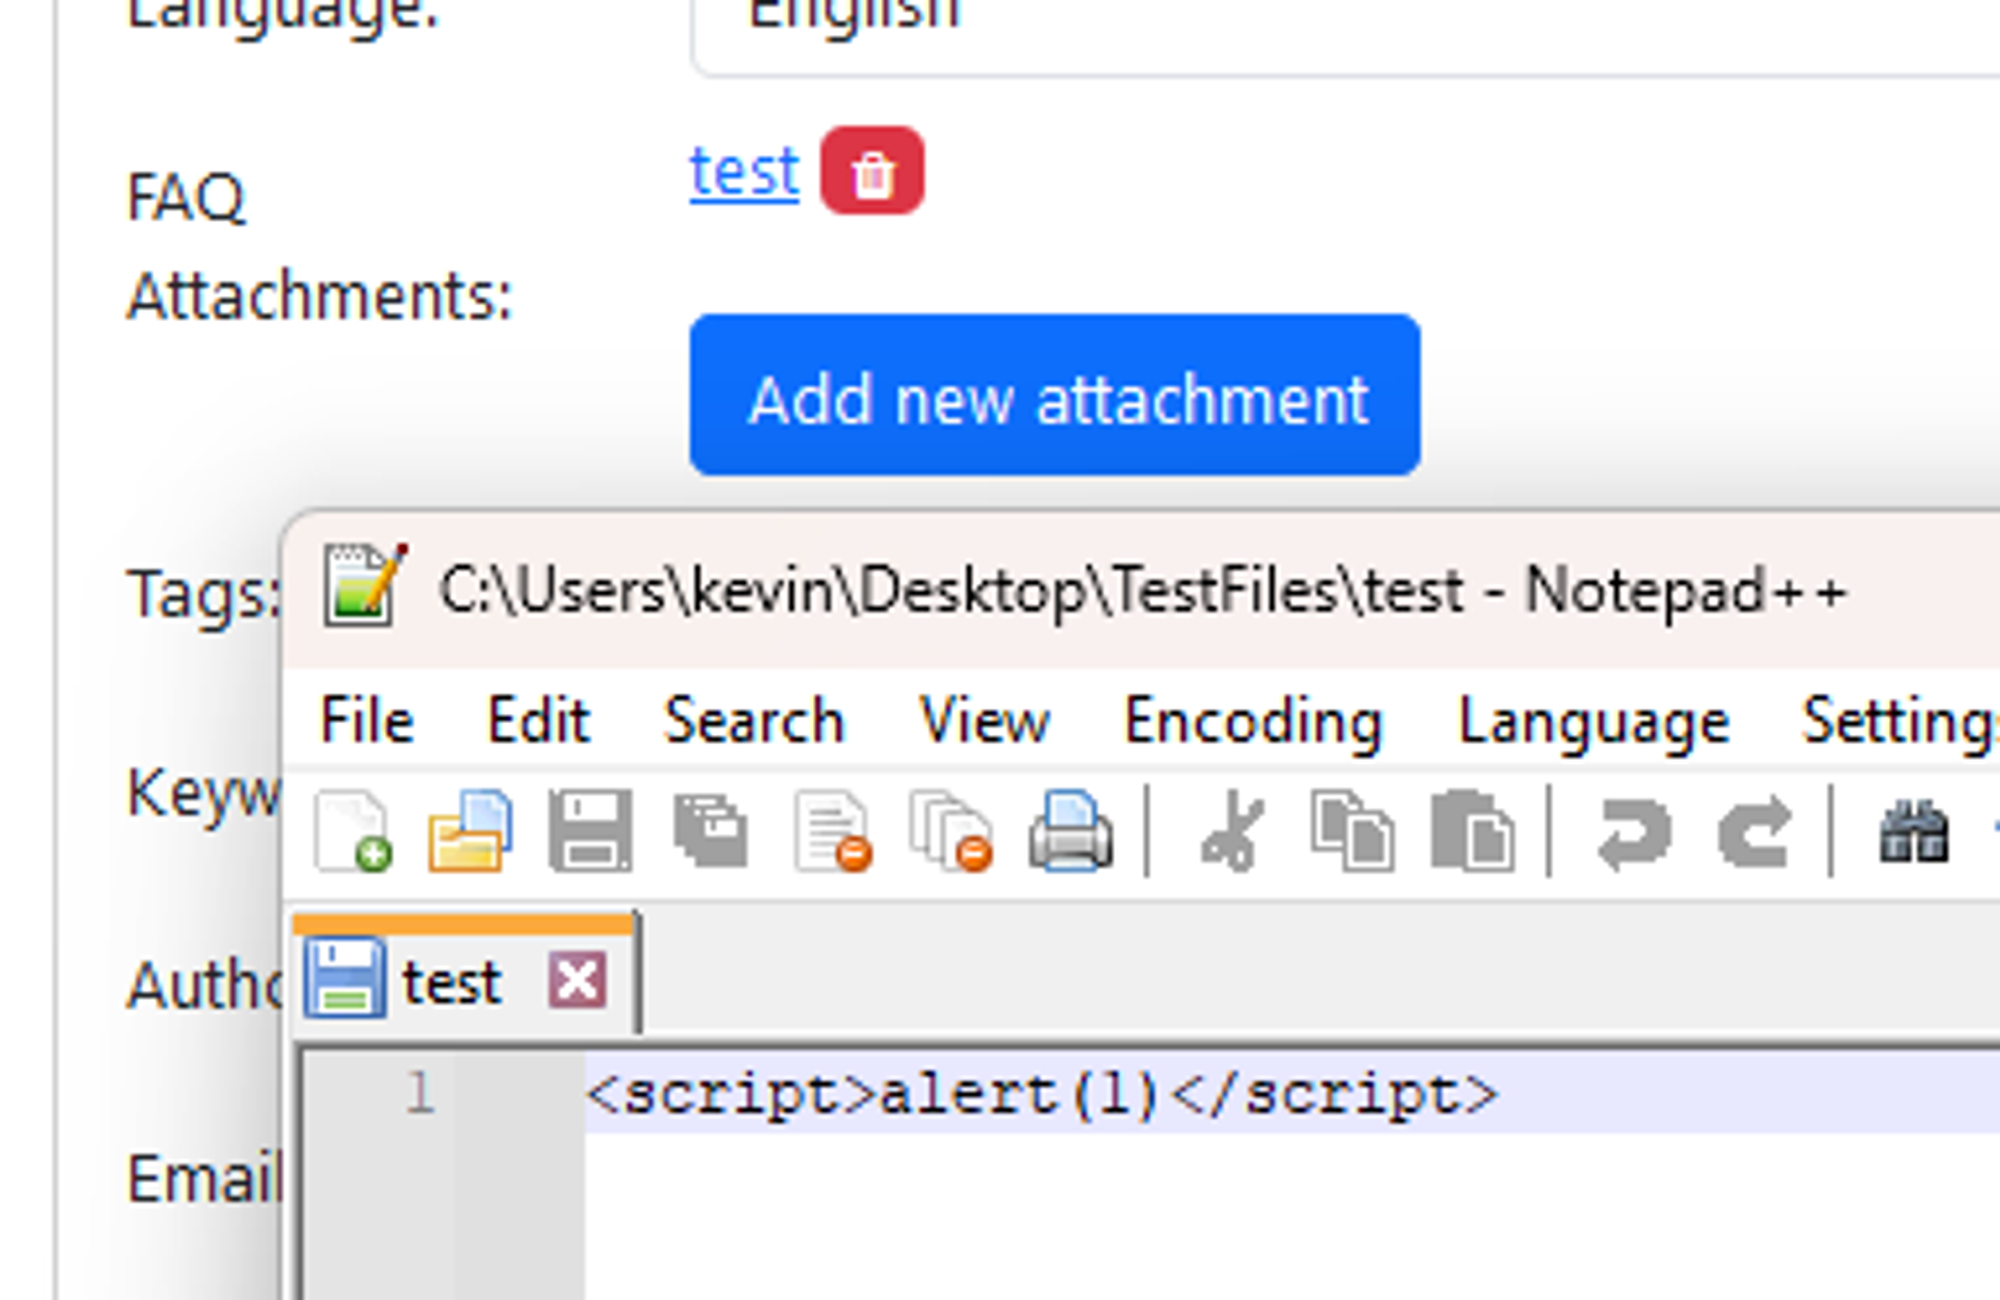\n\n2. Since the path of the uploaded file is built entirely on the file’s MD5 hash and the attachment directory, it is possible for an attacker to know the direct path of the uploaded file.\n\n E.g file MD5 hash: 38fff51cb7248a06d6142c6bdf846831\n\n URL will be: http://127.0.0.1/phpmyfaq/attachments/38fff/51cb7/248a0/6d6142c6bdf846831\n\n - /attachments\n - /38fff (first 5 chars of MD5 hash)\n - /51cb7 (next 5 chars of MD5 hash)\n - /248a0 (next 5 chars of MD5 hash)\n - /6d6142c6bdf846831 (remaining chars of MD5 hash)\n\n3. Even though the attachment was uploaded without a file extension, it is still rendered as .html, hence triggering the XSS payload.\n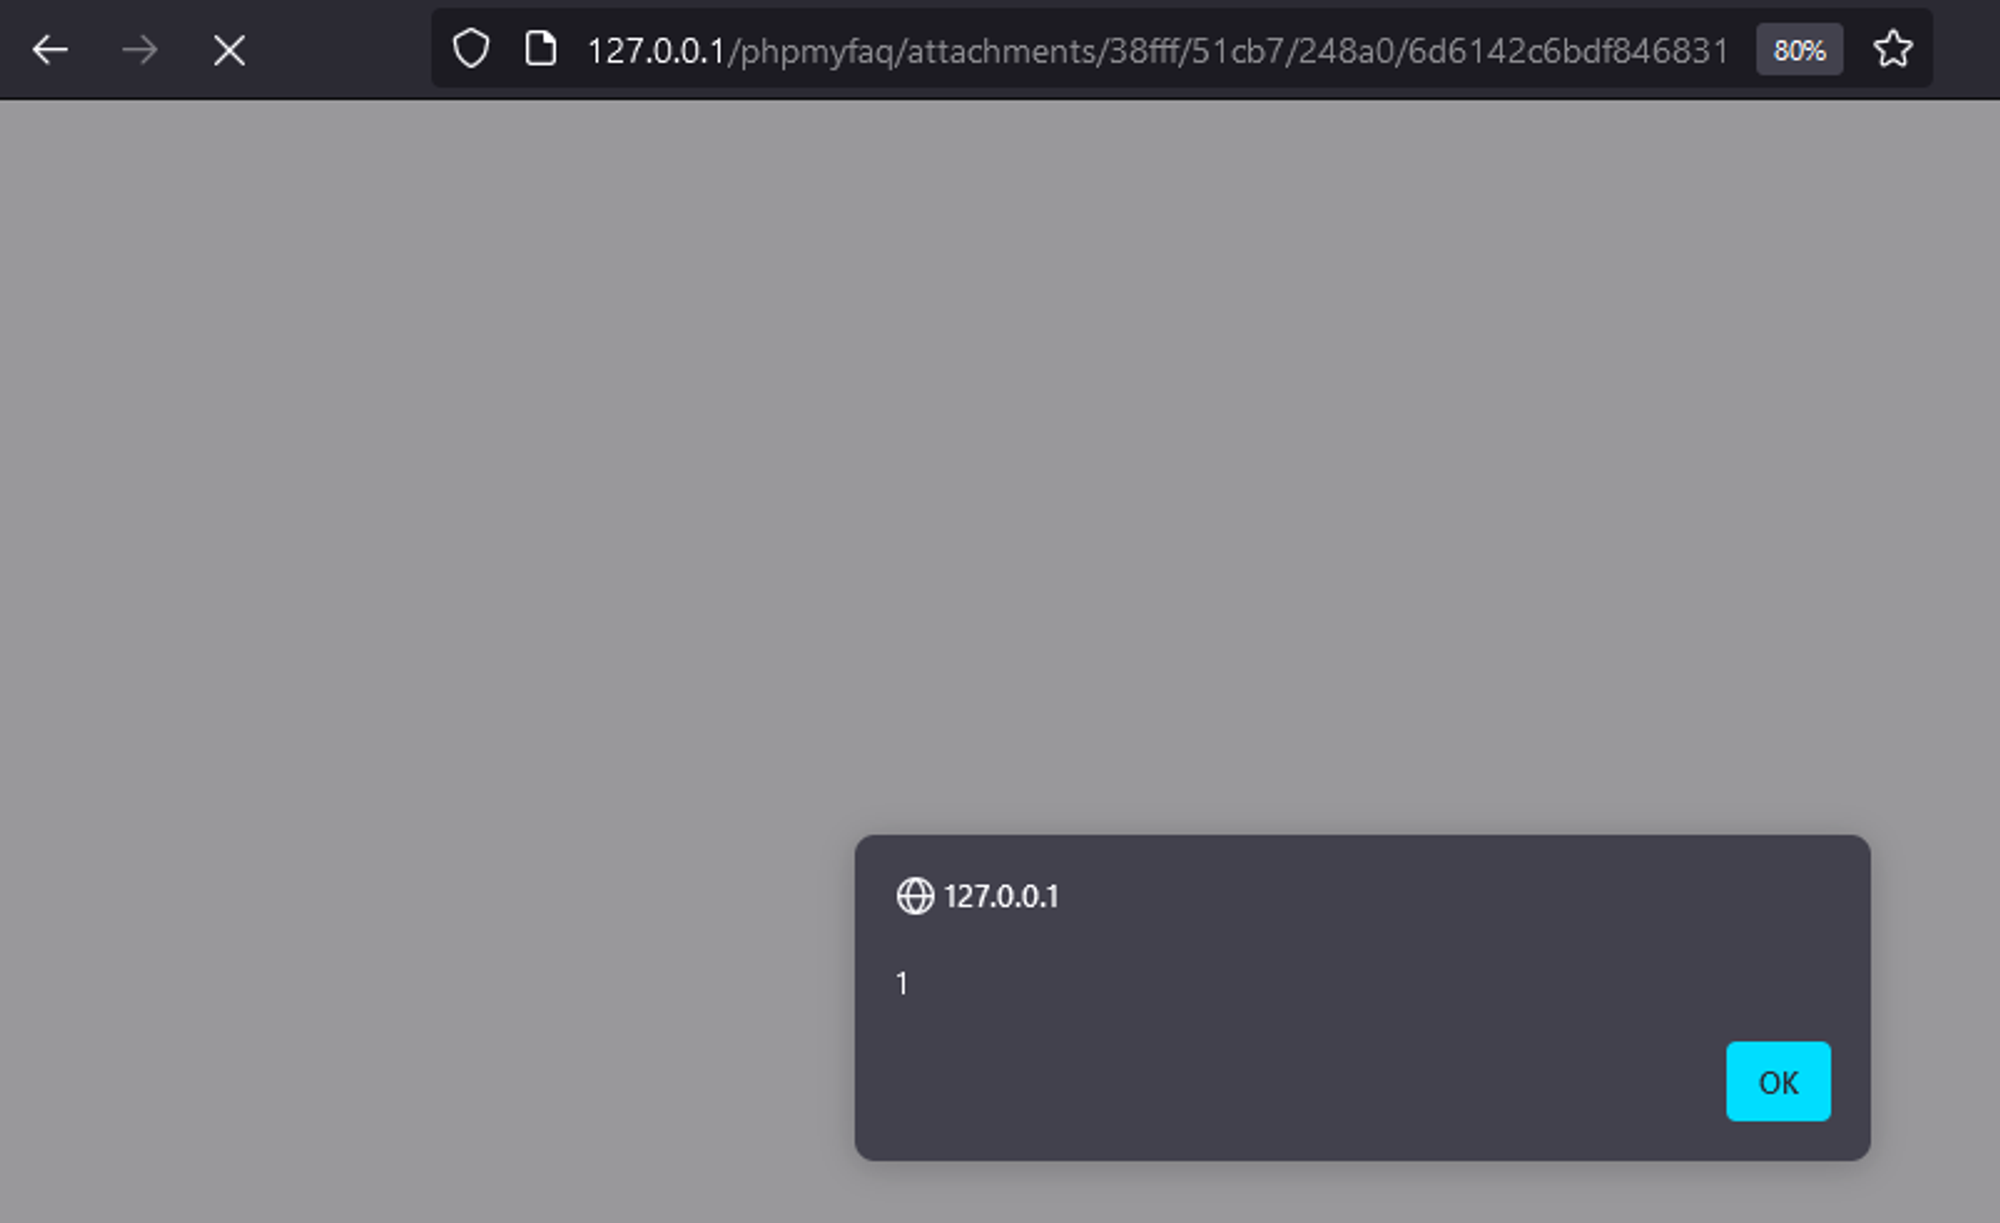\n\n### Impact\nThis allows an attacker to execute arbitrary client side JavaScript within the context of another user's phpMyFAQ session.\n\n",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:L/I:L/A:L"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Packagist",
"name" : "phpmyfaq/phpmyfaq"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "3.2.5"
}, {
"fixed" : "3.2.6"
} ]
} ],
"versions" : [ "3.2.5" ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-hm8r-95g3-5hj9"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2024-29179"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/thorsten/phpMyFAQ"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-79" ],
"severity" : "MODERATE",
"github_reviewed" : true,
"github_reviewed_at" : "2024-03-25T19:45:12Z",
"nvd_published_at" : "2024-03-25T21:15:47Z"
}
}