GHSA-fj52-5g4h-gmq8: Pyload ng PyLoad's Session Not Invalidated After Vulnerability
LOWGHSA-fj52-5g4h-gmq8 is a LOW pyload's session not invalidated after vulnerability (CWE-613: Insufficient Session Expiration) affecting Pyload ng libraries in the PyPI ecosystem. The issue involves pyload's session not invalidated after permission changes. Remediation is available in the latest vendor maintenance releases.
GHSA-fj52-5g4h-gmq8 at a Glance
How to Fix GHSA-fj52-5g4h-gmq8
To remediate this vulnerability, upgrade all affected Pyload ng dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
pip install pyload-ng>=Latest secure releaseRun the following command in your project directory to verify that all resolved dependencies use the patched release:
pip show pyload-ngHow to Check if You Are Affected
To determine whether your Python environment is affected by GHSA-fj52-5g4h-gmq8, inspect your installed packages using pip:
pip show pyload-ngAnalyze the terminal output to locate any version of Pyload ng in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than the patched release), your application is affected.
Note: The pip show pyload-ng command checks currently installed packages in your active Python environment.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-613: Insufficient Session Expiration, where according to wasc, "insufficient session expiration is when a web site permits an attacker to reuse old session credentials or session ids for authorization.". In Pyload ng, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
GHSA-fj52-5g4h-gmq8 Affected Pyload ng Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
pyload-ng
|
PyPI |
≤ 0.5.0b3.dev97
|
|
References
Frequently Asked Questions
What is GHSA-fj52-5g4h-gmq8?
Which Pyload ng versions are affected?
What version fixes GHSA-fj52-5g4h-gmq8?
Is pyload-ng affected?
What CWE is associated with GHSA-fj52-5g4h-gmq8?
How can I check PyPI dependencies for GHSA-fj52-5g4h-gmq8?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-fj52-5g4h-gmq8",
"modified" : "2026-04-14T23:39:25Z",
"published" : "2026-04-14T23:39:25Z",
"aliases" : [ ],
"summary" : "pyLoad's Session Not Invalidated After Permission Changes",
"details" : "### Summary\nThe `pyload` application does not properly invalidate or modify sessions upon changes made to a user's permissions.\n\n### Details\nWhenever an administrator changes the permissions a specific account has, they do not expect that account still being able to access data that their new permissions do not allow. This is not the case for the `pyload` application, as a user with a valid session can still perform the actions.\n\n### PoC\nTake a user with all the permissions, as shown below.\n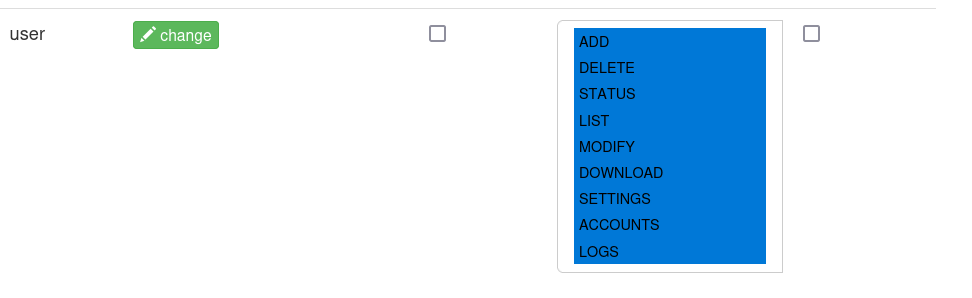\n\nWe now log in as this user.\n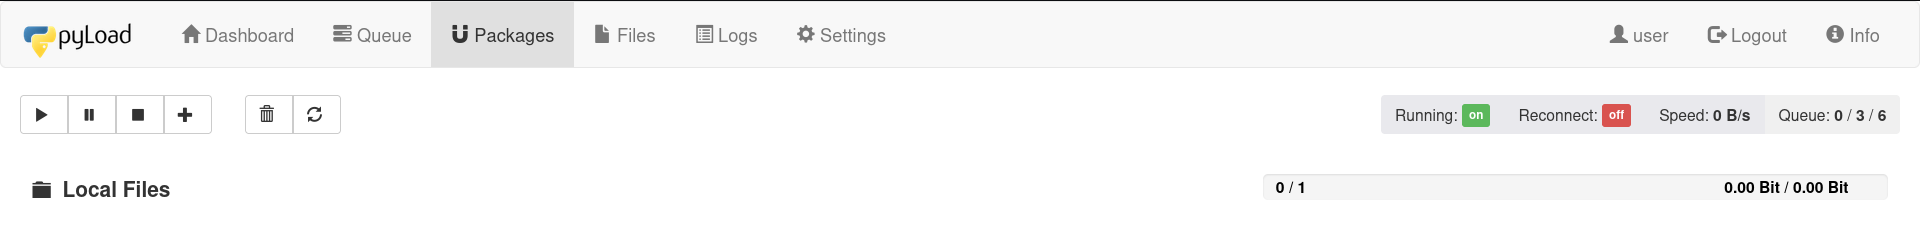\n\nLet us now take away all the permissions.\n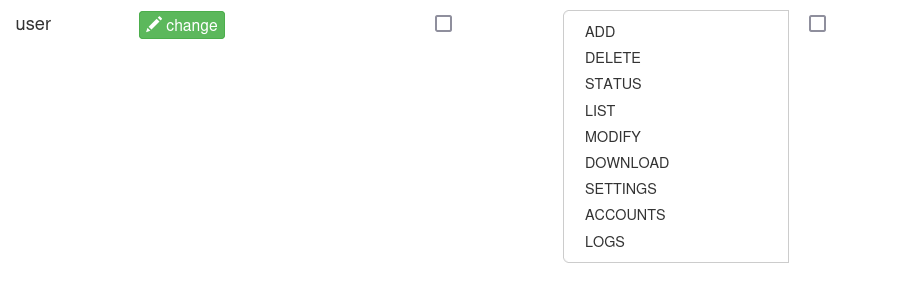\n\nThe logged in session can still be used to access everything in the application.\n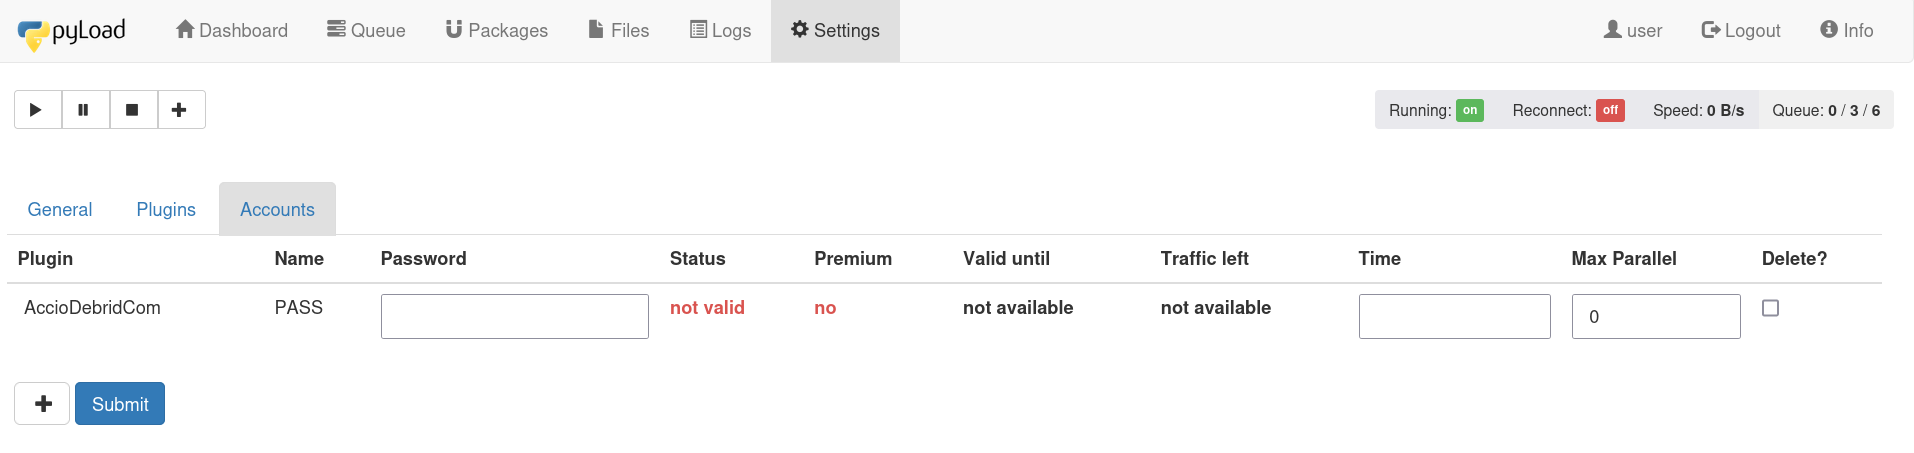\n\n### Impact\nShould permissions be taken away, then the user is expected not to be able to execute the actions belonging to those actions anymore.",
"severity" : [ {
"type" : "CVSS_V4",
"score" : "CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:N/VC:L/VI:L/VA:N/SC:N/SI:N/SA:N/E:P"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "PyPI",
"name" : "pyload-ng"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "0"
}, {
"last_affected" : "0.5.0b3.dev97"
} ]
} ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/pyload/pyload/security/advisories/GHSA-fj52-5g4h-gmq8"
}, {
"type" : "WEB",
"url" : "https://github.com/pyload/pyload/commit/e95804fb0d06cbb07d2ba380fc494d9ff89b68c1"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/pyload/pyload"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-613" ],
"severity" : "LOW",
"github_reviewed" : true,
"github_reviewed_at" : "2026-04-14T23:39:25Z",
"nvd_published_at" : null
}
}