CVE-2026-52796: Gogs.io/gogs Denial of Service Vulnerability
LOWCVE-2026-52796 is a LOW (CVSS 3.5) denial of service vulnerability (CWE-1336: Improper Neutralization of Special Elements Used in a Template Engine) affecting Gogs.io/gogs libraries in the Go ecosystem. The issue involves gogs has dos in rendering issue index pattern. Remediation is available by upgrading affected packages to version 0.14.3.
CVE-2026-52796 at a Glance
Security Impact
CVSS: 3.5
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:N/A:L).
How to Fix CVE-2026-52796
To remediate this vulnerability, upgrade all affected Gogs.io/gogs dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade gogs.io/gogs to 0.14.3Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for gogs.io/gogsHow to Check if You Are Affected
To determine whether your application is affected by CVE-2026-52796, inspect your project dependencies for Gogs.io/gogs:
inspect dependencies for gogs.io/gogsAnalyze the terminal output to locate any version of Gogs.io/gogs in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 0.14.3), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-1336: Improper Neutralization of Special Elements Used in a Template Engine, where the product uses a template engine to insert or process externally-influenced input, but it does not neutralize or incorrectly neutralizes special elements or syntax that can be interpreted as template expressions or other code directives when processed by the engine. In Gogs.io/gogs, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2026-52796 Affected Gogs.io/gogs Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
gogs.io/gogs
|
Go |
< 0.14.3
|
0.14.3
|
References
Frequently Asked Questions
What is CVE-2026-52796?
Which Gogs.io/gogs versions are affected?
What version fixes CVE-2026-52796?
Is gogs.io/gogs affected?
What is the CVSS score of CVE-2026-52796?
What CWE is associated with CVE-2026-52796?
How can I check Go dependencies for CVE-2026-52796?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-4j89-2c4f-44c6",
"modified" : "2026-07-21T13:17:05Z",
"published" : "2026-06-22T23:58:17Z",
"aliases" : [ "CVE-2026-52796" ],
"summary" : "Gogs has DoS in rendering issue index pattern",
"details" : "### Summary\nSpecial template of issue index pattern may cause panic.\n\n### Details\n\nin internal/markup/markup.go\n\n```go\nlink = fmt.Sprintf(`<a href=\"%s\">%s</a>`, com.Expand(metas[\"format\"], metas), m)\n```\n\nIssue index pattern is rendered to link with `com.Expand`.\n\nHowever, `com.Expand` is not safe.\n\n```go\ni = strings.Index(template, \"}\")\nif s, ok := match[template[:i]]; ok {\n```\n\nwhen `{` is found but `}` not found, i comes to 1, template[:-1] will be called, and then panicked\n\n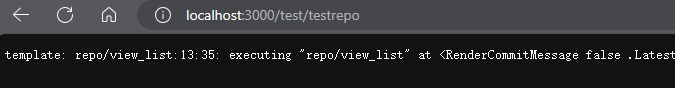\n\nfinally, all pages than contains issue index are unavailable.\n\n### PoC\n\n1. set issue index pattern as follow\n\n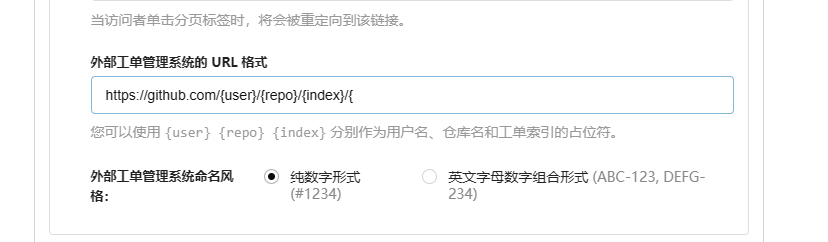\n\n2. add a commit which point to an issue in its msg\n\n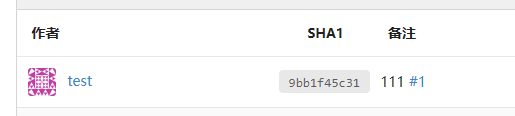\n\nusing `#1` above\n\n### Impact\n\nDoS that cause part of pages of the specify repo unavailable.",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:N/A:L"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Go",
"name" : "gogs.io/gogs"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "0"
}, {
"fixed" : "0.14.3"
} ]
} ],
"database_specific" : {
"last_known_affected_version_range" : "<= 0.14.2"
}
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/gogs/gogs/security/advisories/GHSA-4j89-2c4f-44c6"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2026-52796"
}, {
"type" : "WEB",
"url" : "https://github.com/gogs/gogs/pull/8312"
}, {
"type" : "WEB",
"url" : "https://github.com/gogs/gogs/commit/0529d95fc39f2b6d2997b19a2a12e24522684722"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/gogs/gogs"
}, {
"type" : "WEB",
"url" : "https://github.com/gogs/gogs/releases/tag/v0.14.3"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-1336" ],
"severity" : "LOW",
"github_reviewed" : true,
"github_reviewed_at" : "2026-06-22T23:58:17Z",
"nvd_published_at" : "2026-06-24T21:16:55Z"
}
}