CVE-2024-28107: Phpmyfaq/phpmyfaq SQL Injection Vulnerability
HIGHCVE-2024-28107 is a HIGH (CVSS 8.8) sql injection vulnerability (CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')) affecting Phpmyfaq/phpmyfaq libraries in the Packagist ecosystem. The issue involves phpmyfaq sql injections at insertentry & saveentry. Remediation is available by upgrading affected packages to version 3.2.6.
CVE-2024-28107 at a Glance
Security Impact
CVSS: 8.8
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H).
How to Fix CVE-2024-28107
To remediate this vulnerability, upgrade all affected Phpmyfaq/phpmyfaq dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade phpmyfaq/phpmyfaq to 3.2.6Run the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for phpmyfaq/phpmyfaqHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-28107, inspect your project dependencies for Phpmyfaq/phpmyfaq:
inspect dependencies for phpmyfaq/phpmyfaqAnalyze the terminal output to locate any version of Phpmyfaq/phpmyfaq in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 3.2.6), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection'), where the product constructs all or part of an sql command using externally-influenced input from an upstream component, but it does not neutralize or incorrectly neutralizes special elements that could modify the intended sql command when it is sent to a downstream component. without sufficient removal or quoting of sql syntax in user-controllable inputs, the generated sql query can cause those inputs to be interpreted as sql instead of ordinary user data. In Phpmyfaq/phpmyfaq, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-28107 Affected Phpmyfaq/phpmyfaq Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
phpmyfaq/phpmyfaq
|
Packagist |
≥ 3.2.5
< 3.2.6
All 1 versions
3.2.5
|
3.2.6
|
References
Frequently Asked Questions
What is CVE-2024-28107?
Which Phpmyfaq/phpmyfaq versions are affected?
What version fixes CVE-2024-28107?
Is phpmyfaq/phpmyfaq affected?
What is the CVSS score of CVE-2024-28107?
What CWE is associated with CVE-2024-28107?
How can I check Packagist dependencies for CVE-2024-28107?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-2grw-mc9r-822r",
"modified" : "2024-03-25T22:28:09Z",
"published" : "2024-03-25T19:45:37Z",
"aliases" : [ "CVE-2024-28107" ],
"summary" : "phpMyFAQ SQL injections at insertentry & saveentry",
"details" : "### Summary\nA SQL injection vulnerability has been discovered in the `insertentry` & `saveentry` when modifying records due to improper escaping of the email address. This allows any authenticated user with the rights to add/edit FAQ news to exploit this vulnerability to exfiltrate data, take over accounts and in some cases, even achieve RCE.\n\n### PoC 1 - SQL Injection at insertentry:\n1. Browse to “/admin/?action=editentry”, edit record and save. Intercept the POST request to \"/admin/?action=insertentry\" and modify the email and notes parameters in the body to the payloads below:\n a. `email=test'/*@email.com`\n b. `notes=*/,1,1,1,1,null,1);select+pg_sleep(5)--`\n\n2. Send the request and notice the `pg_sleep(5)` command is executed with a time delay of 5 seconds in the response. This verifies that the SQL injection vulnerability exists. \n 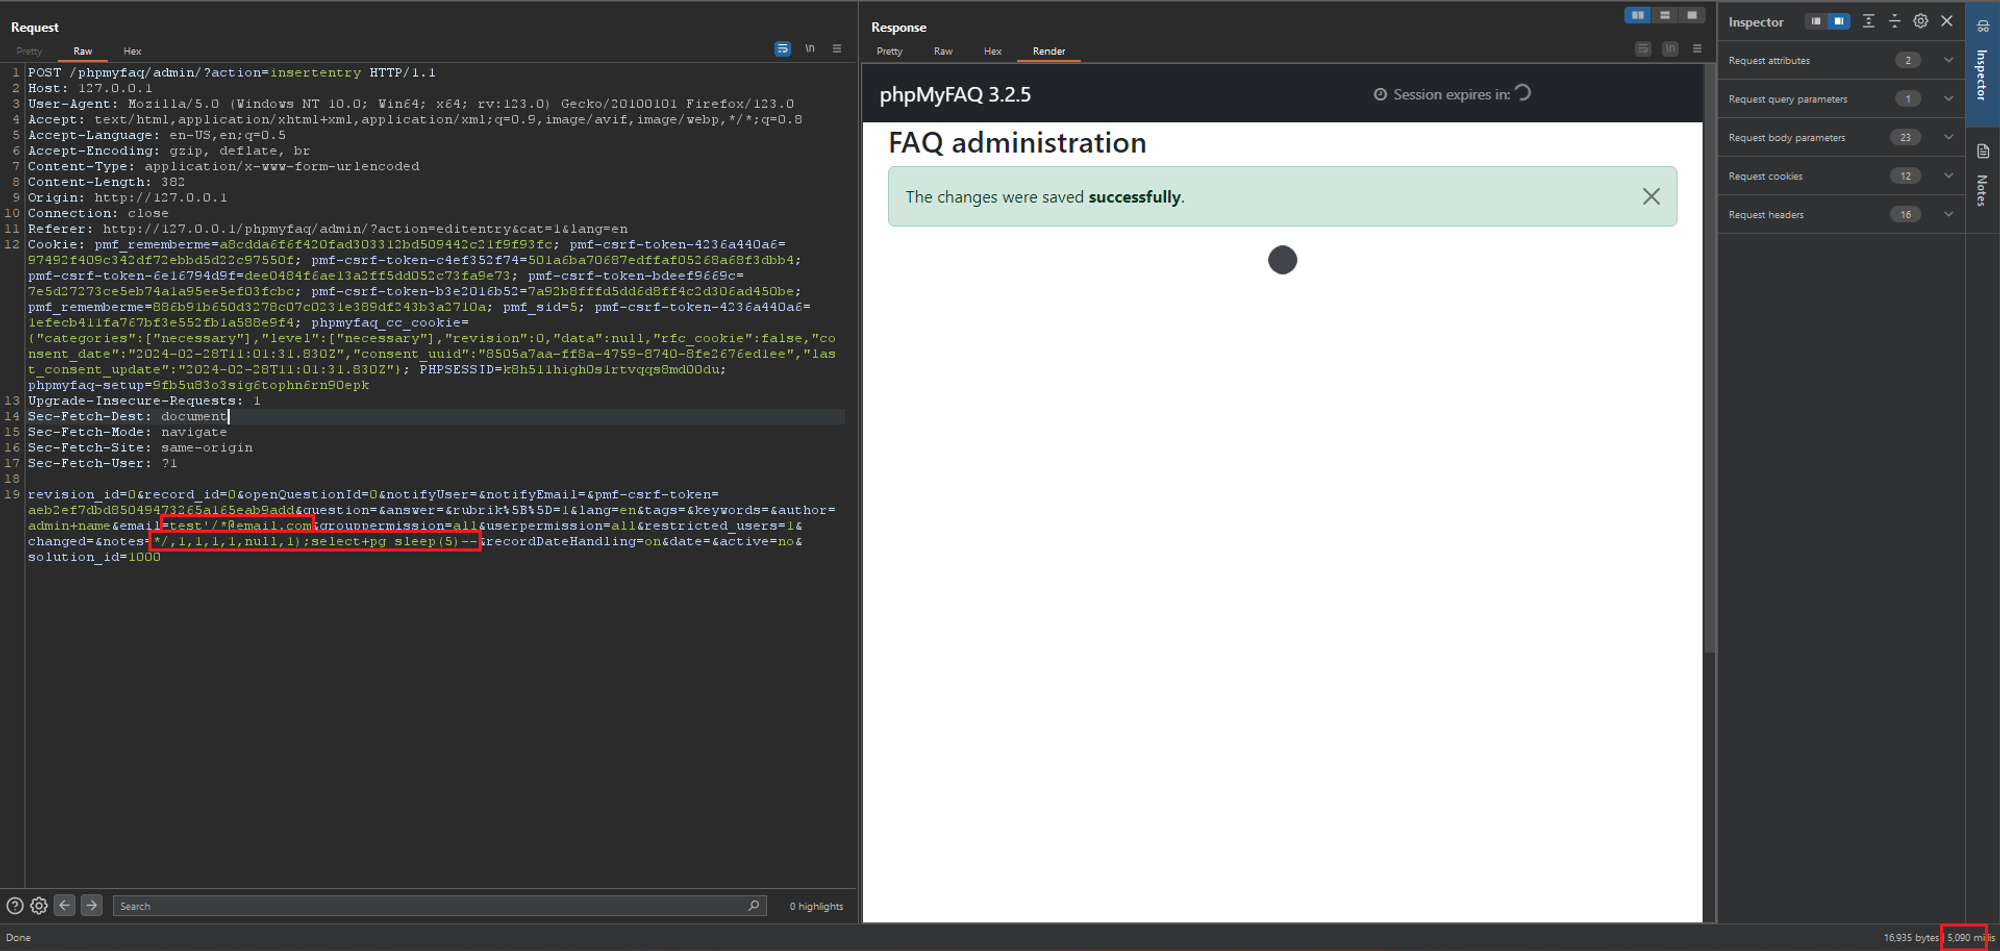\n\n### PoC 2 - SQL Injection at saveentry\n1. Browse to “/admin/?action=editentry”, edit record and save. Intercept the POST request to \"/admin/?action=saveentry\" and modify the email and notes parameters in the body to the payloads below:\n a. `email=test'/*@email.com`\n b. `*/,notes=(select+pg_sleep(5))--`\n 2. Send the request and notice the `pg_sleep(5)` command is executed with a time delay of 5 seconds in the response. This verifies that the SQL injection vulnerability exists.\n 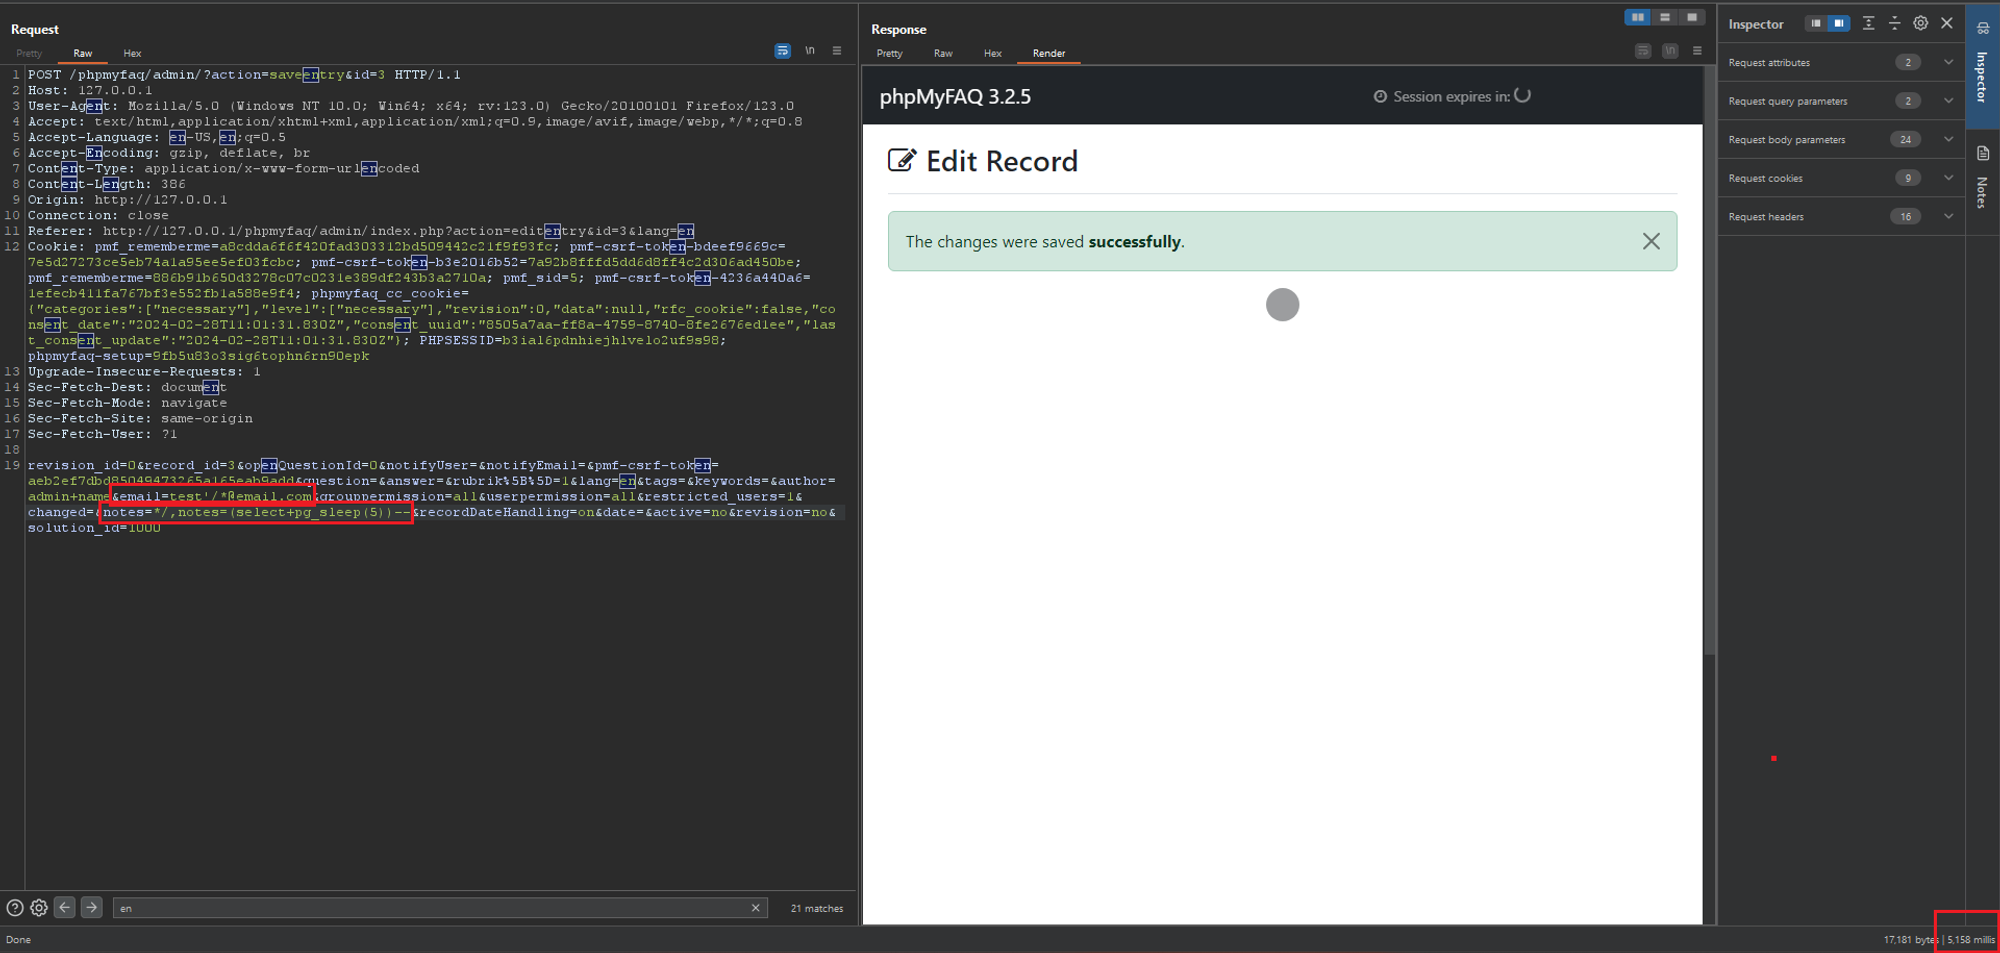\n\n\n### Impact\nThe SQL injection vulnerability discovered allows authenticated users with appropriate privileges to execute malicious SQL queries, potentially leading to data exfiltration, account takeover, and even remote code execution. Attackers can exploit the vulnerability to read sensitive data from the database, such as user credentials and system files, compromising the confidentiality and integrity of the system. Moreover, successful exploitation may enable attackers to gain unauthorized access to user accounts or execute arbitrary commands on the server, impacting both system administrators and end users.",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Packagist",
"name" : "phpmyfaq/phpmyfaq"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "3.2.5"
}, {
"fixed" : "3.2.6"
} ]
} ],
"versions" : [ "3.2.5" ]
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-2grw-mc9r-822r"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2024-28107"
}, {
"type" : "WEB",
"url" : "https://github.com/thorsten/phpMyFAQ/commit/d0fae62a72615d809e6710861c1a7f67ac893007"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/thorsten/phpMyFAQ"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-89" ],
"severity" : "HIGH",
"github_reviewed" : true,
"github_reviewed_at" : "2024-03-25T19:45:37Z",
"nvd_published_at" : "2024-03-25T19:15:58Z"
}
}