CVE-2024-27288: Github.com/1Panel dev/1Panel Remote Code Execution Vulnerability
MODERATECVE-2024-27288 is a MODERATE (CVSS 6.3) remote code execution vulnerability (CWE-863: Incorrect Authorization) affecting Github.com/1Panel dev/1Panel libraries in the Go ecosystem. The issue involves 1panel open source panel project has an unauthorized vulnerability.. Remediation is available by upgrading affected packages to version 1.10.1-lts.
CVE-2024-27288 at a Glance
Security Impact
CVSS: 6.3
The security impact metrics below are parsed directly from the CVSS v3.1 vector string (CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L).
How to Fix CVE-2024-27288
To remediate this vulnerability, upgrade all affected Github.com/1Panel dev/1Panel dependencies to a patched release. Both direct and transitive dependencies should be checked, as frameworks or security libraries may pull in vulnerable versions transitively.
Upgrade github.com/1Panel-dev/1Panel to 1.10.1-ltsRun the following command in your project directory to verify that all resolved dependencies use the patched release:
inspect dependencies for github.com/1Panel-dev/1PanelHow to Check if You Are Affected
To determine whether your application is affected by CVE-2024-27288, inspect your project dependencies for Github.com/1Panel dev/1Panel:
inspect dependencies for github.com/1Panel-dev/1PanelAnalyze the terminal output to locate any version of Github.com/1Panel dev/1Panel in your dependency tree. If any resolved version matches the vulnerable ranges listed in the table below (for example, versions earlier than 1.10.1-lts), your application is affected.
Note: Verify declared build manifests and deployed runtime container environments.
Technical Details
Vulnerability Mechanism & Technical Analysis
This vulnerability is classified under CWE-863: Incorrect Authorization, where the product performs an authorization check when an actor attempts to access a resource or perform an action, but it does not correctly perform the check. In Github.com/1Panel dev/1Panel, software state validation or input boundaries are circumvented during processing. Review the official source advisory statement below for specific affected components, classes, and reproduction details.
Source Advisory Statement
CVE-2024-27288 Affected Github.com/1Panel dev/1Panel Versions
1 component(s)| Product / Package | Ecosystem | Affected Versions | Fixed Version |
|---|---|---|---|
|
github.com/1Panel-dev/1Panel
|
Go |
< 1.10.1-lts
|
1.10.1-lts
|
References
Frequently Asked Questions
What is CVE-2024-27288?
Which Github.com/1Panel dev/1Panel versions are affected?
What version fixes CVE-2024-27288?
Is github.com/1Panel-dev/1Panel affected?
What is the CVSS score of CVE-2024-27288?
What CWE is associated with CVE-2024-27288?
How can I check Go dependencies for CVE-2024-27288?
Machine-readable OSV JSON
OSV v1.5 Schema
{
"schema_version" : "1.4.0",
"id" : "GHSA-26w3-q4j8-4xjp",
"modified" : "2025-02-11T19:03:36Z",
"published" : "2024-03-06T15:29:11Z",
"aliases" : [ "CVE-2024-27288" ],
"summary" : "1Panel open source panel project has an unauthorized vulnerability.",
"details" : "### Impact\n\nThe steps are as follows:\n\n1. Access https://IP:PORT/ in the browser, which prompts the user to access with a secure entry point.\n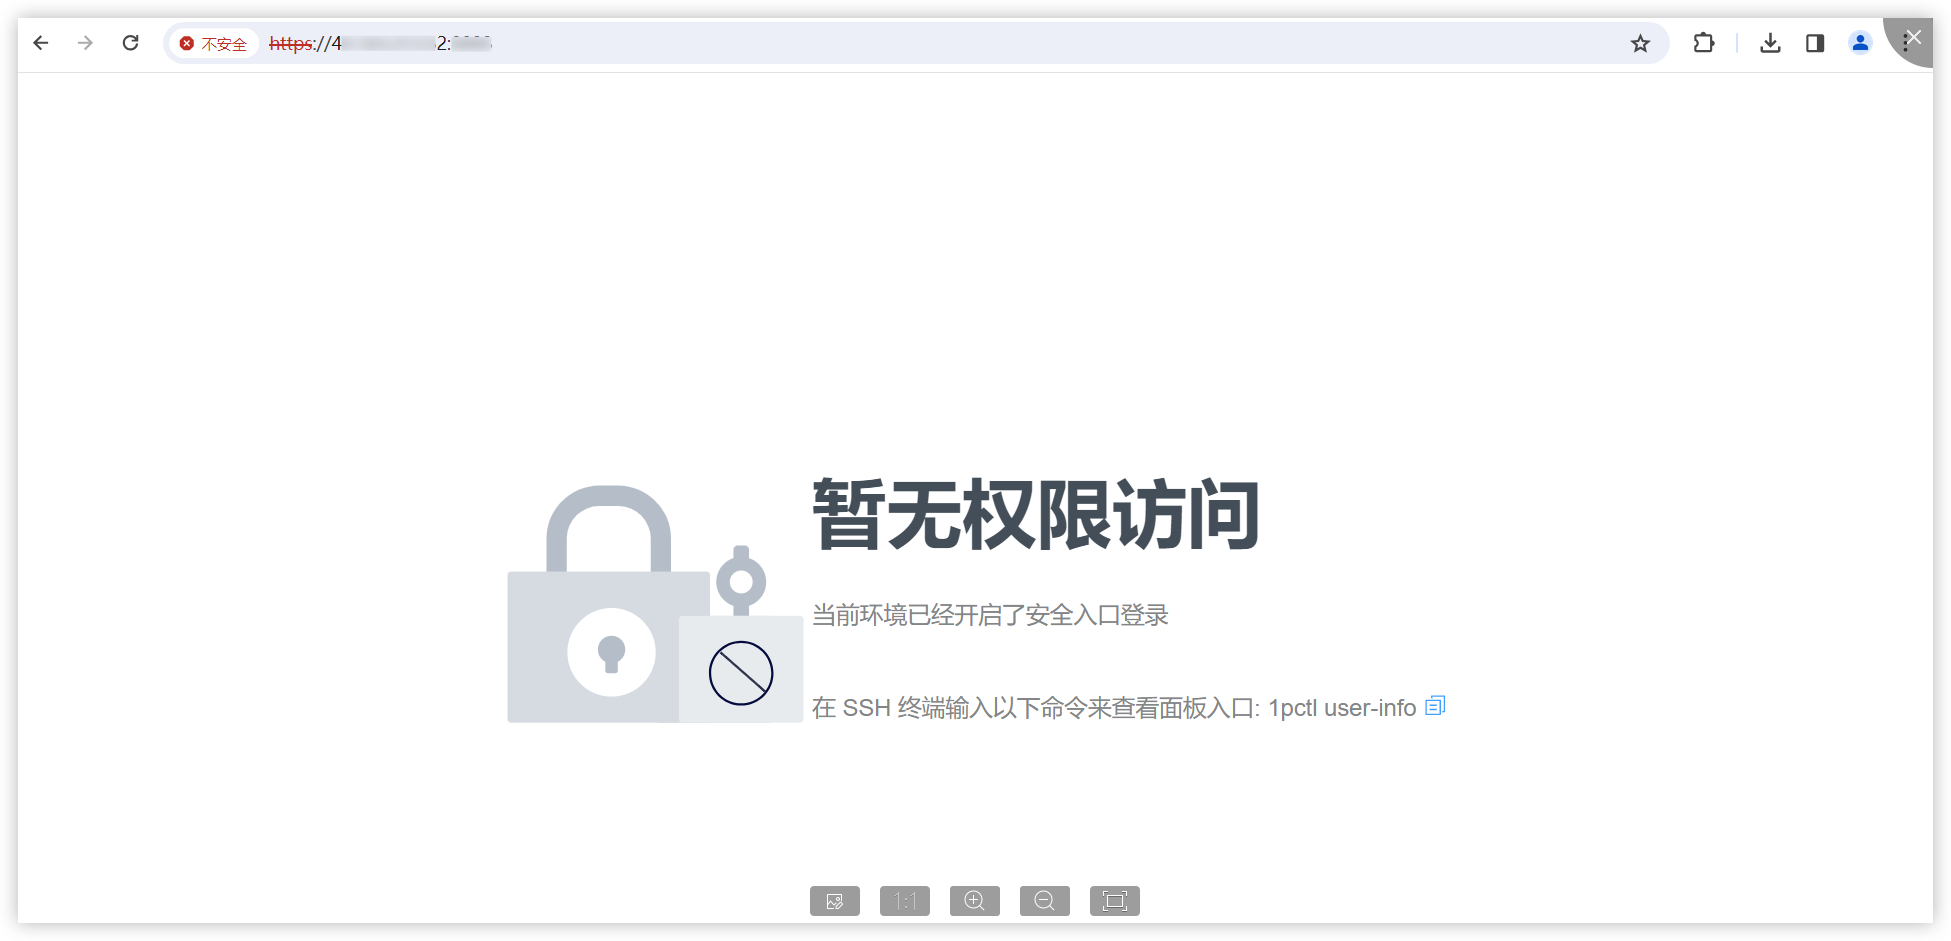\n\n2. Use Burp to intercept:\n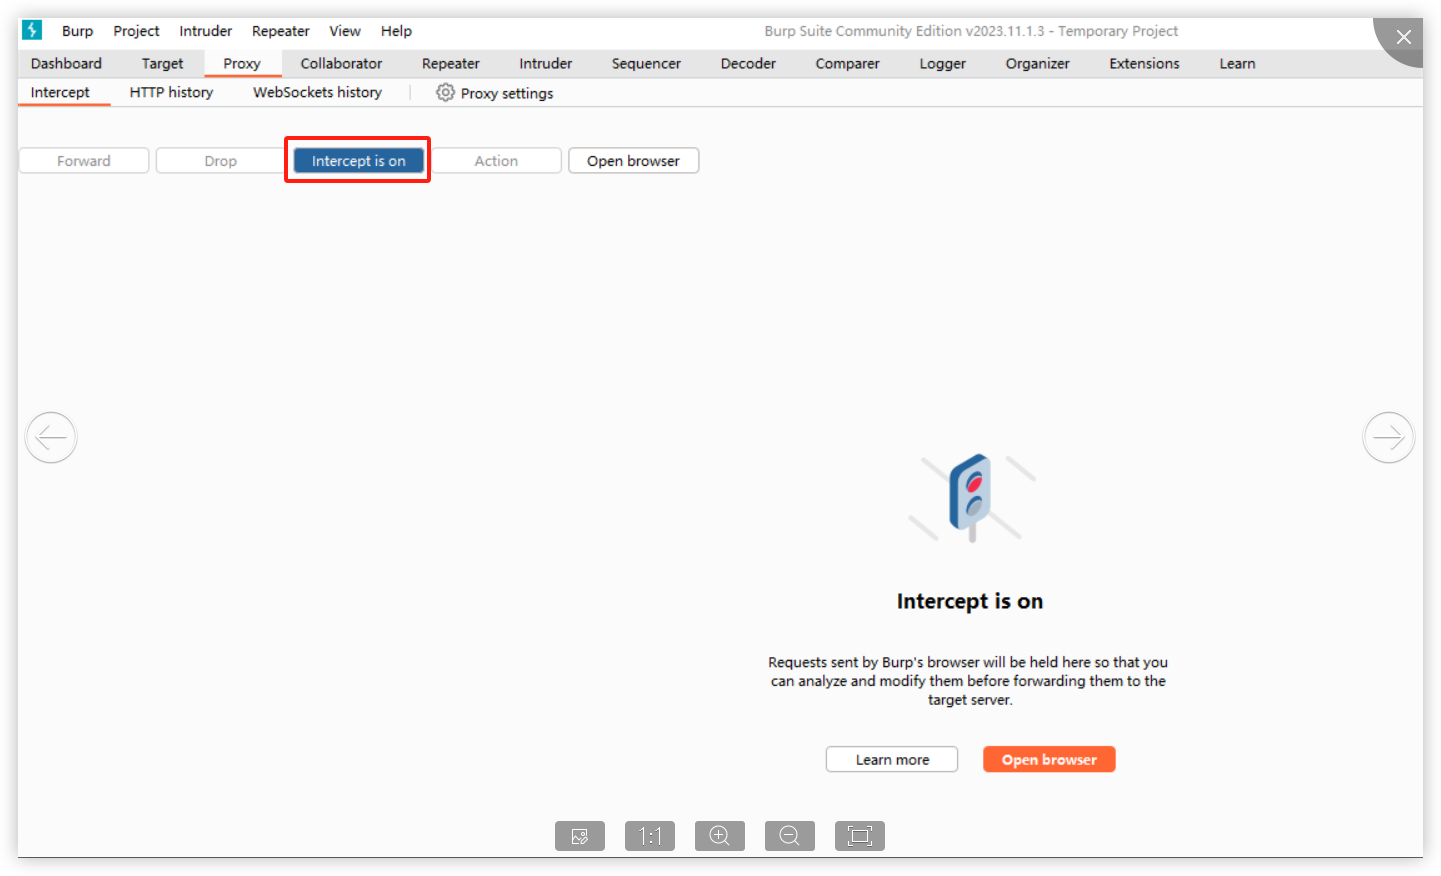\n\nWhen opening the browser and entering the URL (allowing the first intercepted packet through Burp), the following is displayed:\n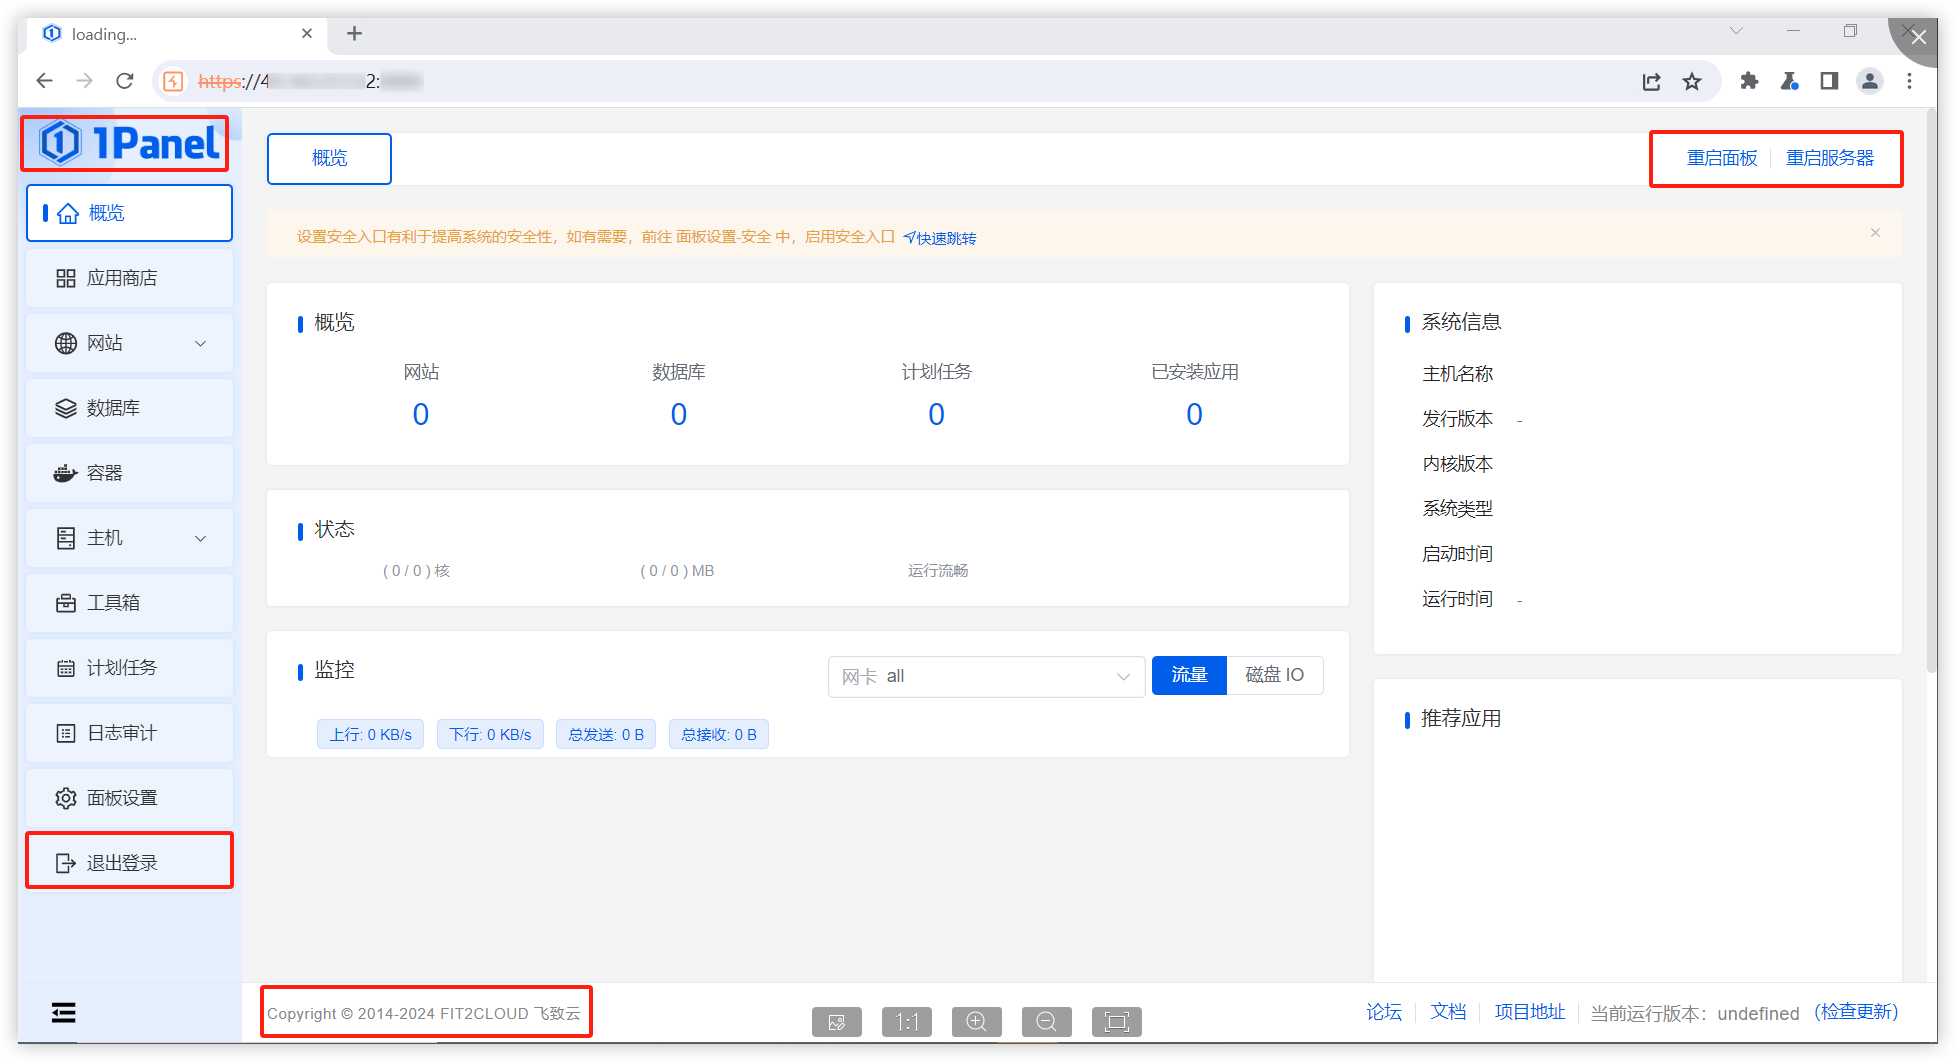\n\nIt is found that in this situation, we can access the console page (although no data is returned and no modification operations can be performed).\"\n\nAffected versions: <= 1.10.0-lts\n\n### Patches\n\nThe vulnerability has been fixed in v1.10.1-lts.\n\n### Workarounds\n\nIt is recommended to upgrade the version to 1.10.1-lts.\n\n### References\n\nIf you have any questions or comments about this advisory:\n\nOpen an issue in https://github.com/1Panel-dev/1Panel\nEmail us at wanghe@fit2cloud.com",
"severity" : [ {
"type" : "CVSS_V3",
"score" : "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L"
} ],
"affected" : [ {
"package" : {
"ecosystem" : "Go",
"name" : "github.com/1Panel-dev/1Panel"
},
"ranges" : [ {
"type" : "ECOSYSTEM",
"events" : [ {
"introduced" : "0"
}, {
"fixed" : "1.10.1-lts"
} ]
} ],
"database_specific" : {
"last_known_affected_version_range" : "<= 1.10.0-lts"
}
} ],
"references" : [ {
"type" : "WEB",
"url" : "https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp"
}, {
"type" : "ADVISORY",
"url" : "https://nvd.nist.gov/vuln/detail/CVE-2024-27288"
}, {
"type" : "WEB",
"url" : "https://github.com/1Panel-dev/1Panel/pull/4014"
}, {
"type" : "PACKAGE",
"url" : "https://github.com/1Panel-dev/1Panel"
}, {
"type" : "WEB",
"url" : "https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts"
} ],
"database_specific" : {
"cwe_ids" : [ "CWE-863" ],
"severity" : "MODERATE",
"github_reviewed" : true,
"github_reviewed_at" : "2024-03-06T15:29:11Z",
"nvd_published_at" : "2024-03-06T19:15:07Z"
}
}